App Compromise vs Host Compromise: What Changes
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
Found 562 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
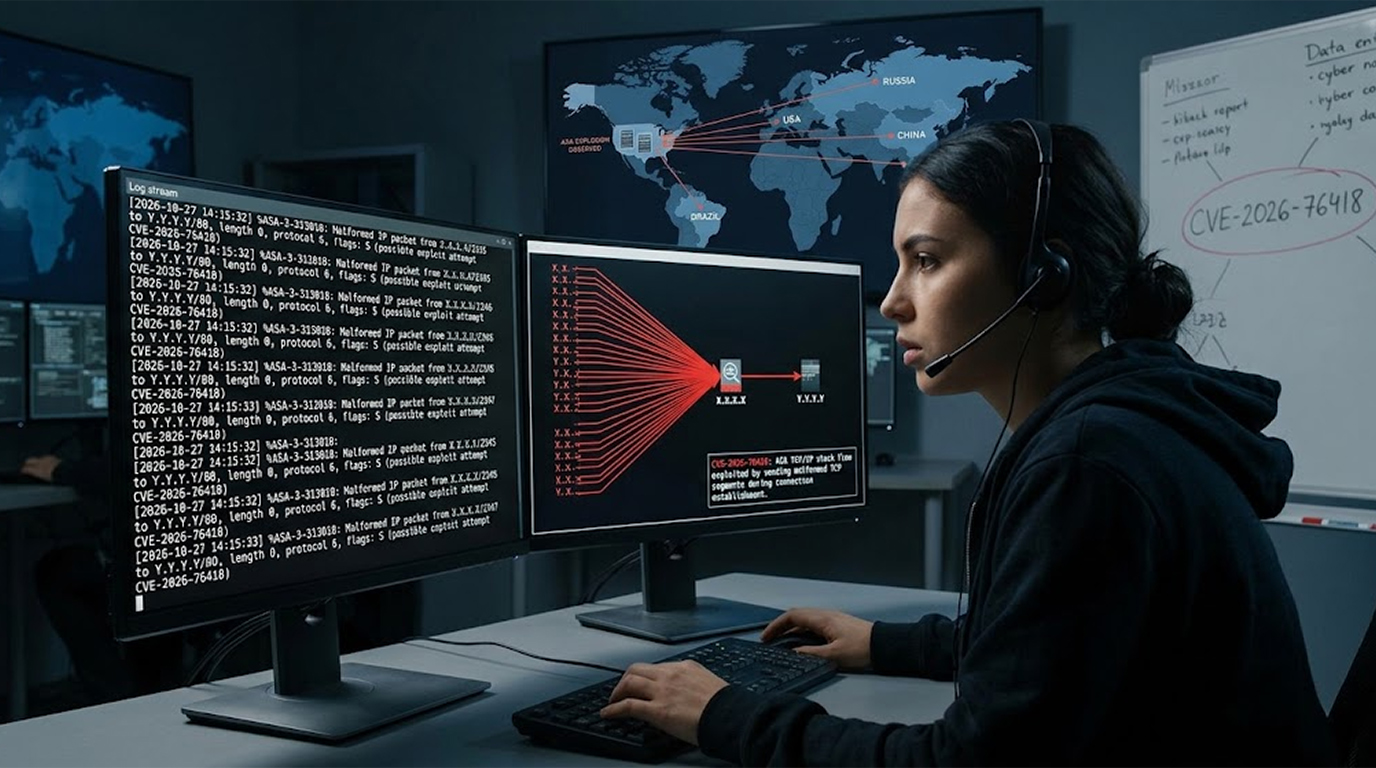
Cisco just confirmed that a high-severity flaw in its Secure Firewall ASA and FTD software is being exploited in the wild, and if you are running SSL remot...
Every engineering team has a version of the same message in their incident channel, which is a screenshot of an error, a timestamp, and the words "it crash...
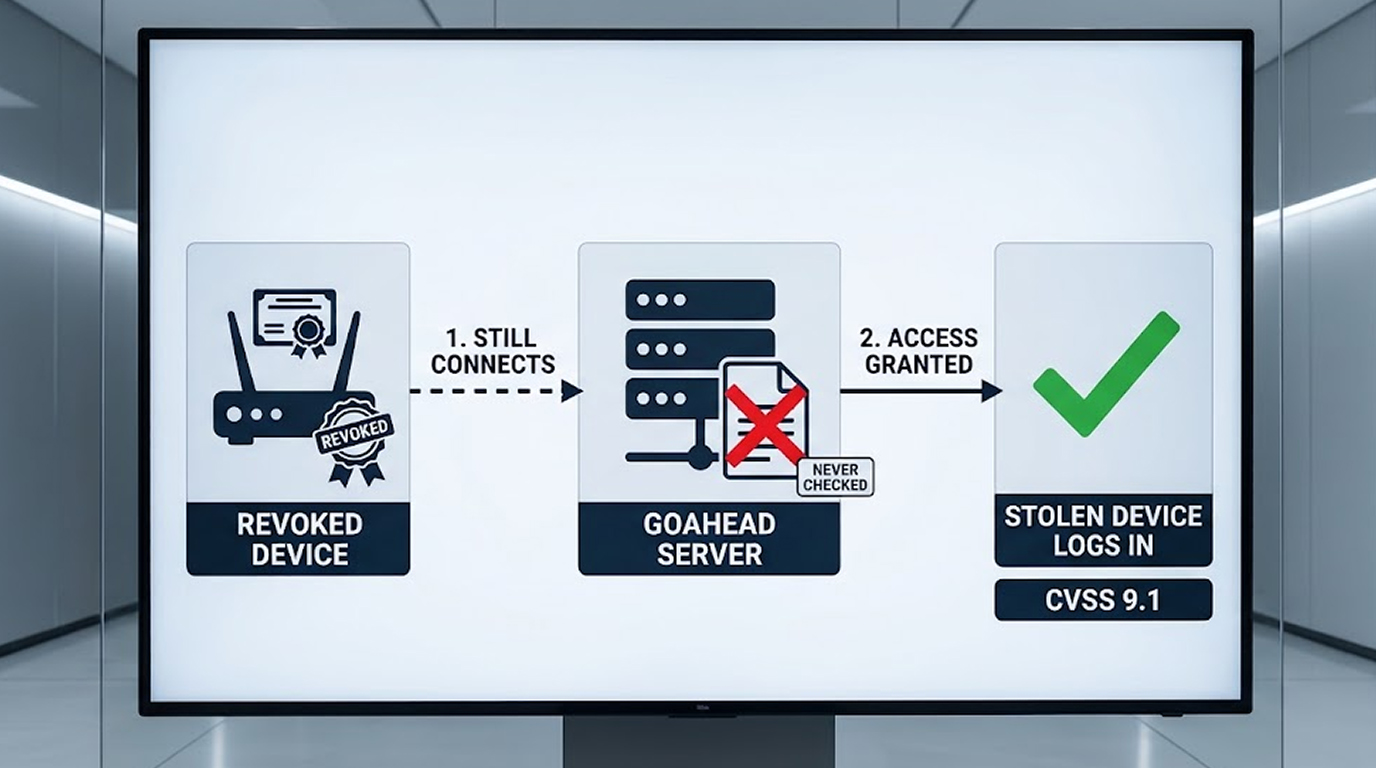
Your router, printer, or industrial controller might be accepting logins from stolen or retired devices, because a critical flaw in the GoAhead embedded we...
Yes, you can audit your own website security, and for most small sites you should. A DIY website security audit covers the basics that stop the majority of...
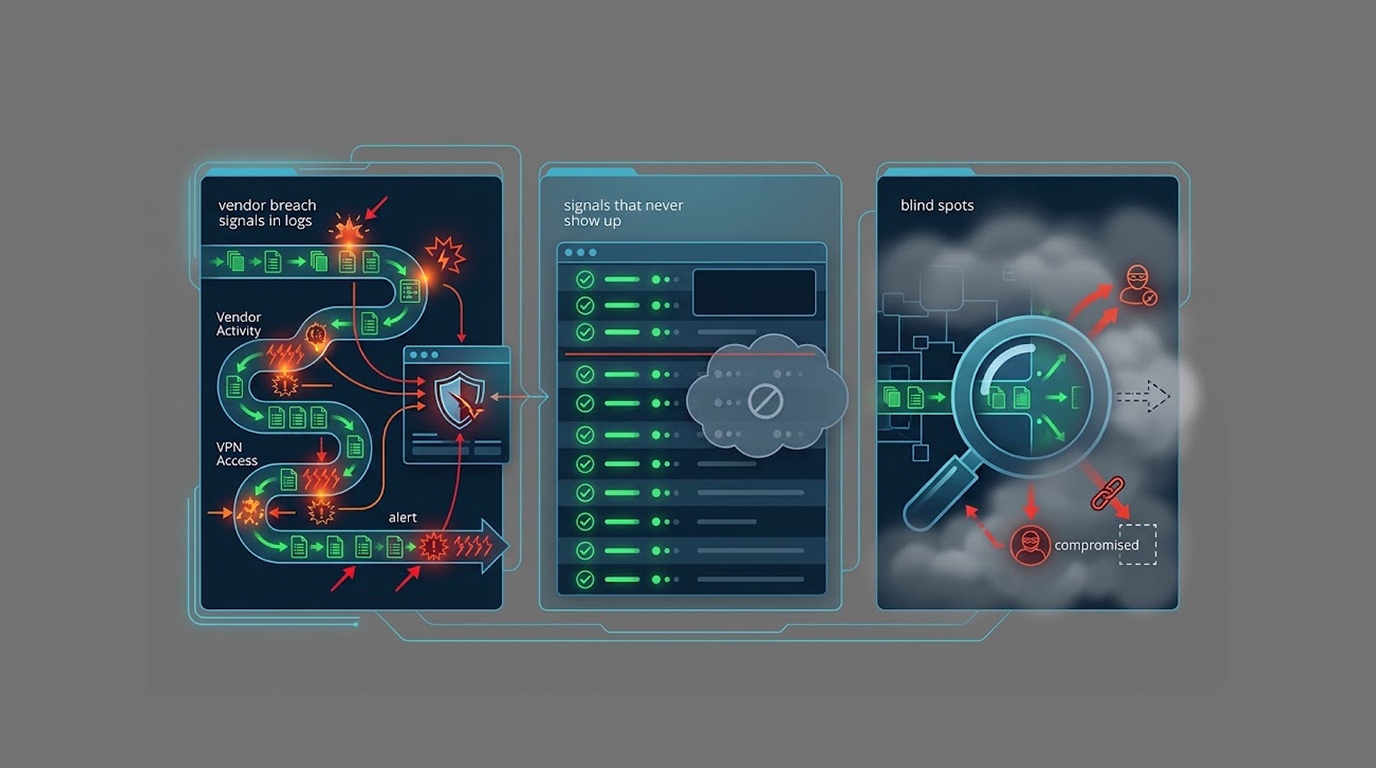
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
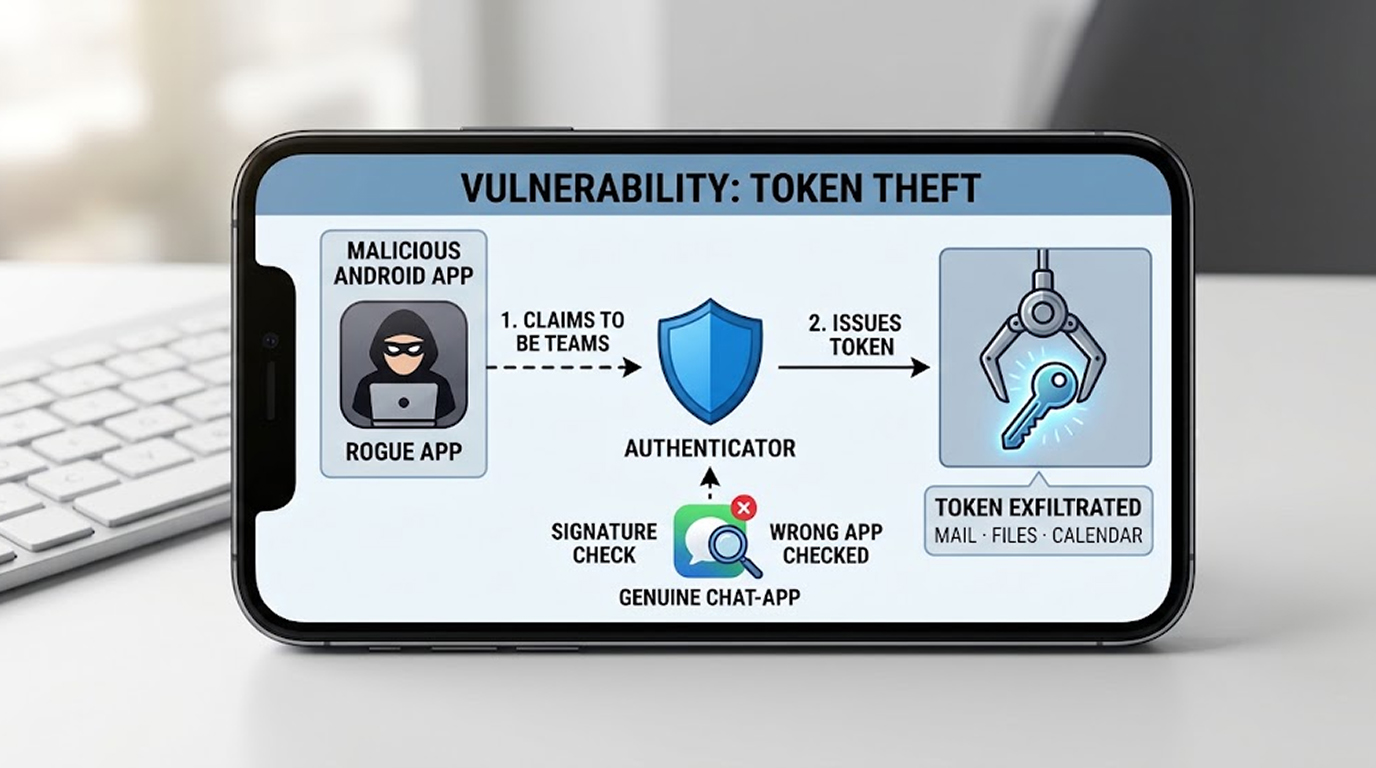
Microsoft just patched a nasty flaw in its Authenticator app for Android, because a malicious app with zero permissions could pose as a trusted Microsoft a...
Your Keystone hardware wallet might not be the genuine article, because an attacker who breached the company's website walked away with the cryptographic k...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067