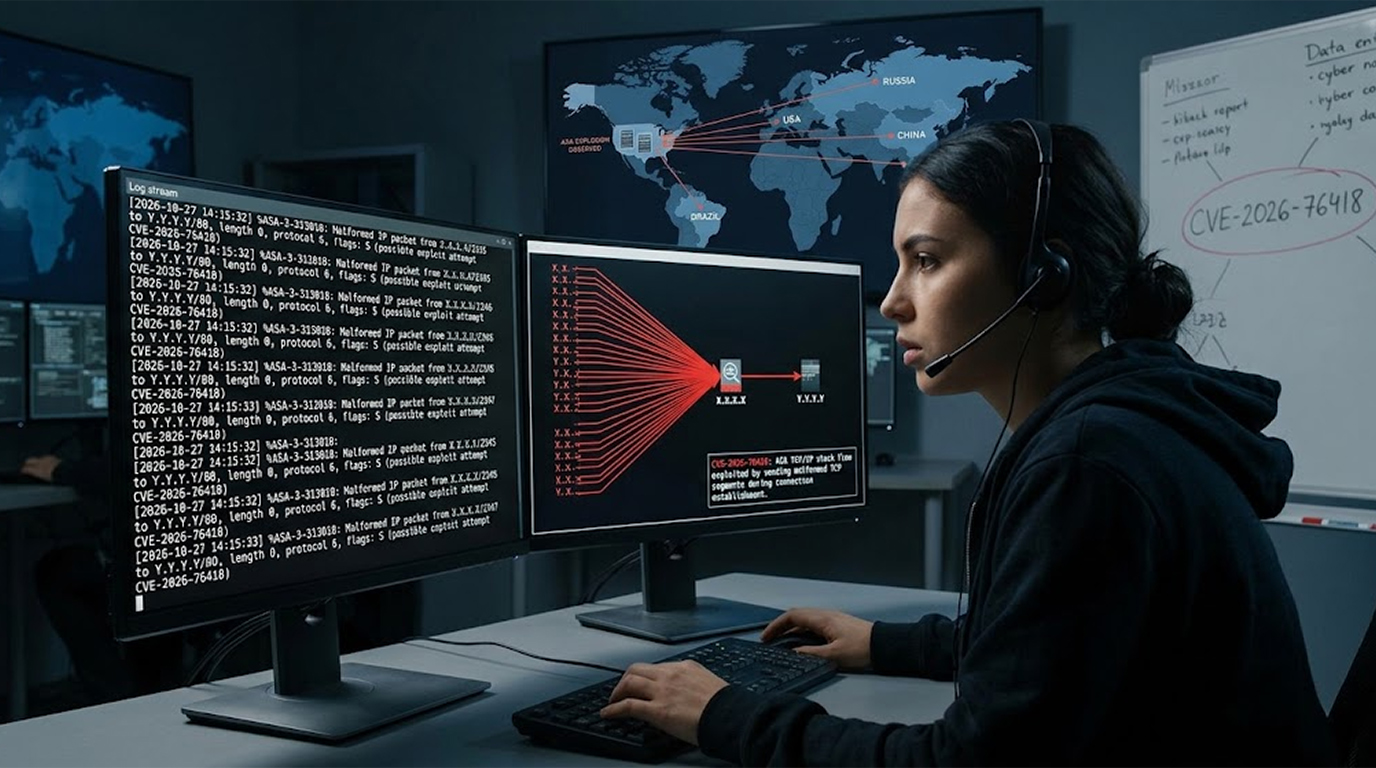
Cisco just confirmed that a high-severity flaw in its Secure Firewall ASA and FTD software is being exploited in the wild, and if you are running SSL remote access VPN with secondary authentication configured, an unauthenticated attacker can crash the device with a single crafted request.
The vulnerability is tracked as CVE-2026-76418, it carries a CVSS score of 8.6, and Cisco said it became aware of active exploitation in October 2026. It did not share when the attacks began, who is behind them, or how many devices have been hit.
What the Flaw Actually Does
Quick Security Checklist
- Scan your system or website
- Update all dependencies
- Change passwords
- Enable 2FA
The issue lives in the Remote Access SSL VPN service of ASA and FTD software. Cisco's advisory describes it as a logic error that occurs when secondary authentication is configured on a tunnel group.
An attacker sends a crafted request while connecting to the SSL remote access VPN. If the conditions line up, the device reloads unexpectedly, which results in a denial-of-service condition. That means your firewall, the thing standing between your network and the internet, just goes dark.
Here is the part that should get your attention: a successful VPN login is not required to reach the affected processing path. The attacker does not need credentials. They just need to hit the right endpoint.
The Three Conditions for Exposure
Cisco says your device is affected only if all three of these are true.
- It is running a vulnerable release of Cisco Secure Firewall ASA Software or Cisco Secure FTD Software.
- The SSL remote access VPN login service is reachable.
- Secondary authentication is configured in the tunnel group scope.
If tunnel-group-list enable is configured, you need to check all tunnel groups, including the default DefaultWEBVPNGroup, for secondary-authentication-server-group.
If tunnel-group-list enable is absent or has been removed with no tunnel-group-list enable, you still need to check DefaultWEBVPNGroup. Disabling the group list does not remove exposure if that default group uses secondary authentication.
The Patch Matrix
Fixes are available now. You need to match the version to your release train.
Cisco Secure Firewall ASA Software
|
Release Train |
Fixed Version |
|
9.16 and earlier |
9.16.4.104 |
|
9.18 |
9.18.4.96 |
|
9.20 |
9.20.4.50 |
|
9.22 |
9.22.3.200 |
|
9.23 |
9.23.1.48 |
|
9.24 |
9.24.1.27 and 9.24.10.1 |
Cisco Secure FTD Software
|
Release Train |
Fixed Version |
|
7.0 and earlier |
7.0.11 |
|
7.2 |
7.2.13 |
|
7.4 |
7.4.9 |
|
7.6 |
7.6.7 |
|
7.7 |
7.7.14 |
|
10.0 |
10.0.3 |
|
10.1 |
10.1.1 |
The Temporary Mitigation
If you cannot patch immediately, Cisco recommends two options. Turn off the tunnel group list if DefaultWEBVPNGroup does not use secondary authentication. Or disable secondary authentication on any user-configured tunnel group list, or on the default tunnel group itself.
On FTD, you need to review the deployed remote access VPN policy and the resulting running configuration in Cisco Secure FMC or Cisco Secure FDM. Do not assume the GUI reflects the running config.
The UAT-11473 Connection
This disclosure lands alongside a second Cisco advisory about an APT actor tracked as UAT-11473. That group weaponized CVE-2026-20127, an authentication bypass in Cisco SD-WAN Catalyst Controller, to gain unauthorized access to affected systems.
The activity has targeted space and satellite services, defense and aerospace technology, and policy research sectors. Cisco Talos assesses that UAT-11473 shares infrastructure overlaps with Volt Typhoon's Silent Train covert network.
UAT-11473 then installed a custom malware framework called KeyDrift, which includes components like PolyFlame and LittleFilch. The framework is built for collecting sensitive keying information, acting as backdoors and intermediate command-and-control hosts, and automating exfiltration.
KeyDrift operates inside SD-WAN control-plane processes. It is capable of intercepting decrypted control traffic, extracting control-session metadata and data-plane keying material, and staging or transmitting that material using encrypted records.
Put plainly: they are not just breaking in. They are stealing the keys that protect the traffic.
FAQ
What is CVE-2026-76418?
It is a high-severity (8.6 CVSS) denial-of-service flaw in Cisco Secure Firewall ASA and FTD software. A logic error in the SSL VPN secondary authentication path lets an unauthenticated attacker crash the device with a crafted request.
Do I need a valid VPN login to trigger it?
No. Cisco explicitly stated that a successful VPN login is not required to reach the affected processing path. That is what makes this so dangerous.
How do I know if my firewall is exposed?
Check three things. Is the SSL remote access VPN login service reachable? Is secondary authentication configured on a tunnel group? And are you running a vulnerable release? All three must be true.
Is disabling the tunnel group list enough?
Not always. If DefaultWEBVPNGroup uses secondary authentication, removing the tunnel group list does not remove exposure. You have to disable secondary auth on that default group too.
Has this been exploited in the wild?
Yes. Cisco said it became aware of active exploitation in October 2026, though it did not disclose when the attacks began or their scale.
What is KeyDrift?
It is a custom malware framework installed by the APT actor UAT-11473 after exploiting CVE-2026-20127 in Cisco SD-WAN. It intercepts decrypted control traffic and steals keying material for long-term persistent access.