Yes, you can audit your own website security, and for most small sites you should. A DIY website security audit covers the basics that stop the majority of real-world attacks: outdated software, weak passwords, missing backups, and leaked error messages. What you cannot do alone is deep vulnerability testing, which is where a professional review earns its money.
Here's a story you've heard before, even if you don't know it yet.
A small business owner wakes up to an email from a customer. "Hey, when I click your site, it redirects to a casino page." By lunchtime, Google has flagged the site as unsafe. By dinner, three more customers have emailed. By the end of the week, the site is blacklisted, the traffic is gone, and the fix is being quoted in the thousands.
The brutal part? The door was left open months earlier. An old plugin nobody updated. A password that was one word and a number.
Nobody targeted that business. It was simply the easiest house on the street to walk into.
Which brings us to the question you probably typed into Google: can you audit your own website security? The honest answer is yes, and you absolutely should. But "yes" comes with fine print, so let's get into it.
Why Most People Never Audit Their Website
Most owners skip security audits because they sound technical, expensive, and unlikely to matter until something breaks. In reality, the highest-impact checks are simple, free, and take under an hour to complete.
The word "audit" does a lot of damage. It sounds like tax season and men in suits.
But a website security audit is just a structured check of your site's weak points. Think of it as a health check, not open-heart surgery. You're looking for doors left unlocked, not rebuilding the house.
The reason you should care isn't fear. It's math. A compromised site costs you traffic, rankings, customer trust, and often hosting penalties. An hour of checking costs you nothing but an hour.
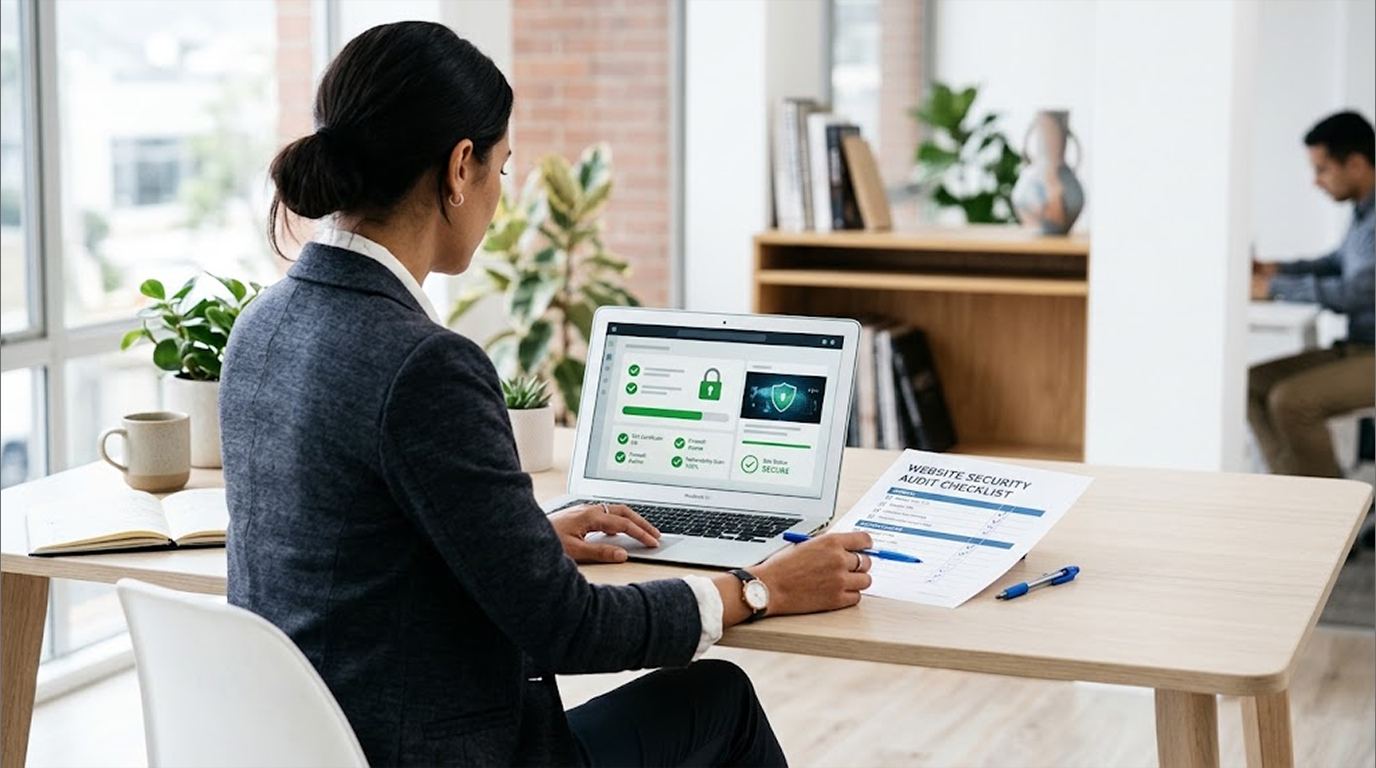
If you want the structure handed to you instead of building it from scratch, the Website Security Audit Checklist covers 150+ individual checks across 25 review areas, from SSL/TLS to WordPress hardening, so you're not guessing what to look at.
What Can You Actually Catch Yourself?
A DIY website security audit reliably catches outdated software, weak or reused passwords, missing two-factor authentication, no backups, stale admin accounts, exposed files, and unencrypted traffic. These are the same gaps behind most real-world website compromises.
Here's what a non-expert can find and fix in a single afternoon:
- Outdated software, your content management system, plugins, and themes.
- Weak or reused passwords, especially on admin and hosting accounts.
- Missing two-factor authentication, one extra step that blocks most credential theft.
- No tested backups, a backup you've never restored is a prayer, not a plan.
- Stale user accounts, old admins who should have been removed months ago.
- Exposed sensitive files, config files, logs, or directory listings visible to the public.
- Unencrypted traffic, a missing or misconfigured SSL certificate.
- Error messages leaking details, stack traces telling strangers exactly what software you run.
None of this requires a computer science degree. It requires a list, a bit of patience, and the willingness to actually do it instead of reading about it.
A good checklist turns this from a vague intention into a scored, repeatable process. The Red Secure Tech checklist, for example, includes a scorecard and a risk register, so every failed check becomes a tracked finding with a severity and a deadline instead of a note you forget by Friday.
What Will You Miss Without Professional Help?
A DIY website security audit cannot reliably test for authentication flaws, business logic vulnerabilities, injection attacks, API weaknesses, or supply chain risks. These require hands-on testing tools and the experience to interpret the results.
Let's be honest about the gap. A DIY website security audit is excellent at the boring 80 percent. It is genuinely poor at the clever 20 percent.
What you likely won't catch on your own:
- Authentication bypasses, routes that let someone in without logging in.
- Business logic flaws, like a discount code that can be applied eleven times.
- Injection vulnerabilities, places where user input gets treated as code.
- API weaknesses, endpoints that expose more data than intended.
- Third-party and supply chain risk, the script loaded from somewhere you forgot about.
This isn't a sales pitch for hiring a pentester every quarter. It's a map of where the checklist stops and real testing begins. The Website Security Audit Checklist is explicitly positioned as the tool you use before deciding whether you need a penetration test, not a replacement for one. For most small sites, closing the boring 80 percent removes the vast majority of realistic risk.
How Do You Audit Your Own Website Security, Step by Step?
Run your audit in a fixed order: update everything, check encryption, lock down accounts, verify backups, scan for malware, review exposed files, then check your forms and error handling. Doing it in the same order every time is what turns a one-off panic into a habit.
- Step 1: Update everything. Core software, plugins, themes, and your hosting control panel. Remove whatever you're not using. An abandoned plugin is an unlocked window nobody remembers opening.
- Step 2: Check your SSL setup. The padlock should appear on every page, not just the homepage. Browsers punish mixed content, and customers notice warnings more than you think. The checklist's SSL/TLS section alone covers HTTPS redirects, mixed content, certificate expiry monitoring, weak protocols, and HSTS configuration.
- Step 3: Lock down accounts. Strong unique passwords on admin, hosting, and email. Two-factor authentication everywhere it's offered. Delete accounts for people who no longer need access.
- Step 4: Verify your backups. Confirm they're running on a schedule, stored somewhere separate, and actually restore. A backup you've never tested is a rumour.
- Step 5: Run a malware scan. Most security plugins include one. It won't catch everything, but it catches the common stuff and gives you a baseline.
- Step 6: Hunt for exposed files. Try browsing to your config file and log directories. If you can see them, so can everyone else.
- Step 7: Review your forms and error pages. Make sure error messages stay vague in public. Detailed errors are useful to you and a gift to attackers.
That's the DIY loop. Repeat it regularly and you've closed more holes than most small businesses ever bother to check.
If you'd rather not build this loop from memory every time, the Website Security Audit Checklist walks you through every item in order, with 150+ checks across 25 areas, including WordPress-specific and Laravel-specific hardening sections. It starts at €29, it's an instant download with no subscription, and it's designed to be re-run every quarter.
How Often Should You Audit Your Website Security?
Run a full DIY audit quarterly, check for updates and failed logins monthly, and re-audit immediately after any major change: a new plugin, a new team member, or a migration.
Security isn't a task you complete. It's a rhythm.
Monthly: updates, login monitoring, backup confirmation. Quarterly: the full checklist, end to end. Immediately after changes: because most new holes get introduced when something gets added, not when time simply passes.
The checklist is built around that quarterly rhythm. Every edition includes a scorecard with rating bands from Strong to Critical, so you can track whether your posture is actually improving between audits or just feels like it is.
What Mistakes Do DIY Auditors Make Most Often?
The most common mistakes are auditing once and calling it done, skipping backup restore tests, ignoring staging and old subdomains, and treating a clean malware scan as proof of safety.
A few traps worth naming:
- One-and-done audits. The site changes weekly. The audit can't be annual.
- Backups assumed, never tested. Restore one. Today.
- Forgotten corners. Old staging sites, expired subdomains, and abandoned landing pages get breached just as easily as the main site.
- Clean scan equals safe. A scanner tells you it found nothing. That's not the same as there being nothing.
Final Thoughts
So, can you audit your own website security? Yes, genuinely, and you'd be foolish not to. The boring basics, done consistently, stop most of what actually happens to real websites.
But "doing it yourself" doesn't mean "remembering it all from scratch at midnight after a scare." It means following a system you trust, every time, in the same order.
That's the entire point of a checklist. It's the difference between intending to lock the doors and knowing you did.
You can get the full Website Security Audit Checklist here and turn a vague worry into a repeatable habit. It covers 150+ checks across 25 review areas, includes a risk register and a 30-day prioritised action plan, and starts at €29.
FAQ
Can you audit your own website security without technical skills?
Yes, for the core checks. Updates, passwords, two-factor authentication, backups, and exposed files can all be handled by a careful non-expert. Deep vulnerability testing is where you need help.
How often should you audit your website security?
Quarterly for the full checklist, monthly for updates and login monitoring, and immediately after any significant change to the site or your team.
Is a DIY website security audit enough for a small business?
It covers the majority of realistic risk for most small sites. If you handle payments, personal data, or customer accounts, pair the DIY audit with periodic professional testing.
What should you check first in a website security audit?
Updates and account security. Outdated software and weak credentials are the most common entry points, and both are fixed in minutes.
Do free website security scanners actually work?
They work as a baseline, not a guarantee. Use them to catch known malware and obvious misconfigurations, then verify the rest by hand. For the checks scanners miss, the Website Security Audit Checklist gives you the full manual review structure.