Weaver E-cology Unauthenticated RCE Exploit Under Active Attack
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
Found 562 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
Imagine waking up to find your email server locked. Your admin password does not work. Your users cannot send or receive messages.You did not click a phish...
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
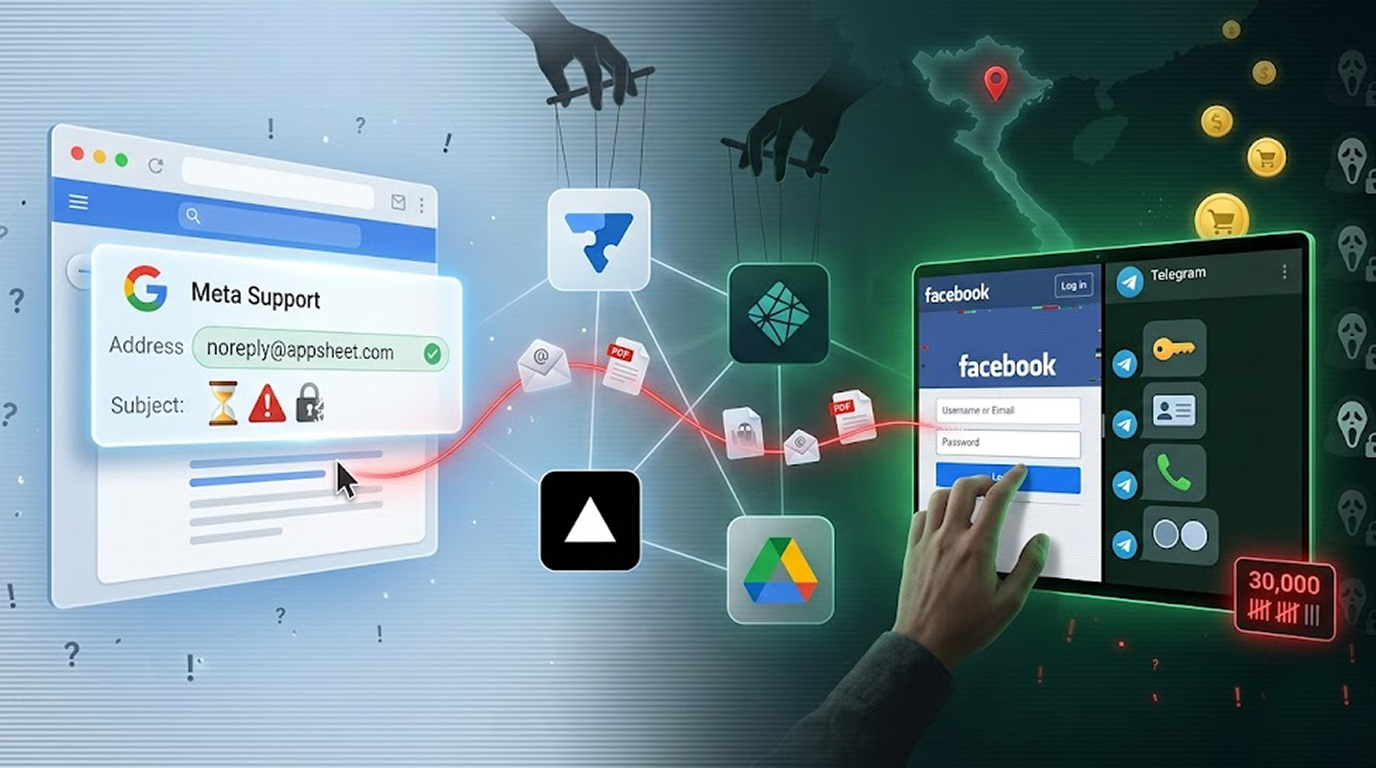
You receive a fake email from Meta Support that looks legitimate, as it was sent from a Gmail address using the @appsheet.com domain (which is operated by...
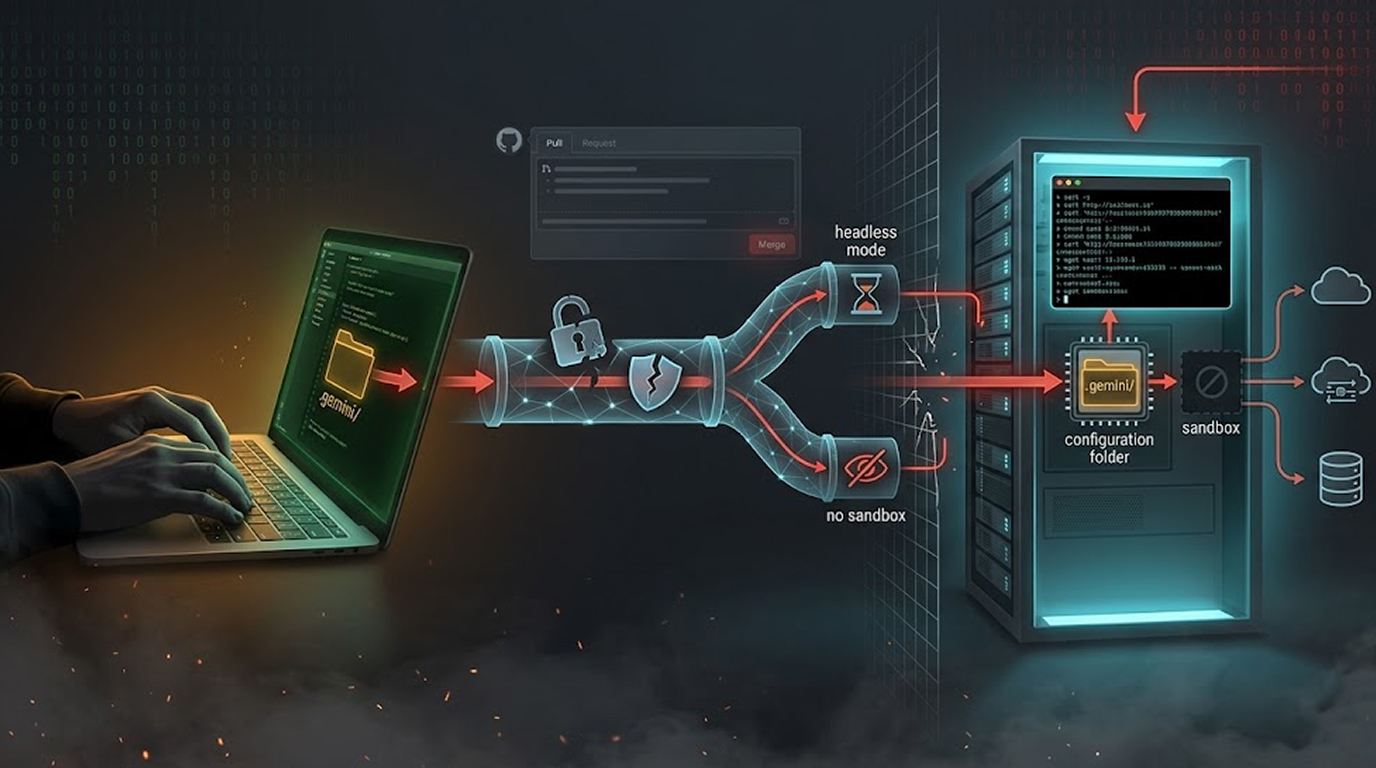
A perfect 10. That is the CVSS score Google assigned to a security flaw in its Gemini CLI tool. And for good reason. The Gemini CLI remote code execution...
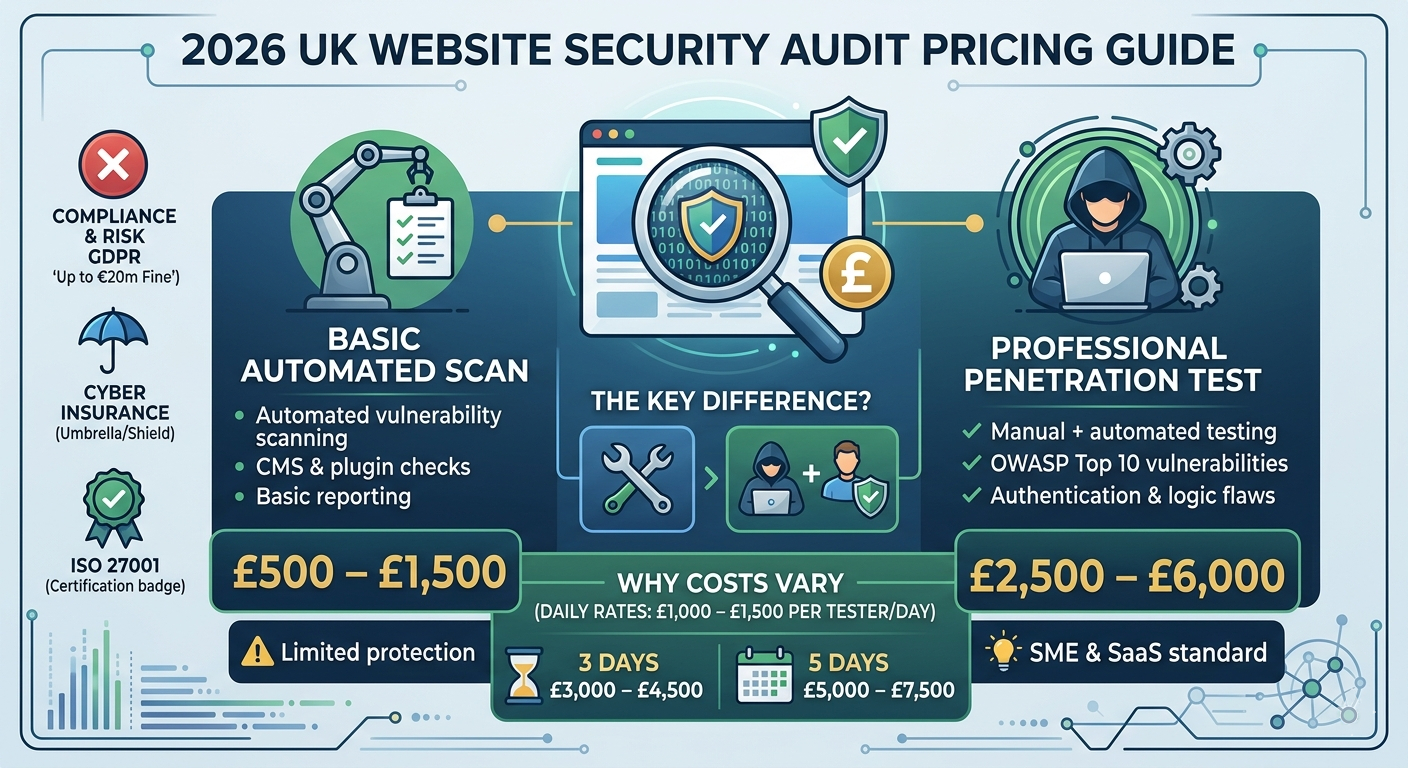
If you're researching website security audit cost in the UK, you’ve probably noticed something confusing: Some providers charge £500… o...
Microsoft fixed a security flaw in February. Attackers found a way around it. Now the company has admitted the incomplete patch left a different vulnerabil...
You imagine a hacker. Dark room. Glowing screens. Fingers flying across a keyboard. Exploits. Zero-days. Firewalls crumbling.That is Hollywood. The realit...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067