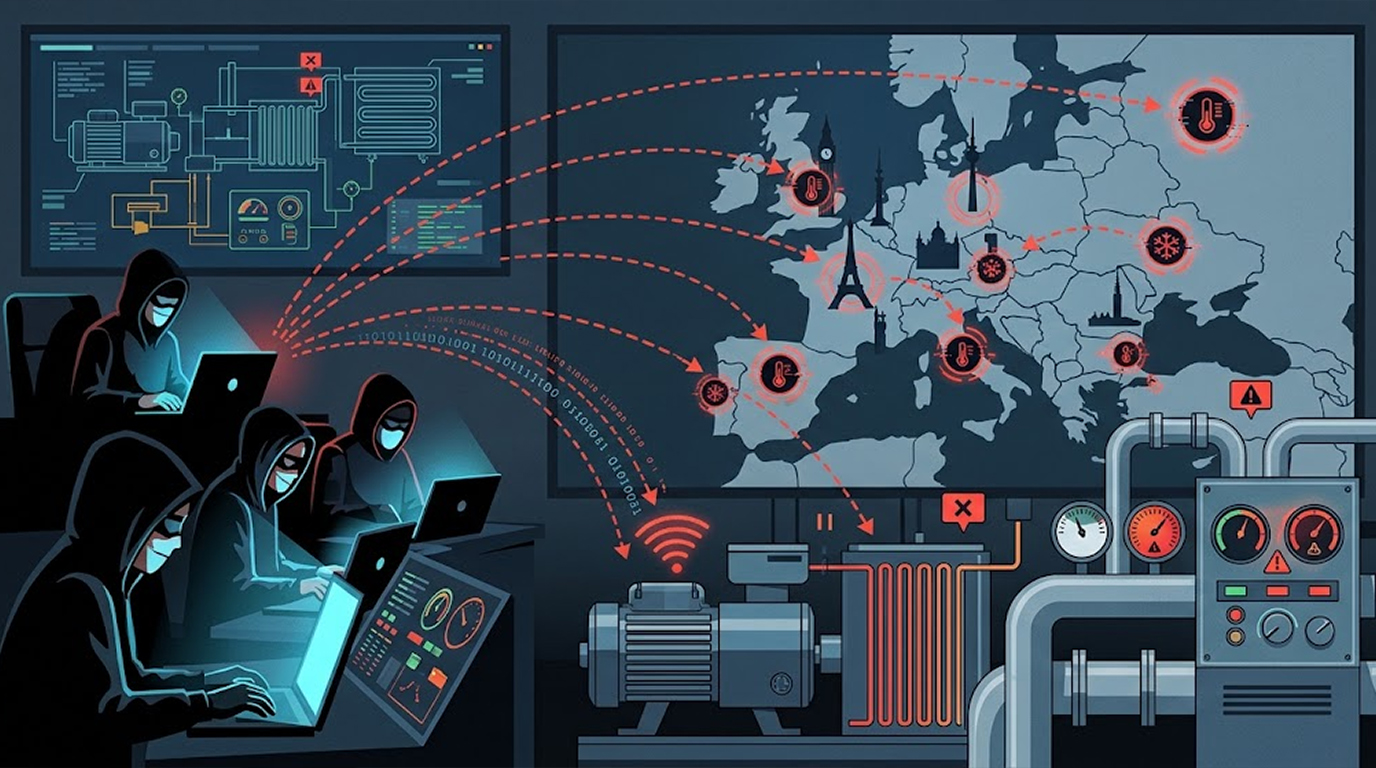
Someone spent Sunday night changing the temperature settings on supermarket refrigeration systems in Belgium, Sweden, Estonia, the Netherlands, and a handful of other European countries. They did not steal data. They did not deploy ransomware. They just made the freezers warm.
No chain reported more than several dozen affected stores. Some threw out chilled and frozen food. Others pulled it from shelves as a precaution. And the equipment involved, in several confirmed cases, was made by Danfoss, the same Danish manufacturer whose controllers were targeted three weeks earlier in an attack on hundreds of French supermarkets.
Nobody had claimed responsibility by Monday night. It is not yet clear whether the two campaigns are connected.
What Actually Happened
Refrigeration controllers are small computers that run a store's fridges and freezers. They are often internet-connected so refrigeration contractors can monitor them and fix faults remotely. That convenience is the entire attack surface.
In Belgium, attackers switched cooling units into defrost mode. Stephan Moelans, chief executive of the refrigeration contractor Sabcobel, described the effect to Belgian media. Defrost mode exists to clear ice buildup, but in this case it made the units heat up instead of holding food cold.
In other cases, the temperature setpoint was simply raised.
|
Country |
Company |
Stores Affected |
What Was Reported |
|
Belgium, Luxembourg |
Delhaize |
Several dozen |
"IT incident" affecting refrigeration |
|
Belgium |
Carrefour |
15 of 700+ |
Cyberattack, very limited impact |
|
Belgium |
Intermarché |
10 to 15 |
Fridge problems |
|
Belgium |
Spar (Colruyt Group) |
5 |
Fridge systems attacked |
|
Belgium |
IKEA Mons |
1 |
Cyber incident on fridges and freezers |
|
Sweden |
ICA |
Limited number |
Incident affecting refrigeration |
|
Sweden |
Coop |
6 to 7 of 800 |
Unauthorized tampering with refrigeration |
|
Ireland |
Musgrave (SuperValu) |
13 of 223 |
Cyber incident limited to one model |
|
Estonia |
Selver |
1 |
Attack on older Danfoss system |
|
Netherlands |
Unnamed businesses |
At least 17 |
Attack confirmed by Danfoss |
|
Finland |
Kesko |
A few smaller stores |
Unusual temperatures, cause under investigation |
|
Portugal |
Intermarché (Mosqueteiros) |
7 |
Cyberattack on external refrigeration manager |
|
Italy |
Coop (Radenza Group) |
At least 4 in Sicily |
Attack on remote control system |
The Damage in Concrete Terms
An ICA store in Sjöbo, southern Sweden, said its fridges and freezers had been set to 50°C. Staff were throwing out affected goods.
A Selver supermarket in Estonia had a freezer set to 50°C, according to Jann Mutso, chief executive of the refrigeration supplier Kitman Coldtech. In that case the temperature rose only about 2 to 3 degrees, the problem was resolved in roughly 10 minutes, and no products were damaged.
At a De Laet & Van Haver butcher shop in Hove, south of Antwerp, fridges were turned up to 18°C. Owner Luc De Laet told Reuters he estimated about €15,000 worth of meat was ruined.
Musgrave pulled chilled and frozen products from sale at 13 SuperValu stores as a precaution. By Monday afternoon the company said the incident was resolved and restocking was underway.
How Attackers Got In
This is the part that matters most, and it is not a sophisticated exploit.
The Dutch systems that were hit were not on a secure network and still used default passwords. A Danfoss spokesperson told NOS that most shops in the Netherlands had taken measures after the French attack, but a few had not, and those were the ones hit.
Danfoss told Belgian broadcaster VTM that the weakness lies mainly in outdated software, and that customers who had not updated were affected.
Sabcobel knows of roughly 20 affected units among the hundreds it manages in Belgium. Moelans said attackers got into individual supermarkets' systems, not the contractors' systems. Sabcobel had advised stores to secure their internet connections. Many did. Not all.
Mutso said old controllers that had not been updated were being targeted. Selver confirmed the affected store was the last one it had not yet migrated to a new system.
ICA told NBC News that its own systems were not affected, and that the affected stores used an outside supplier connected to a network outside ICA's central network.
The Equipment in Question
Danfoss is not named in every case, but it appears in several.
All of ICA's affected stores were connected to an outside refrigeration control system supplied by Danfoss, an ICA spokesperson told AFP. In Estonia, attackers reached the control computer of an older Danfoss system.
An affected Belgian butcher told Dutch broadcaster NOS that Copeland equipment was also attacked in Belgium. Copeland gave NOS no clear answer when asked.
CERT-FR's October alert covers Danfoss AK-SM and AK-SC series controllers, as well as Copeland xweb and Dixell xweb. It states that attack campaigns against these devices are probably still underway.
In October, Danfoss said most of the units hit in France were older models it no longer updates, specifically the AK-SM 800 and AK-SC 355.
What Operators Should Do
CERT-FR's alert remains the most detailed public guidance available. When The Hacker News checked on November 3, it had last been updated on October 16.
For devices that have not been compromised:
- Remove internet reachability. Make sure the controllers cannot be reached from the internet, including any device on a public IP. Check your insurance contract before cutting the data feed to your refrigeration contractor.
- Audit the full configuration, especially defrost schedules.
- Restore access only through a secure VPN or a protected network. Firewall filtering of contractor IPs is acceptable in an emergency, but not as a permanent fix.
- Follow the manufacturer's guidance. Update firmware. On Danfoss devices, set the security level to Strict and confirm default passwords have been changed.
For devices that have been compromised, two more steps are required. Restart the Danfoss device or reset it to factory settings, then reconfigure it before returning it to service.
CERT-FR is explicit about end-of-life hardware. Devices that no longer receive security fixes are very likely to be compromised if they remain internet-facing. A factory reset alone leaves them open to the same attack again.
The Industry's Own Assessment
Sweden's National Cybersecurity Centre advised organizations to inventory which devices are internet-connected, decide whether each one needs to be, and keep the remaining ones updated and protected with layered security.
Moelans made a point that software updates alone will not solve. The installations need physical changes, and those cost money. The simplest answer is a secure internet connection for managing the fridges, which most of Sabcobel's customers adopted after the French attack.
Who Is Behind It
Danfoss said the Dutch attacks matched the pattern from France. Sabcobel said the method in Belgium was the same. Kitman said Estonia was similar.
A shared method does not establish that the same people carried out both campaigns.
Belgium's Centre for Cybersecurity said on Monday that it did not know who was responsible, and that it may never be determined. Belgium's federal prosecutor's office has opened a criminal investigation. Sweden's National Cybersecurity Centre said it was following the incidents and sharing information with agencies across the Nordic region and Europe.
FAQ
What happened to the supermarket refrigeration systems?
Attackers accessed internet-connected refrigeration controllers and changed settings overnight into Monday, November 2, 2026. Some units were switched into defrost mode, which made them heat up. Others had their temperature setpoints raised as high as 50°C.
Was Danfoss equipment involved?
Yes, in several confirmed cases. Danfoss AK-SM and AK-SC series controllers appear in CERT-FR's advisory, and an ICA spokesperson confirmed all affected ICA stores used a Danfoss-supplied external control system.
How did attackers get in?
According to Danfoss and the contractors involved, the affected systems used default passwords, outdated firmware, or were exposed directly to the internet without a secure network in front of them.
Is this connected to the French supermarket attacks?
The method appears to be the same, and Danfoss said the Dutch attacks matched the French pattern. But no authority has confirmed a link, and Belgium's Centre for Cybersecurity said it may never be determined who was responsible.
What should a supermarket operator do right now?
Remove internet reachability from refrigeration controllers, restore access only through a VPN or protected network, audit defrost schedules and temperature setpoints, update firmware, change default passwords, and set Danfoss devices to Strict security level.
What about older controllers that no longer receive updates?
CERT-FR warns that end-of-life devices on the internet are very likely to be compromised, and a factory reset alone will not protect them. Replacement is the practical answer.