If you are holding onto an older iPhone or iPad, you need to update it right now. Apple just quietly pushed out a critical security patch because a zero-day flaw is actively being exploited in the real world, and it is being used to target specific individuals.
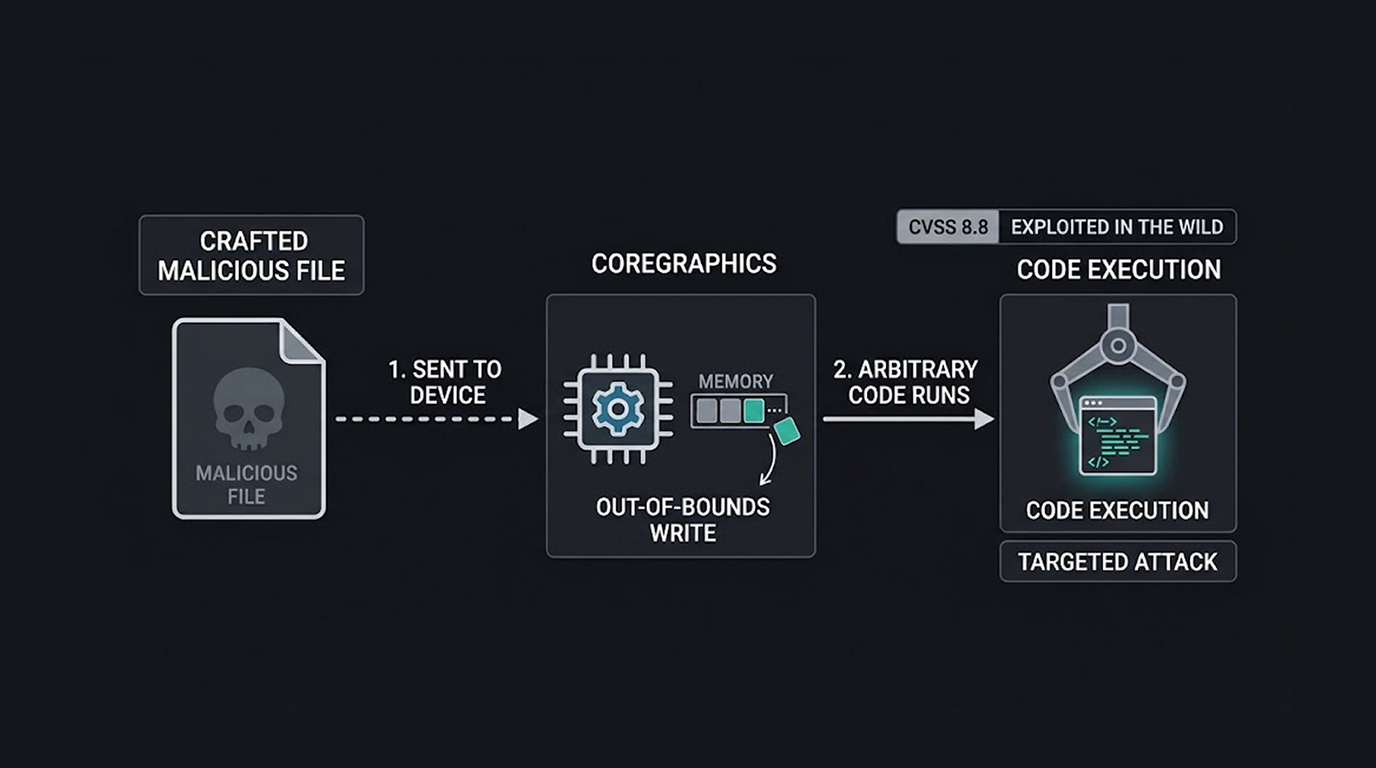
The bug is tracked as CVE-2026-86950, it carries a CVSS score of 8.8, and it is an out-of-bounds write issue in CoreGraphics. Basically, if an attacker sends you a maliciously crafted file, the flaw lets them execute arbitrary code on your device.
The Sophisticated Attack Vector
Apple initially fixed this flaw last month for users on the latest operating systems, but they have now backported the patch to older devices. Apple explicitly stated that they are aware of reports that this issue may have been exploited in an "extremely sophisticated attack against specific targeted individuals."
That means this is not some random hacker spraying ransomware at everyone. It is advanced, targeted espionage or high-level cybercrime aimed at specific people.
The backported fixes are available in iOS 18.7.11 and iPadOS 18.7.11, and they cover a very specific set of older hardware.
|
Device Type |
Supported Models |
|
iPhone |
iPhone XS, iPhone XS Max, iPhone XR |
|
iPad |
iPad 7th generation, iPad Air 4th generation and later, iPad 9th generation and later, iPad mini 6th generation and later |
The Hidden Risks in the Same Update
The iOS 18.7.11 update does not just fix the CoreGraphics zero-day, because it also patches two other nasty security holes that could compromise your privacy.
- Audio Data Leak (CVE-2026-65339): A logic issue in the Audio component could let a malicious app leak your sensitive information.
- Camera Bypass (CVE-2026-86990): An access vulnerability in CoreMedia could be abused by a malicious app to access your camera without your permission.
That camera bypass is especially creepy, because it means a rogue app could theoretically watch you without ever triggering the green indicator dot.
The Massive iOS 27.2 Release
Alongside the older device patches, Apple also dropped iOS 27.2, iPadOS 27.2, macOS Golden Gate 27.2, tvOS 27.2, watchOS 27.2, visionOS 27.2, and Safari 27.2, fixing hundreds of vulnerabilities across the board.
One notable fix is an authorization issue in Apple Intelligence (CVE-2026-86987) that could let a remote attacker access sensitive user data. Apple fixed it with improved entitlement checks. The update also patches a massive list of flaws in AppleAVD, CoreAudio, ImageIO, the kernel, Model I/O, Screen Sharing Server, Spotlight, StorageKit, and WebKit.
How to Update Your Device
Apple has not mentioned that these other flaws were exploited in the wild, but the CoreGraphics zero-day is a confirmed active threat, so you need to move fast.
- Open Settings: Go to the Settings app on your iPhone or iPad.
- Navigate to General: Tap on General, then Software Update.
- Install the Update: If you are on an older device, you will see iOS 18.7.11 or iPadOS 18.7.11. If you are on the latest hardware, you will see iOS 27.2.
- Enable Automatic Updates: To avoid missing future patches, go to Settings > General > Software Update > Automatic Updates and make sure downloading and installing are toggled on.
FAQ
What actually is CVE-2026-86950?
It is a memory corruption bug buried in CoreGraphics. In plain English, if you open the wrong file, an attacker can run their own code on your phone. No jailbreak required.
Was this flaw exploited in the wild?
Yeah. Apple confirmed it was used in "extremely sophisticated attacks" against specific targets. It wasn't a random mass-hack; it was highly targeted.
Am I affected if I have an older iPhone?
Depends on how old. If you are rocking an iPhone XS, XS Max, XR, or one of the specific older iPads listed earlier, you need to grab iOS 18.7.11 right now. If your phone is older than that (like the iPhone X), you are out of luck, it is not getting updates anymore, and that is a massive risk.
What is the deal with the Apple Intelligence flaw?
It is a separate issue (CVE-2026-86987). Basically, a remote attacker could access your sensitive data through it. Apple patched it in iOS 27.2 by tightening up the entitlement checks. Just update your phone.
Can a rogue app really spy on my camera?
It was a real bug (CVE-2026-86990). It let apps bypass the permission checks and access the camera without asking. The patch closes the hole, but only if you actually install the update. Do not put it off.