Postinstall.js Malicious Code Obfuscation: 4 Layers Attackers Use
You run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
You run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically. You did not approve it. You did not review...
Read Full ArticleYou run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically...
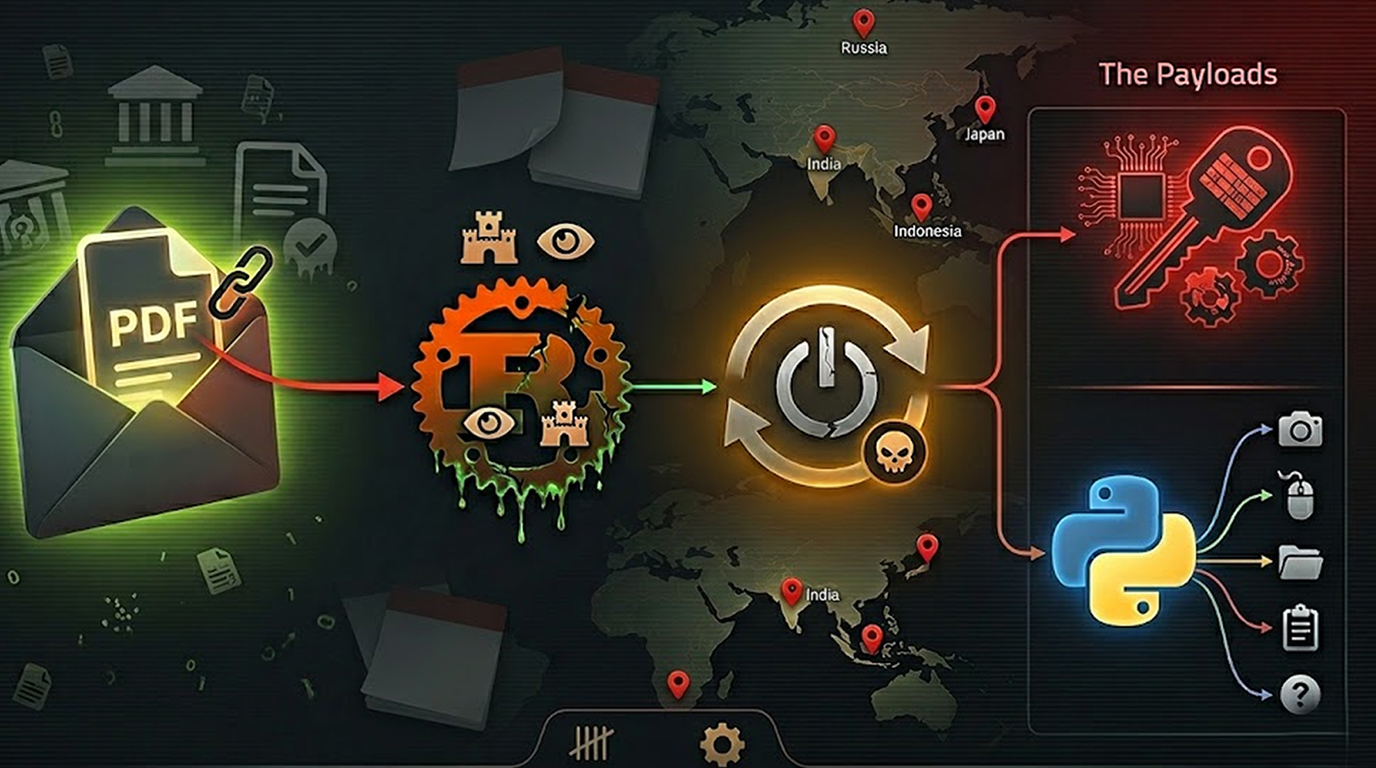
A Chinese cybercrime group is pretending to be tax authorities in two different countries. Their goal? Deliver malware that steals data, controls systems,...
Imagine waking up to find your email server locked. Your admin password does not work. Your users cannot send or receive messages.You did not click a phish...
Telegram is now a fight for the future. On one side: platform moderators and automated bots are working extra hard to get rid of illegal content (online sc...
There have been large changes to the Internet in the last few decades. Twenty years ago the focus of digital policy was on spam filtering and domain names....
60 seconds to summarize for you about DIRTPIPE (Dirty Pipe) security vulnerability. The TL;DR (10 Seconds) Question Answer What...
A potential compromise in the security of Chrome's CSS Engine, contains a vulnerability (CVE-2026-2441) which was found before even anyone had ever realize...
You receive a fake email from Meta Support that looks legitimate, as it was sent from a Gmail address using the @appsheet.com domain (which is operated by...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067