Types of Videoconferencing Malware and How Each One Works
"Videoconferencing malware" gets used as if it describes a single thing, and it doesn't, because the software in question is abused in at least a dozen dis...
Found 199 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
"Videoconferencing malware" gets used as if it describes a single thing, and it doesn't, because the software in question is abused in at least a dozen dis...
The mental image most people carry of state-sponsored espionage is a team of elite operators, custom zero-days, and infrastructure that costs more than a s...
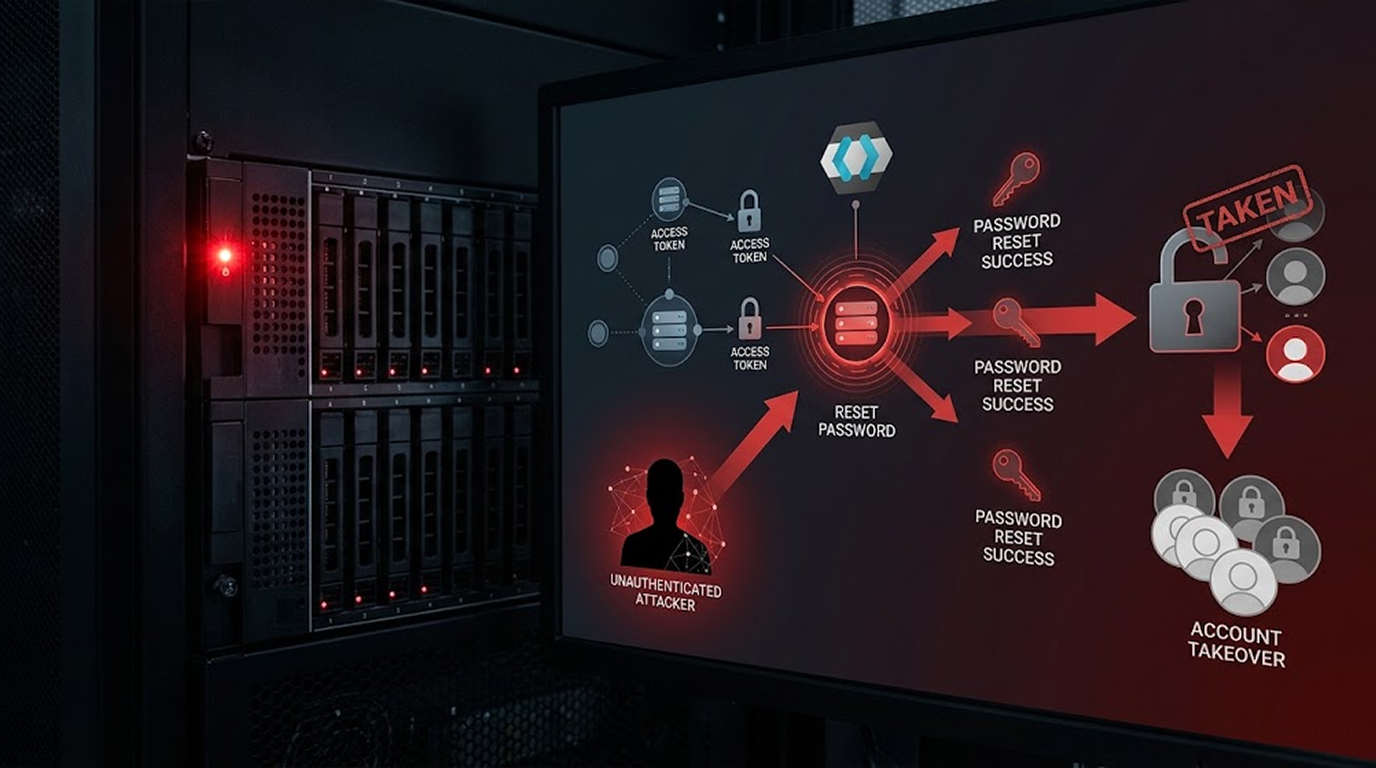
Password reset flows are supposed to be the safest part of an authentication system. You enter an email, you get a link, you click it, you change your pass...
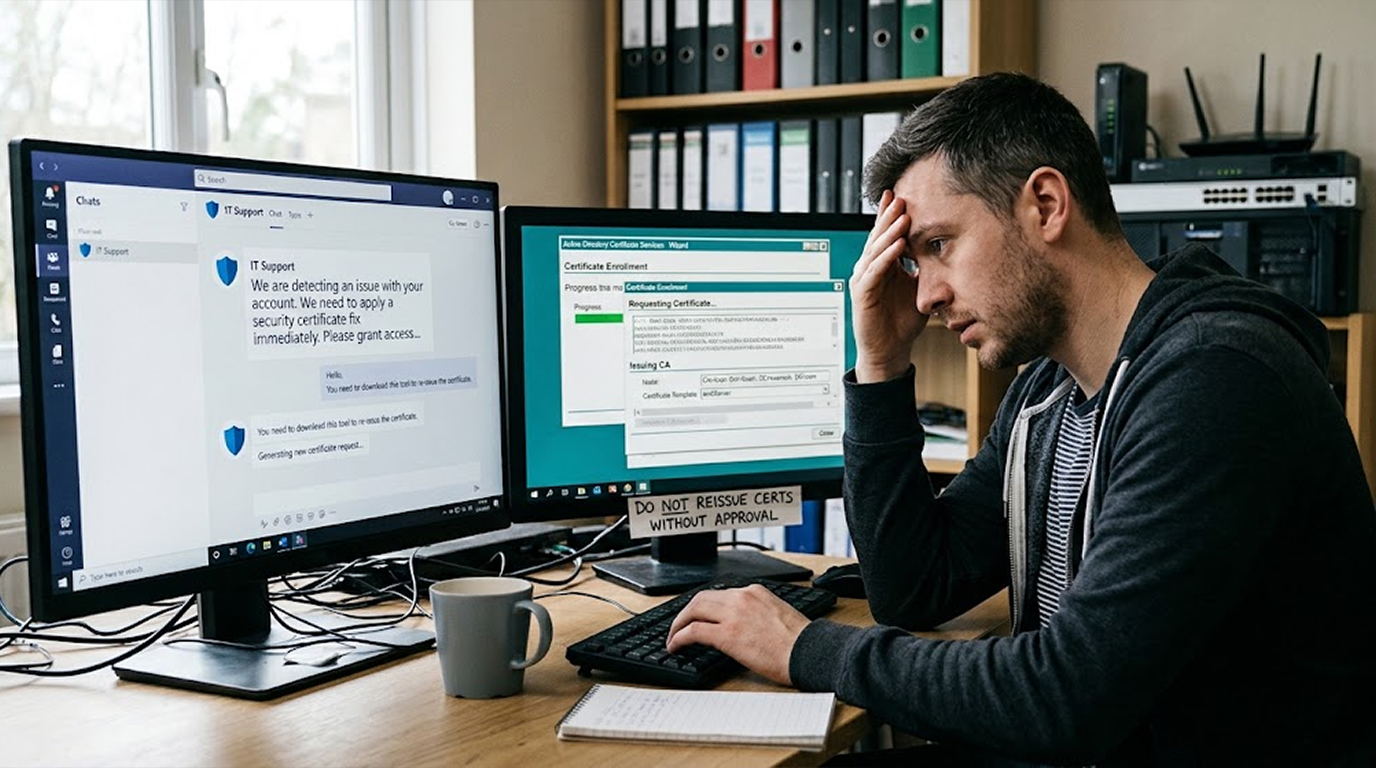
No zero-day. No malware-laced attachment. No exploit chain worth a conference talk. Microsoft just published an investigation into two intrusions where th...
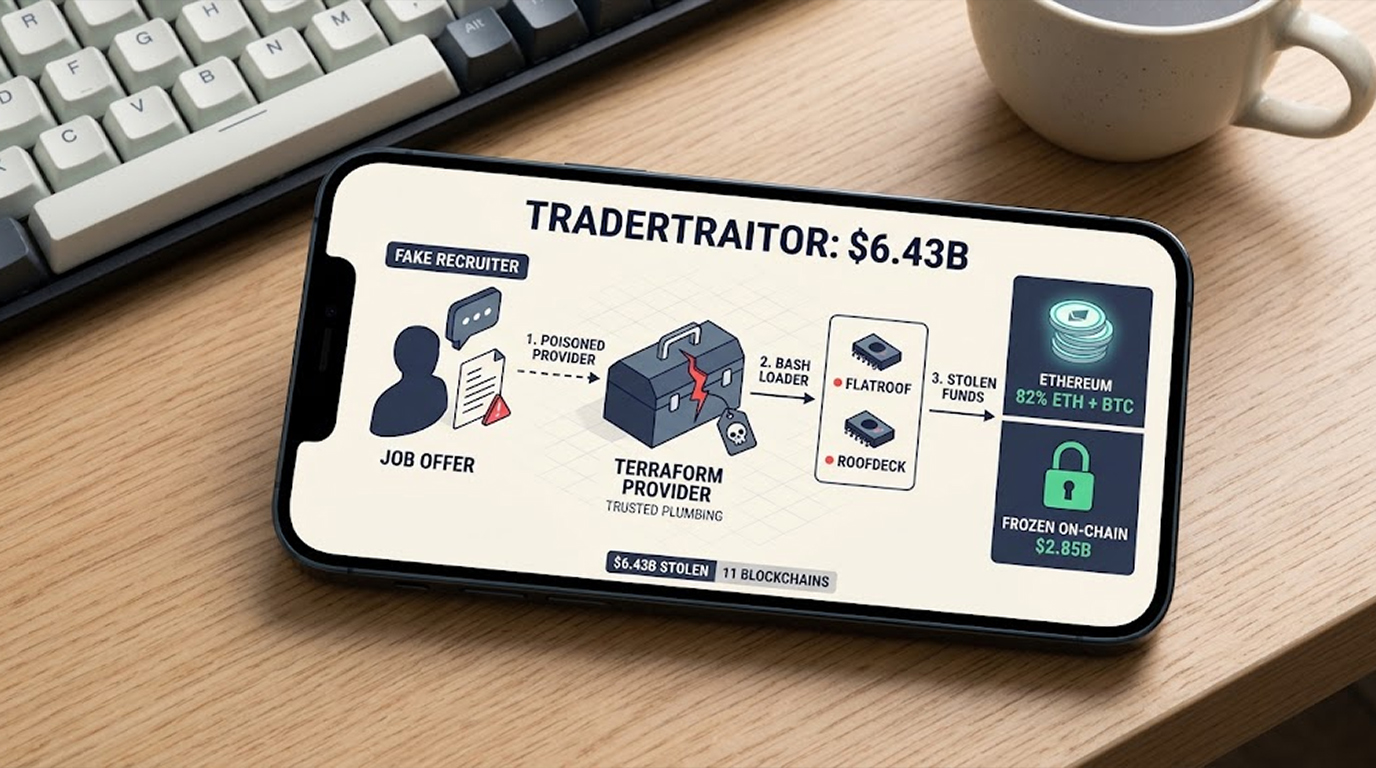
Six billion dollars. That is the number the FBI put on a single hacking operation this week, and it belongs to TraderTraitor, a North Korean crew that also...
You're sitting in a coffee shop, or on a train, or in a lecture hall, and your phone buzzes with a popup saying someone nearby wants to share a file with y...
Your repository might look clean and still be compromised, because the actor behind GhostAction has moved past injecting workflows entirely, and the new Gh...
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067