npm Supply Chain Attack Campaign Hits 800 Packages
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
Found 214 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targ...
North Korean threat actors are back at it. This time, however, they are using an advanced macOS malvertising attack where they trick their victims into cli...
A 90-second hack. A $300 toolkit. A virtual camera feed. And a bank's facial recognition system is defeated. This is not a movie plot. This is happening r...
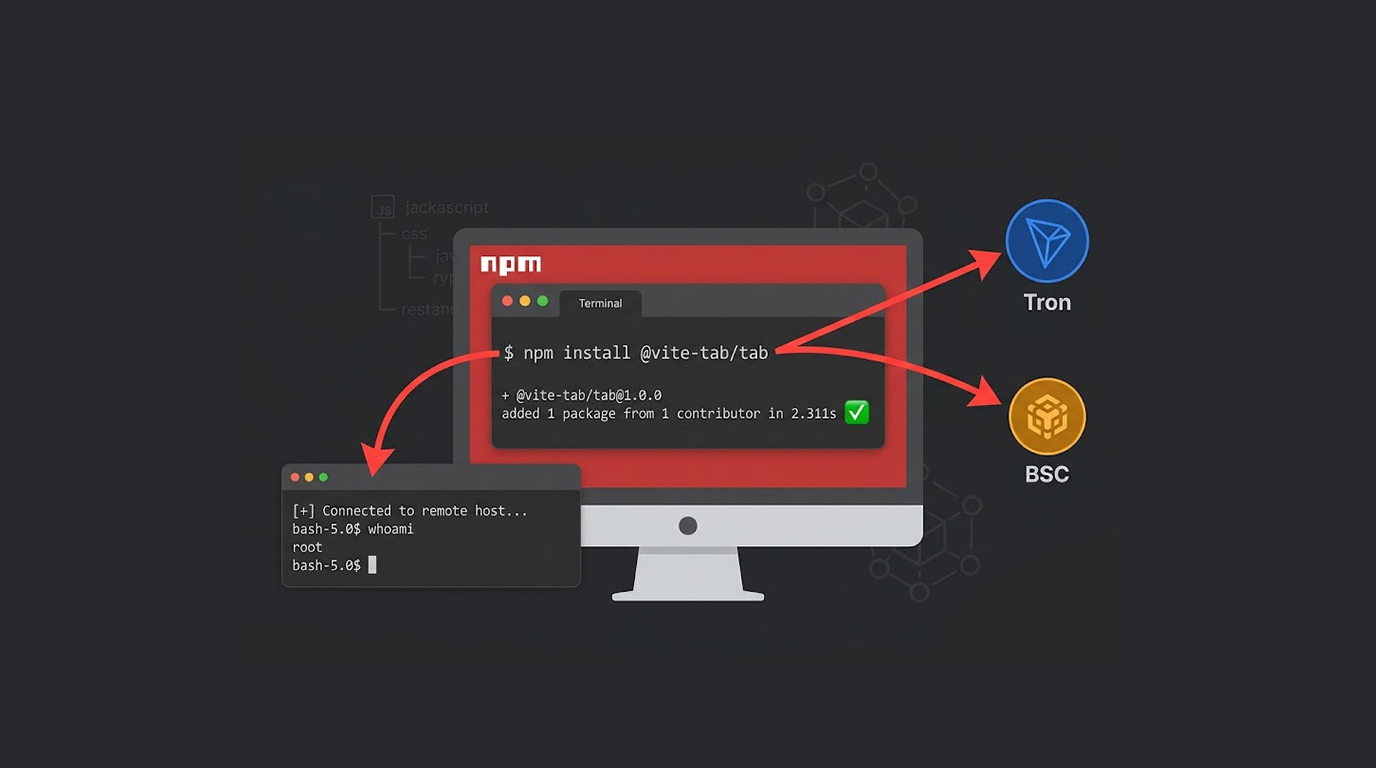
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
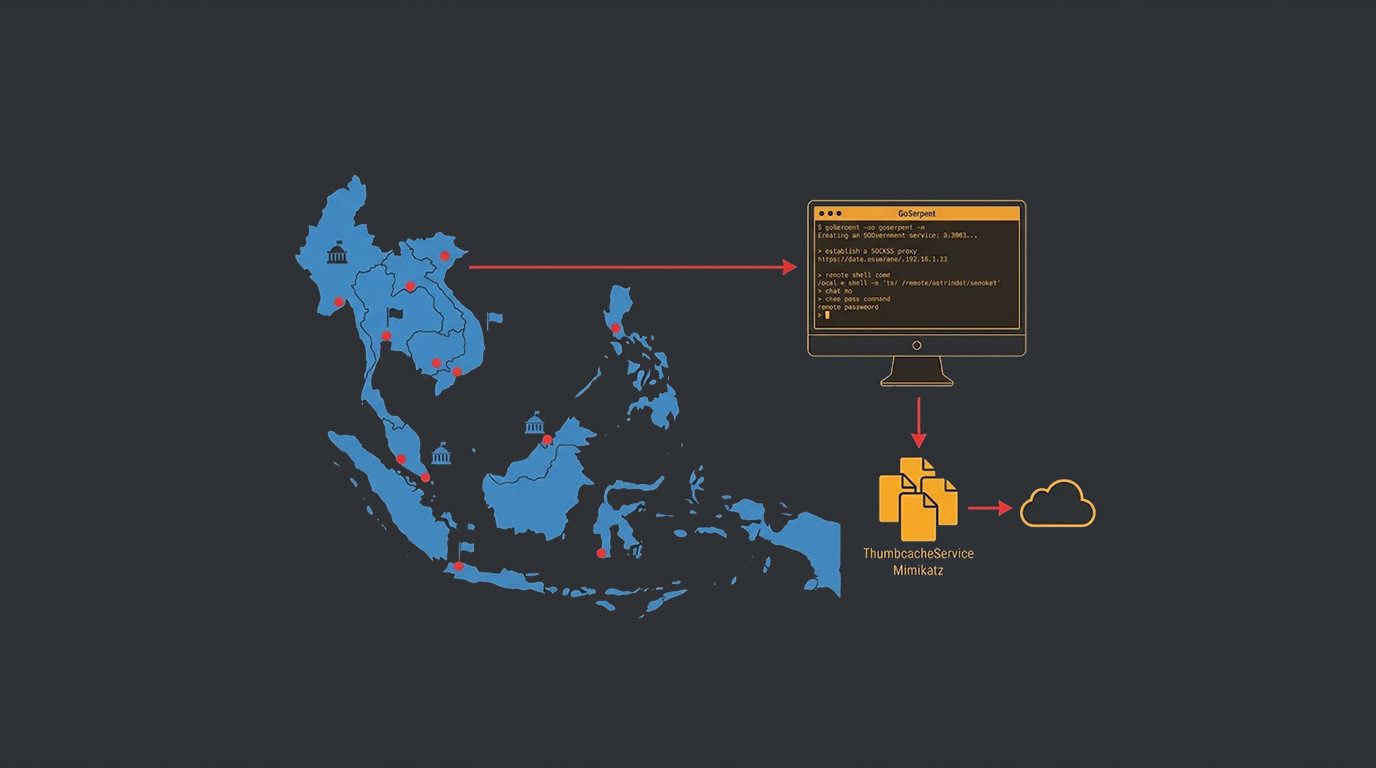
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
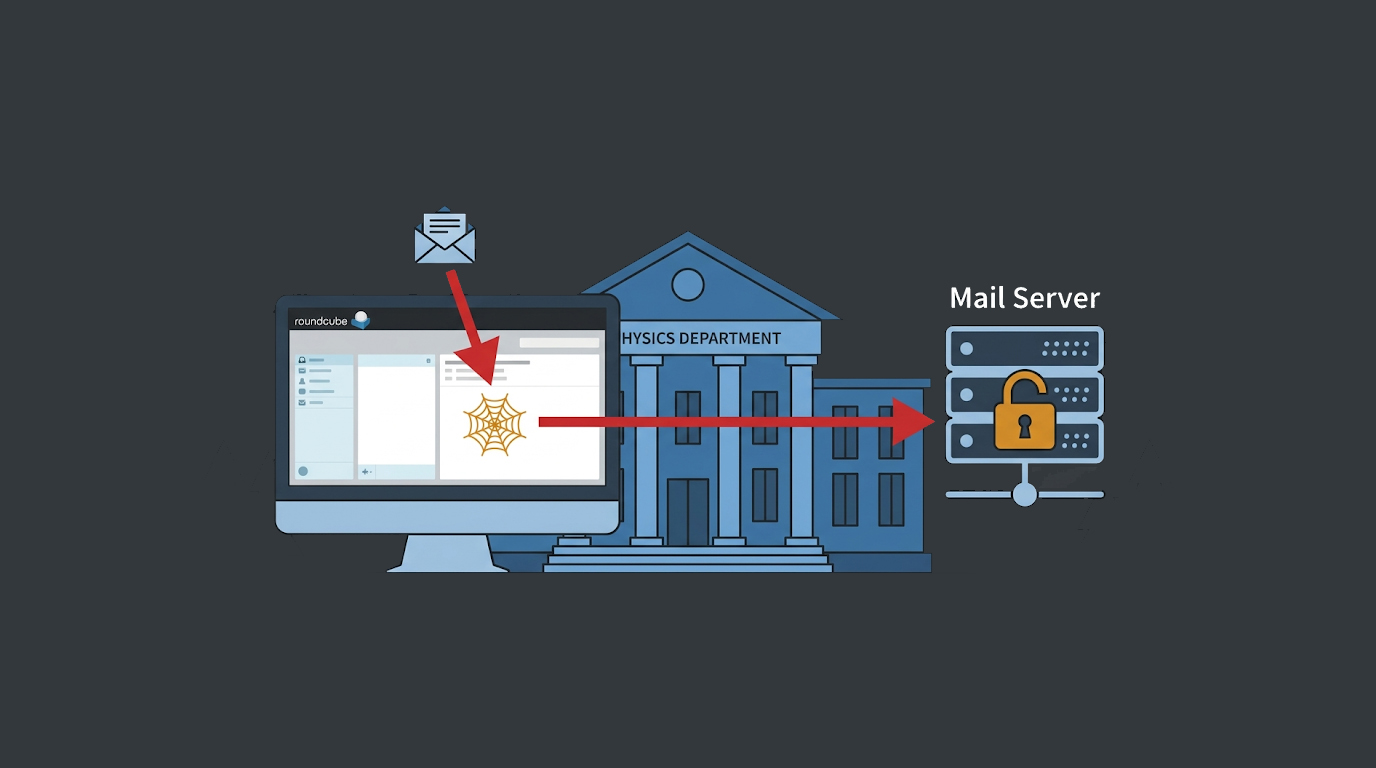
China-linked activity cluster suspected of carrying out attacks on the Roundcube webmail program of universities in the United States and Canada through th...
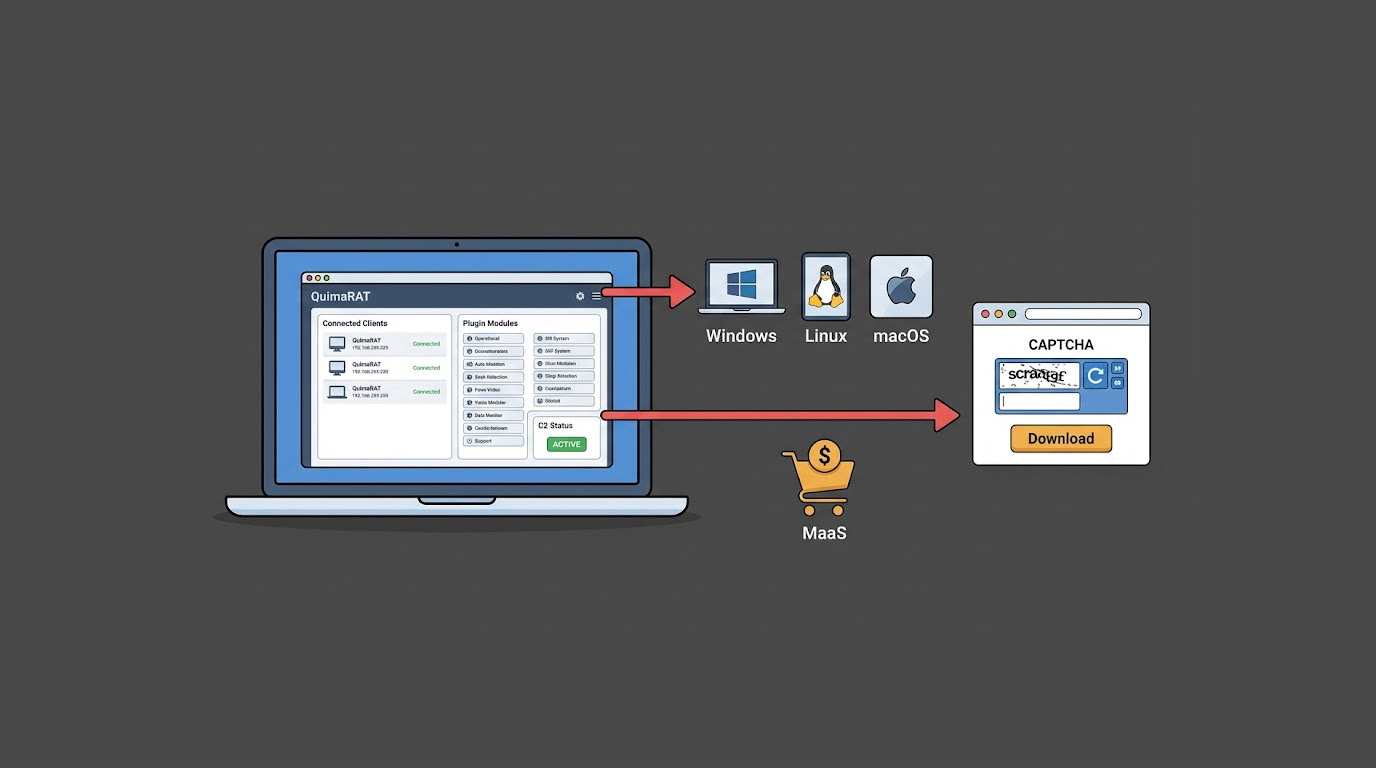
QuimaRAT, which is a new form of Java-based Remote Access Trojan, can attack systems running on Windows, Linux, and macOS platforms. The malware is offered...
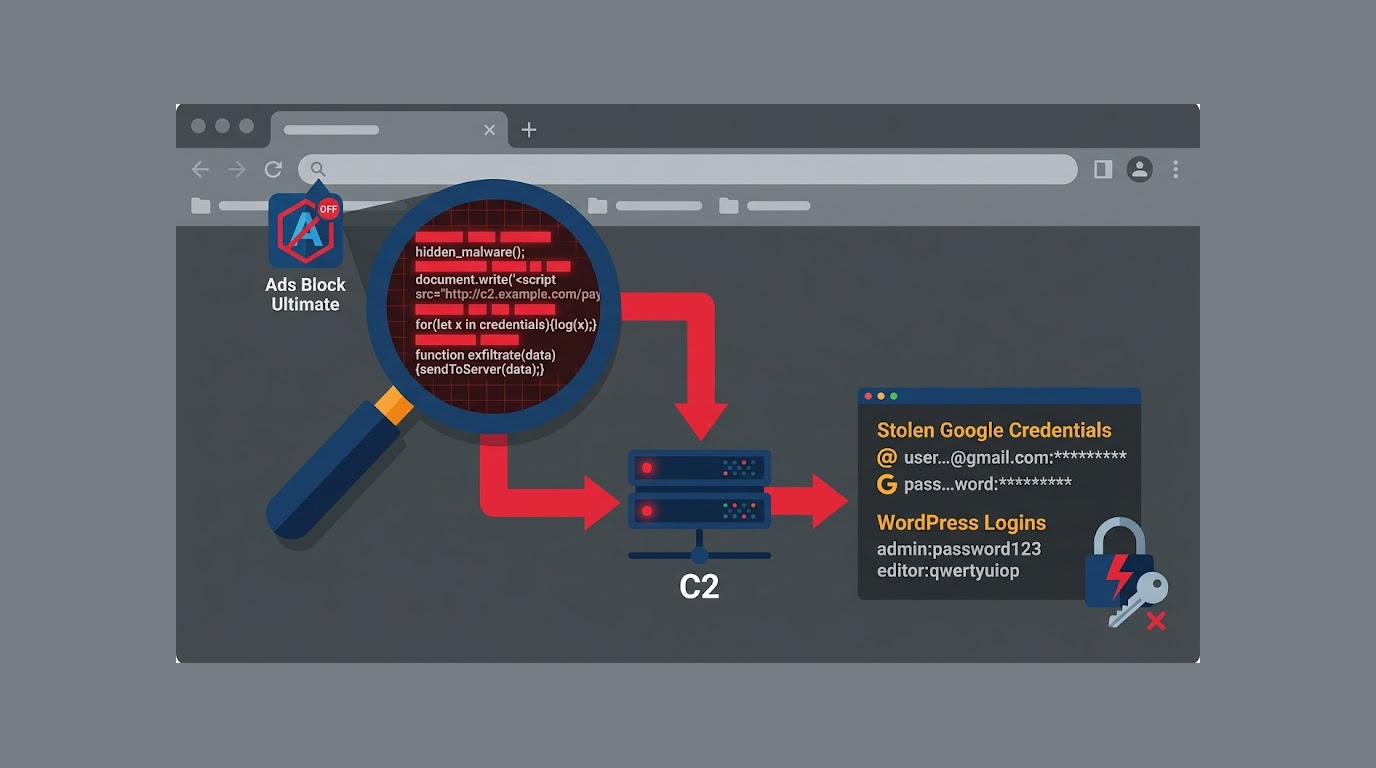
You install an ad blocker. It blocks ads. It has good reviews. You forget about it. For years, it sat quietly in your browser. Then one day, it woke up. I...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067