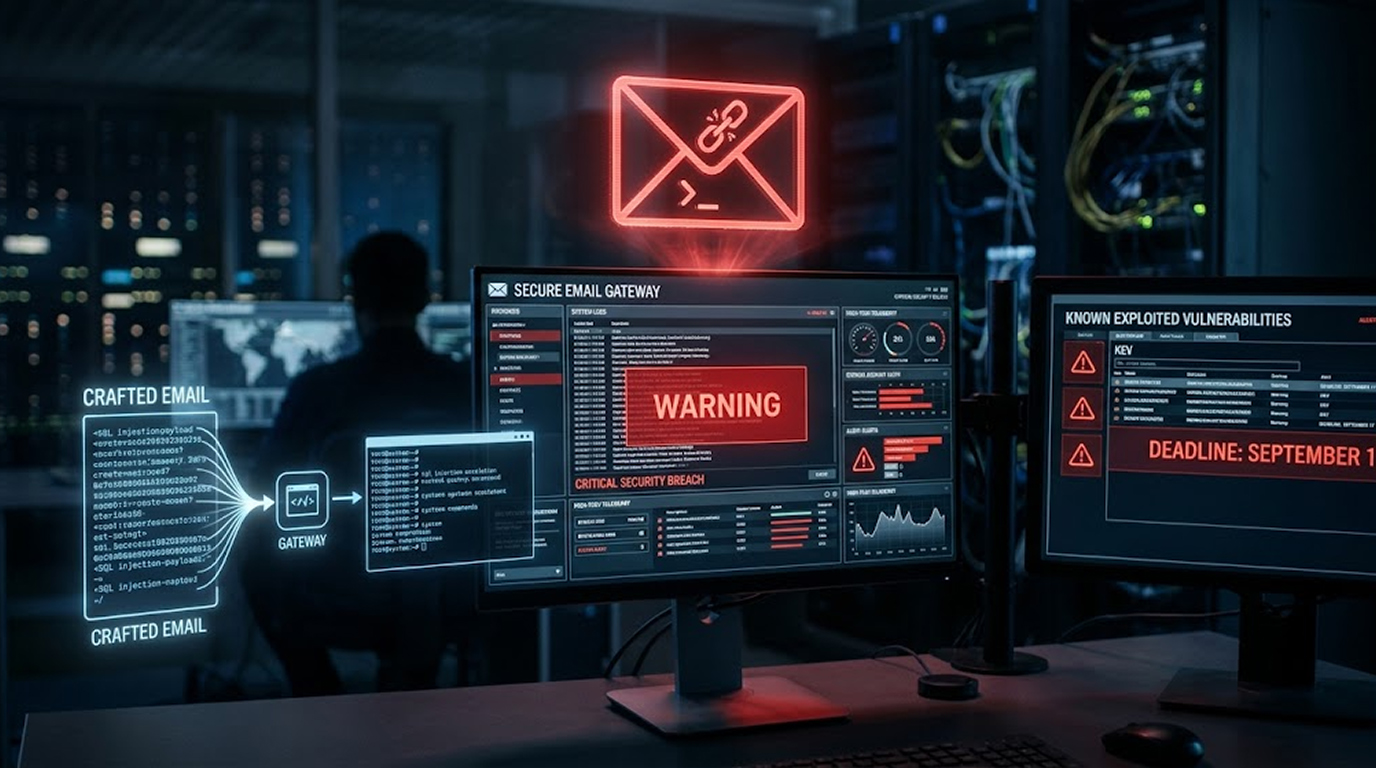
Cisco has a problem. A critical bug in its Secure Email Gateway is being exploited in the wild. An unauthenticated attacker can send a crafted email and get root on the underlying operating system. That's about as bad as it gets.
The vulnerability is CVE-2026-76461. CVSS score: 9.8. Cisco disclosed it on Monday. CISA added it to the Known Exploited Vulnerabilities catalog and gave federal agencies until September 17 to patch.
Let me break down what's going on.
Quick Summary
|
What |
Details |
|
Vulnerability |
CVE-2026-76461 |
|
CVSS |
9.8 |
|
Affected |
Cisco Secure Email Gateway (physical and virtual) |
|
Impact |
Unauthenticated root command execution |
|
Status |
Actively exploited |
|
CISA Deadline |
September 17, 2026 |
What Is the Bug?
It's an insufficient validation issue in the email parsing logic. Cisco's advisory says a crafted email containing malicious SQL statements can trigger the flaw.
"An attacker could exploit this vulnerability by sending a crafted email message that contains malicious SQL statements through an affected device," Cisco said. "A successful exploit could allow the attacker to execute arbitrary SQL statements, leading to command execution with root privileges on the underlying operating system."
So the chain is: email in, SQL injection, command execution as root. No login. No credentials. Just an email.
Who's Affected?
Cisco Secure Email Gateway, both physical and virtual appliances. The bug affects devices regardless of configuration.
Not affected:
- Cisco Secure Email and Web Manager
- Cisco Secure Web Appliance
So if you're running one of those, you can breathe. If you're running Secure Email Gateway, you need to move.
The Fix
Cisco released patches for these versions:
|
Version |
Fixed In |
|
15.5 and earlier |
15.5.5-0141 |
|
16.0 |
16.0.4-302 |
|
16.5 |
16.5.0-780 |
There are no workarounds. You have to update. That's it.
How to Check for Compromise
Cisco shared some indicators of compromise. Here's what to do.
1. Check your mail logs.
Look for suspicious SQL statements. Cisco recommends running this command:
cisco-esa> grep -i "COPY.*TO PROGRAM" [mail_logs]If anything shows up, that's bad. The COPY ... TO PROGRAM pattern is a common way to turn SQL injection into command execution.
2. Check cluster logs.
If your device is part of a cluster, check every node. Don't assume one is clean just because the others are.
3. Look outside the device.
This is important. Cisco warns that because the attacker gets root, they can cover their tracks. Evidence may be deleted or hidden. So you can't just trust the device's own logs.
- Check your network logs. Check your firewall logs. Look for:
- Unexpected uploads from the email gateway to external IPs
- Downloads from known malicious IPs
- Any unusual outbound traffic
4. Cisco is contacting some customers directly.
Cisco said it has reached out to customers who own Cisco Secure Email Cloud devices where malicious activity was detected. It didn't say how many. It didn't say how big the campaign is.
The CISA Deadline
CISA added CVE-2026-76461 to the KEV catalog. Federal Civilian Executive Branch agencies have until September 17, 2026, to patch.
That's a short window. It reflects the severity. Root command execution on an email gateway is a serious problem. That device sits at the edge of your network. It processes all your incoming mail. If someone owns it, they own a lot.
Meanwhile: Fortinet VPN Credential Attacks
The Cisco disclosure comes just days after Arctic Wolf reported large-scale credential attacks against Fortinet VPN appliances.
The attacks happened in late August 2026. Two sustained waves. August 26 through August 28. Tens of millions of authentication failures across multiple U.S. customer environments.
What made these attacks different?
The attackers weren't just spraying generic usernames. They used organization-specific usernames. Corporate email addresses. Affiliate accounts. Common administrative identities.
"The attempted usernames included employee names, corporate email addresses, affiliate identities, and common administrative accounts associated with the targeted organizations," said researcher Kyle Siddall. "This targeted identity selection, rather than generic username spraying, indicates access to previously collected or enumerated identity information."
In other words, the attackers did their homework. They knew who worked at these companies. They knew their email addresses. They used that information to make their attacks more convincing.
One success:
Arctic Wolf observed at least one successful Fortinet VPN authentication from IP 158.94.211[.]14. That was followed by malicious activity in the affected environment. So at least one of these attacks worked.
What You Should Do
For Cisco Secure Email Gateway:
- Patch immediately. Update to 15.5.5-0141, 16.0.4-302, or 16.5.0-780.
- Check your logs. Run the grep command. Look for COPY.*TO PROGRAM.
- Check network and firewall logs. Don't trust the device's own logs alone.
- Look for outbound anomalies. Unexpected uploads or downloads from the gateway.
- If you're in a cluster, check every node.
For Fortinet VPN:
- Enable Multi-Factor Authentication (MFA). It will be very hard to conduct any credential attack with two-factor authentication enabled.
- Protection from credential stuffing attack. One needs to be cautious about multiple logins from single IPs or IP ranges.
- Look out for successful logins from unusual locations. If you see a login from a country you don't operate in, investigate.
- Review your user lists. Are there accounts that shouldn't exist? Remove them.
- Consider IP allowlisting. If your VPN doesn't need to be reachable from everywhere, restrict it.
The Bottom Line
Cisco Secure Email Gateway has a critical RCE bug. CVE-2026-76461. CVSS 9.8. Unauthenticated attacker sends a crafted email, gets root. It's being exploited. Patch now. Check your logs. Don't trust the device alone.
And keep an eye on your Fortinet VPN. Credential attacks are ramping up. Targeted ones, not just generic spraying.
Quick Reference:
|
Key Point |
Detail |
|
Cisco Bug |
CVE-2026-76461 |
|
CVSS |
9.8 |
|
Impact |
Unauthenticated root command execution |
|
Fixed Versions |
15.5.5-0141, 16.0.4-302, 16.5.0-780 |
|
CISA Deadline |
September 17, 2026 |
|
Fortinet Attacks |
Late August 2026, tens of millions of failures |
What to Do:
- Patch Cisco Secure Email Gateway immediately
- Check mail logs for COPY.*TO PROGRAM
- Review network and firewall logs
- Enable MFA on Fortinet VPN
- Monitor for credential stuffing
FAQ Section
What is CVE-2026-76461?
A critical vulnerability in Cisco Secure Email Gateway. It lets an attacker who is not authenticated to execute SQL statements and commands in the underlying operating system as root.
How is the attack conducted?
An email with the malicious SQL statements is sent by the attacker. The SQL statements are not validated correctly by the email parser, which results in SQL injection and root command execution.
Which versions are affected?
Cisco Secure Email Gateway 15.5 and earlier, 16.0, and 16.5. Fixed in 15.5.5-0141, 16.0.4-302, and 16.5.0-780.
Is it being exploited?
Yes. Cisco became aware of active exploitation this month. CISA added it to the KEV catalog.
What should I do?
Patch immediately. Check mail logs for COPY.*TO PROGRAM. Review network and firewall logs. Don't trust the device's own logs alone.