Prompt Injection + SQL Injection: Hybrid Attack That Breaks All
You have heard about prompt injection. You have heard about SQL injection. Both are dangerous on their own. But what happens when they combine? Attackers...
Found 4 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have heard about prompt injection. You have heard about SQL injection. Both are dangerous on their own. But what happens when they combine? Attackers...
SQL injection (SQLi) is still among the top Web App Vulnerabilities due to both its high cost and long-standing existence over 20 years. SQLi continues to...
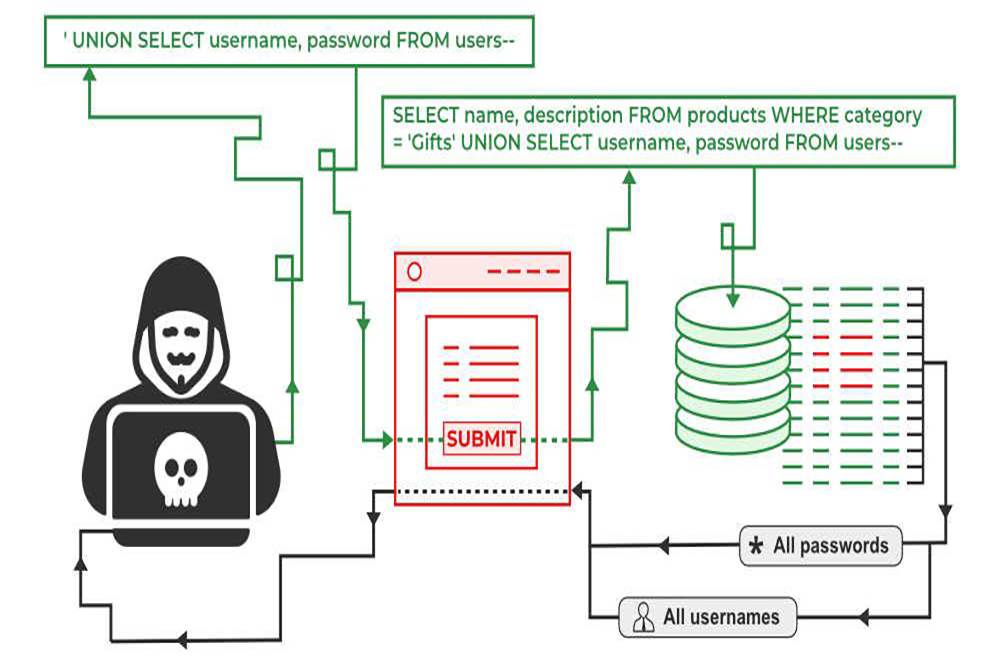
SQL injection (SQLi) is one of the most dangerous web application vulnerabilities, allowing attackers to manipulate databases and extract sensitive data. E...
SQL injection (or SQLi) attacks alter SQL queries by injecting malicious code through application vulnerabilities. SQLi attacks that are successful allow a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067