Elementor CSRF Flaw Lets Attackers Create Admin Accounts
A high-severity flaw in the Elementor Website Builder plugin could let an unauthenticated attacker create rogue administrator accounts and take full contro...
Found 8 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A high-severity flaw in the Elementor Website Builder plugin could let an unauthenticated attacker create rogue administrator accounts and take full contro...
You know the drill. Traditional penetration testing takes forever. It costs a fortune. And it happens once or twice a year, if you are lucky. Static scann...
GitLab has issued a security patch for a critical security vulnerability. It impacts Community Edition as well as the Enterprise Edition of GitLab. It will...
What if, for example, one of your staff members clicks on an apparently safe link, only to have an autonomous AI agent start operating within your company...
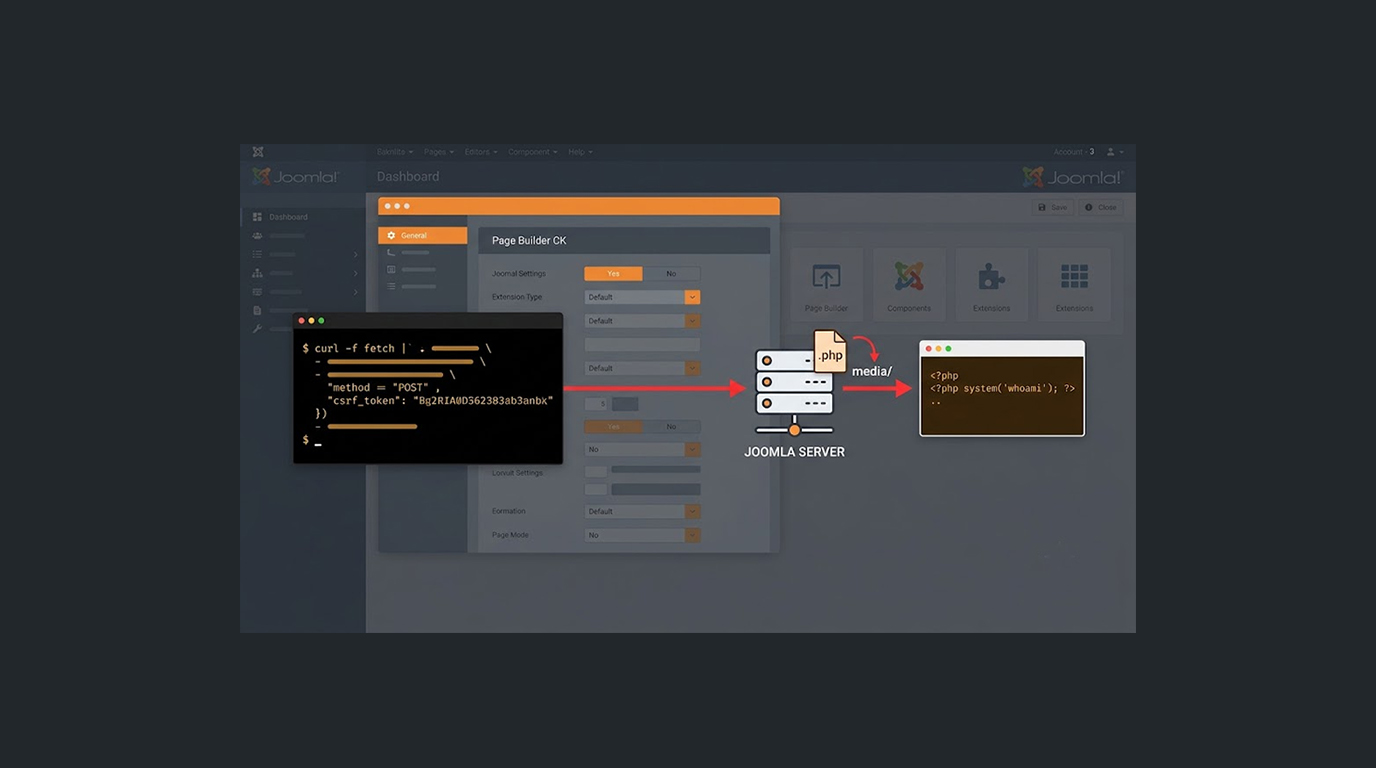
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
Cross-Site Request Forgery (CSRF) attacks are one of the most underrated web attacks, and this is even more common in legacy applications, particularly in...
Version 1.8.2 of YOURLS has a security flaw that allows authenticated users to be victimized by a CSRF attack. An attacker could log an authenticated user...
On 2025-10-23 a Cross-Site Request Forgery (CSRF) weakness was reported in Casdoor v2.95.0 (release date 2025-10-22). The vulnerable endpoint (/api/set-pas...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067