Network Interception for Tokens: When HTTPS Isn't Enough
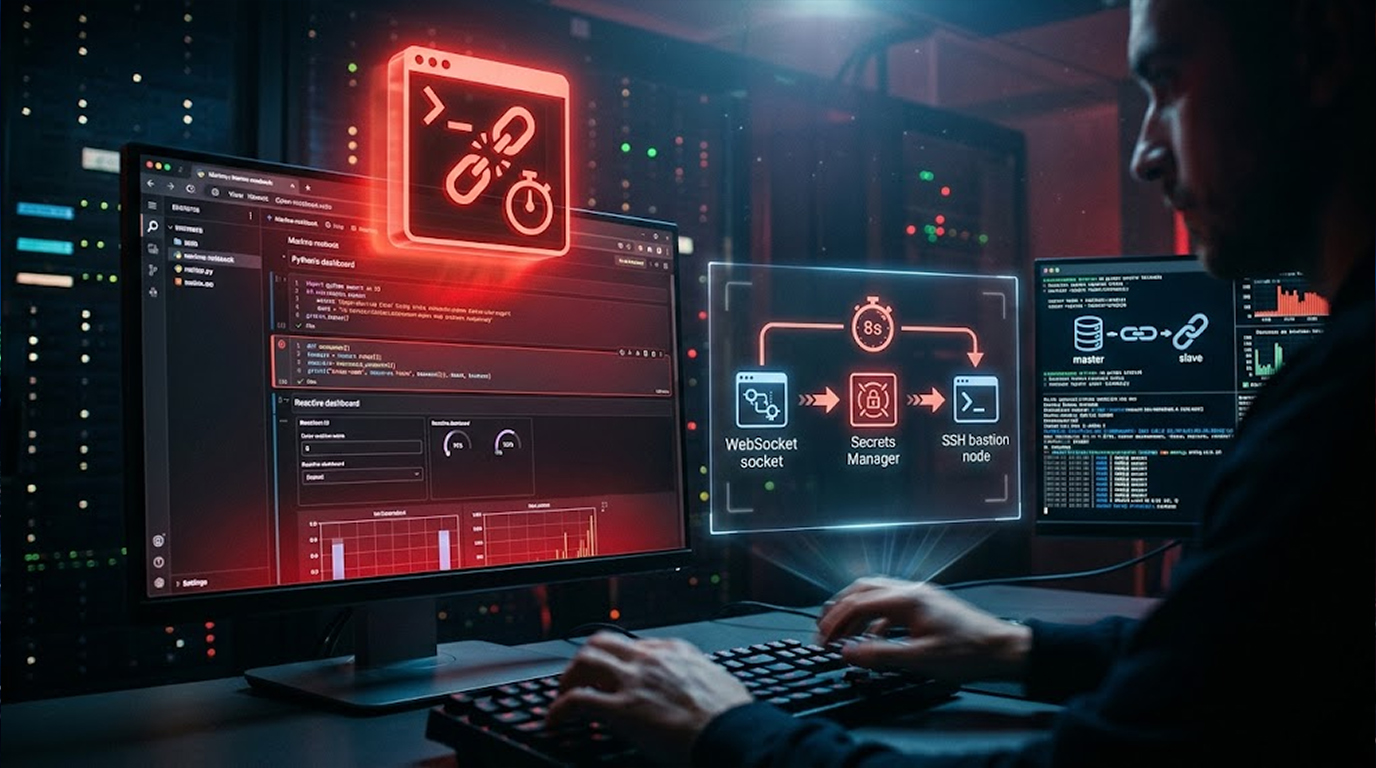
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
There is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumption is wrong in more ways than most people real...
Read Full ArticleThere is a comfortable assumption most teams carry around, and it sounds like this, we use HTTPS everywhere, so tokens are safe in transit. That assumptio...
Everyone's talking about how AI is speeding up attacks. And it is. But here's the thing. Skilled humans can still move just as fast. Sometimes faster. Sys...
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
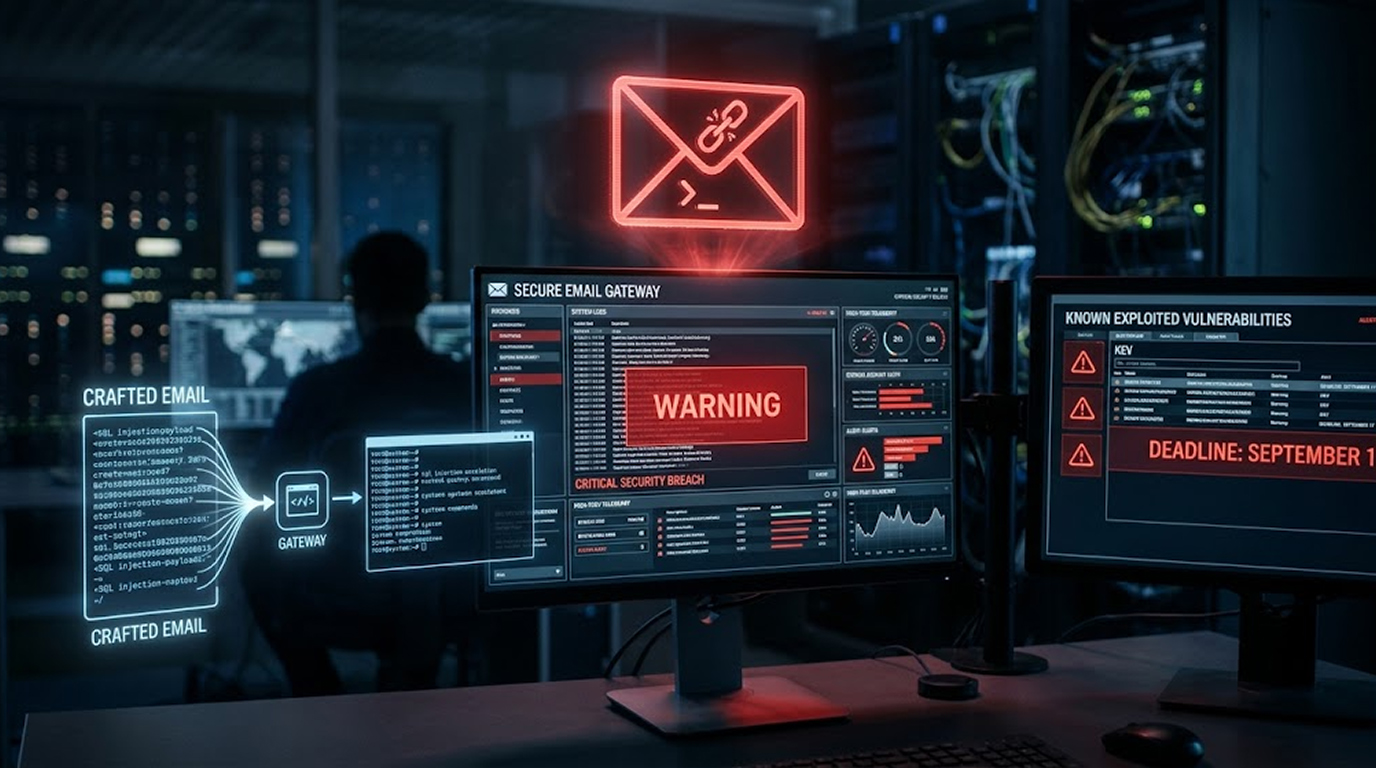
Cisco has a problem. A critical bug in its Secure Email Gateway is being exploited in the wild. An unauthenticated attacker can send a crafted email and ge...
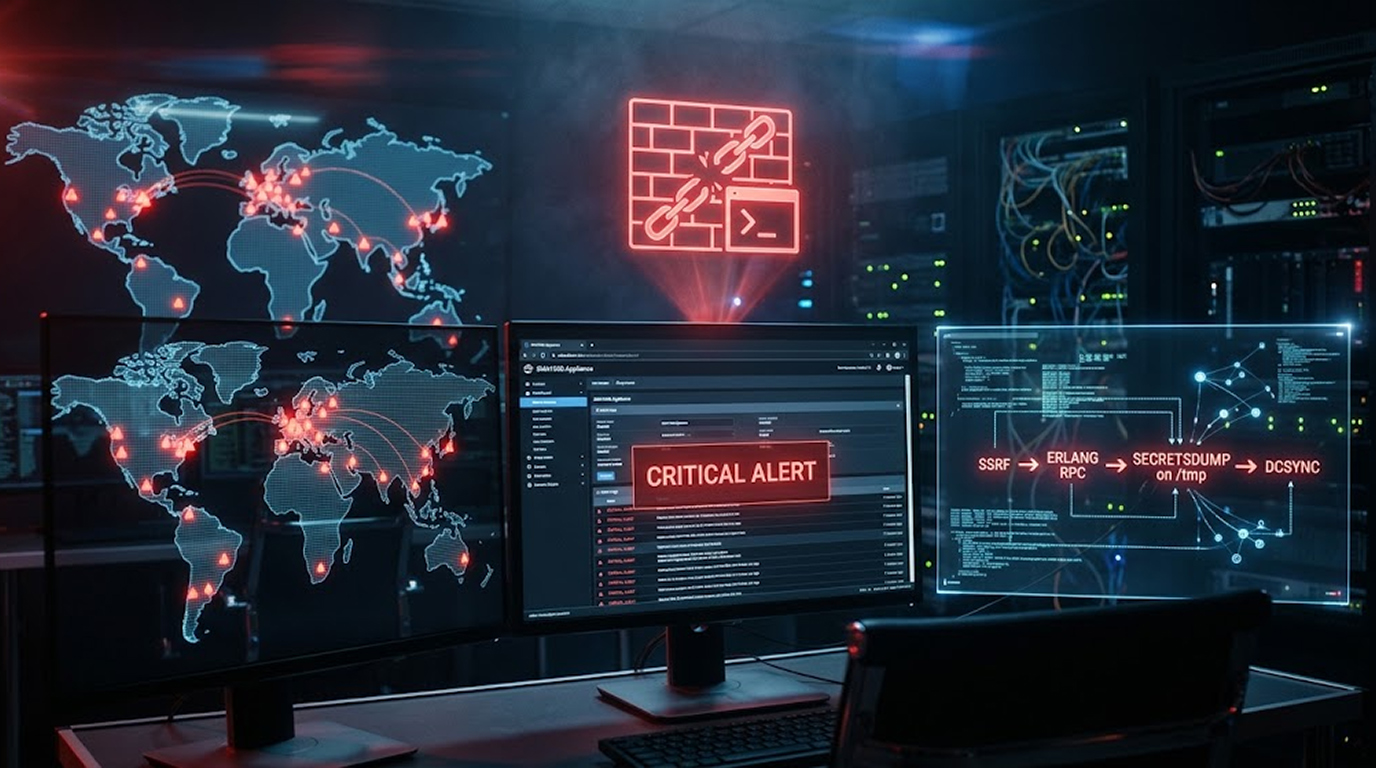
Two days. That's all it took. SonicWall disclosed CVE-2026-15409 on July 14, 2026. By July 16, someone was already scanning for vulnerable appliances at sc...
A Chinese threat actor just pulled off a nasty attack chain. They used two Chrome bugs and one Windows flaw to drop a JavaScript backdoor called GRIMWEDGE....
An attacker got inside 3BB, one of Thailand's biggest broadband providers. They didn't just visit. They set up shop, moved around, and went after customer...
Here's a weird one. A flaw in Telegram Desktop let a bot slip JavaScript into your chat exports. If you saved a chat as an HTML file and opened it in a bro...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067