APT37 Uses Facebook Pretexting to Deliver RokRAT Malware
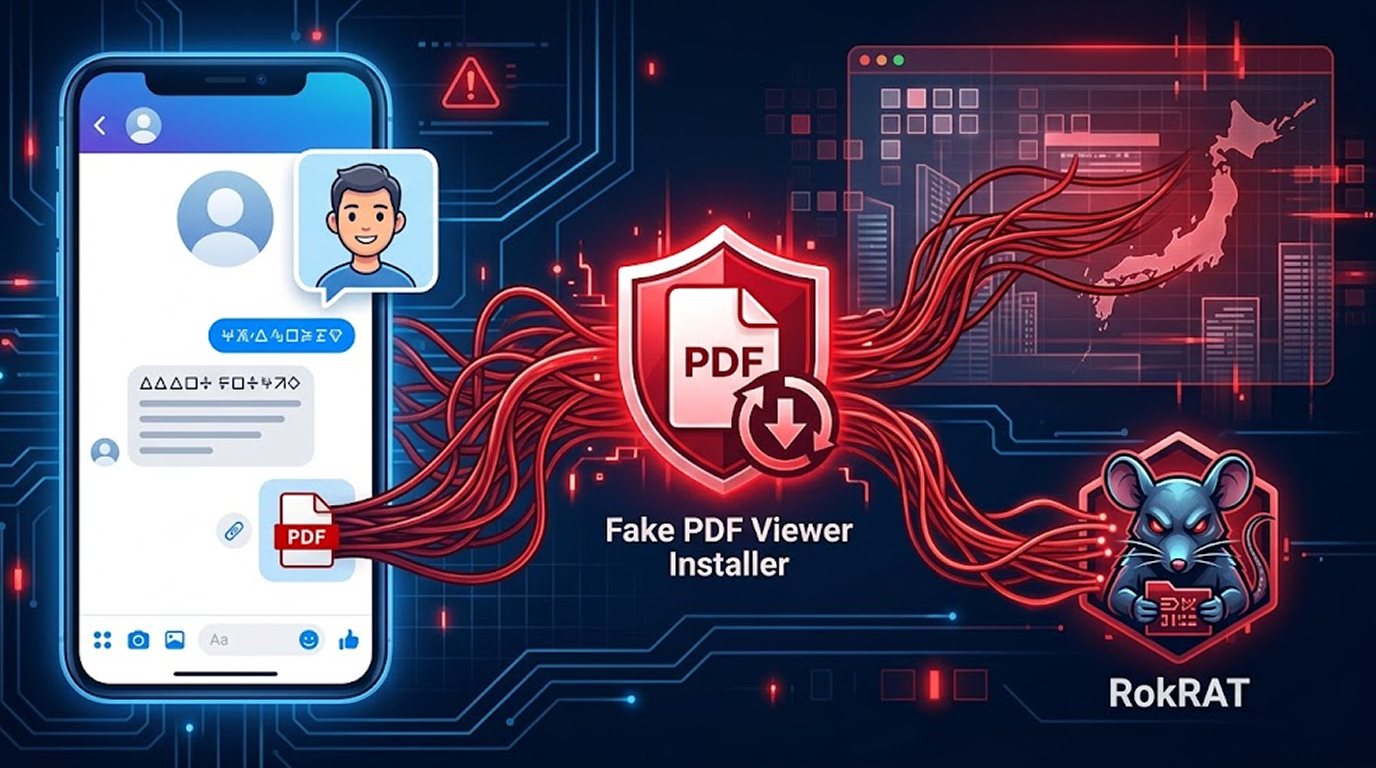
The North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliv...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
The North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliver the remote access trojan RokRAT. Accordin...
Read Full ArticleThe North Korean hacking group known as APT37 (also called ScarCruft) has been linked to a targeted social engineering campaign that uses Facebook to deliv...
The Predator is one of the most sophisticated mercenary spyware platforms still in existence. Initially birthed as a covert monitoring solution for commerc...
Many organizations invest heavily in security tools, training completion rates, and compliance checklists, yet these often do not lead to a reduction of ac...
A lot of people think that their phones' cameras only turn on when they use the camera app. However, malicious apps can activate either the front or back c...
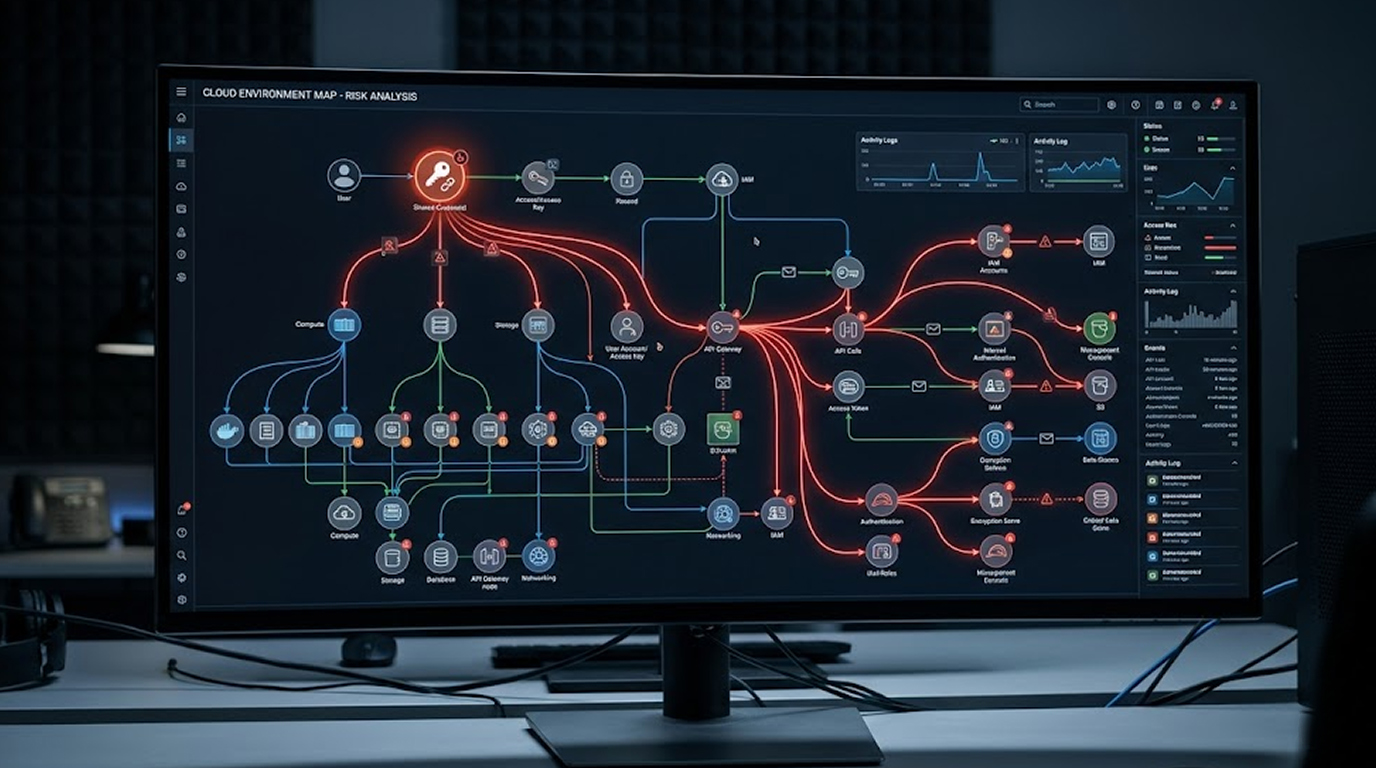
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
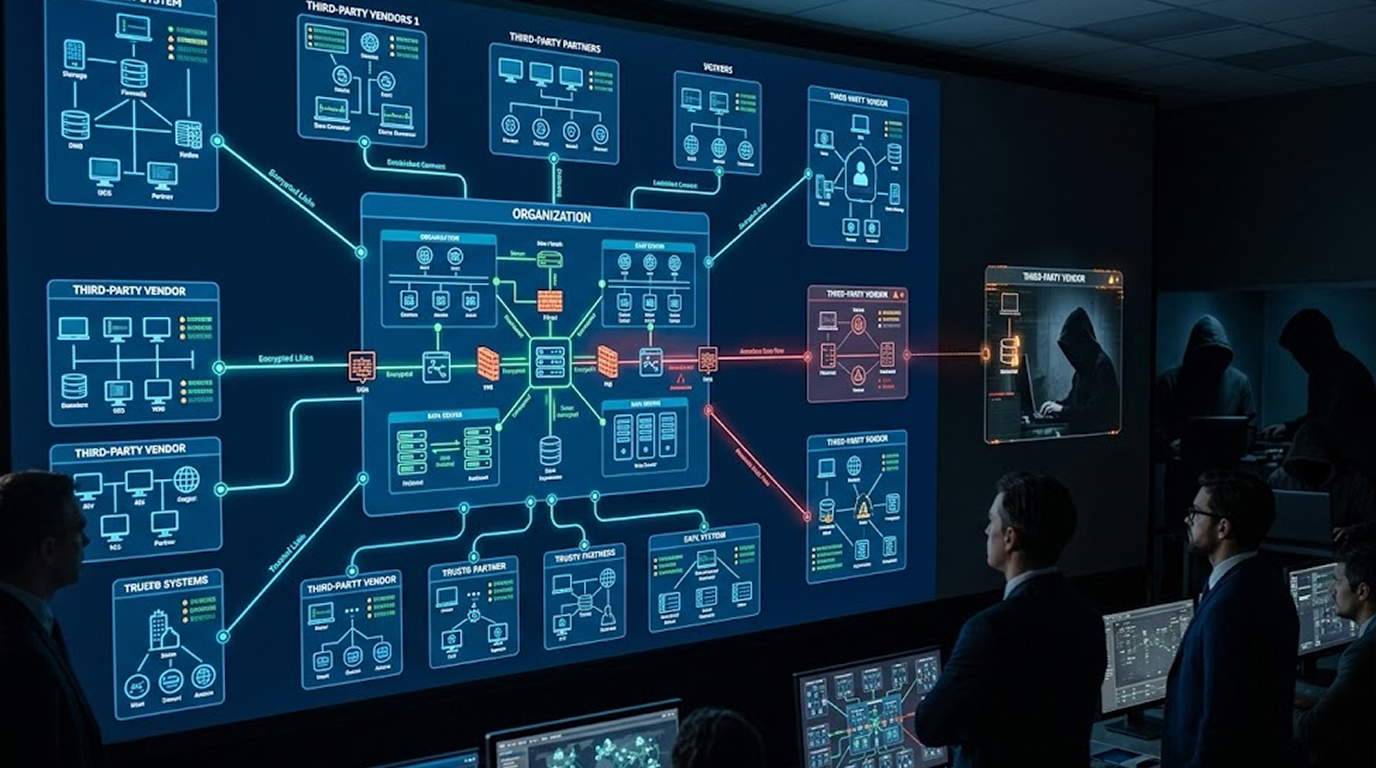
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
New malware called STX RAT was discovered as the first RAT to be able to use invisibility techniques and perform a variety of operations. This was first se...
A privilege escalation vulnerability has been identified in NetBT e-Fatura, a widely used electronic invoicing solution in Turkey. Tracked as CVE-2025-140...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067