AIT-GUI NASA Flaw Allows Unauthenticated Spacecraft Commands
Security researchers just found a vulnerability in software used by NASA's Jet Propulsion Laboratory. The flaw is in AIT-GUI, the browser-based console tha...
Found 7 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Security researchers just found a vulnerability in software used by NASA's Jet Propulsion Laboratory. The flaw is in AIT-GUI, the browser-based console tha...
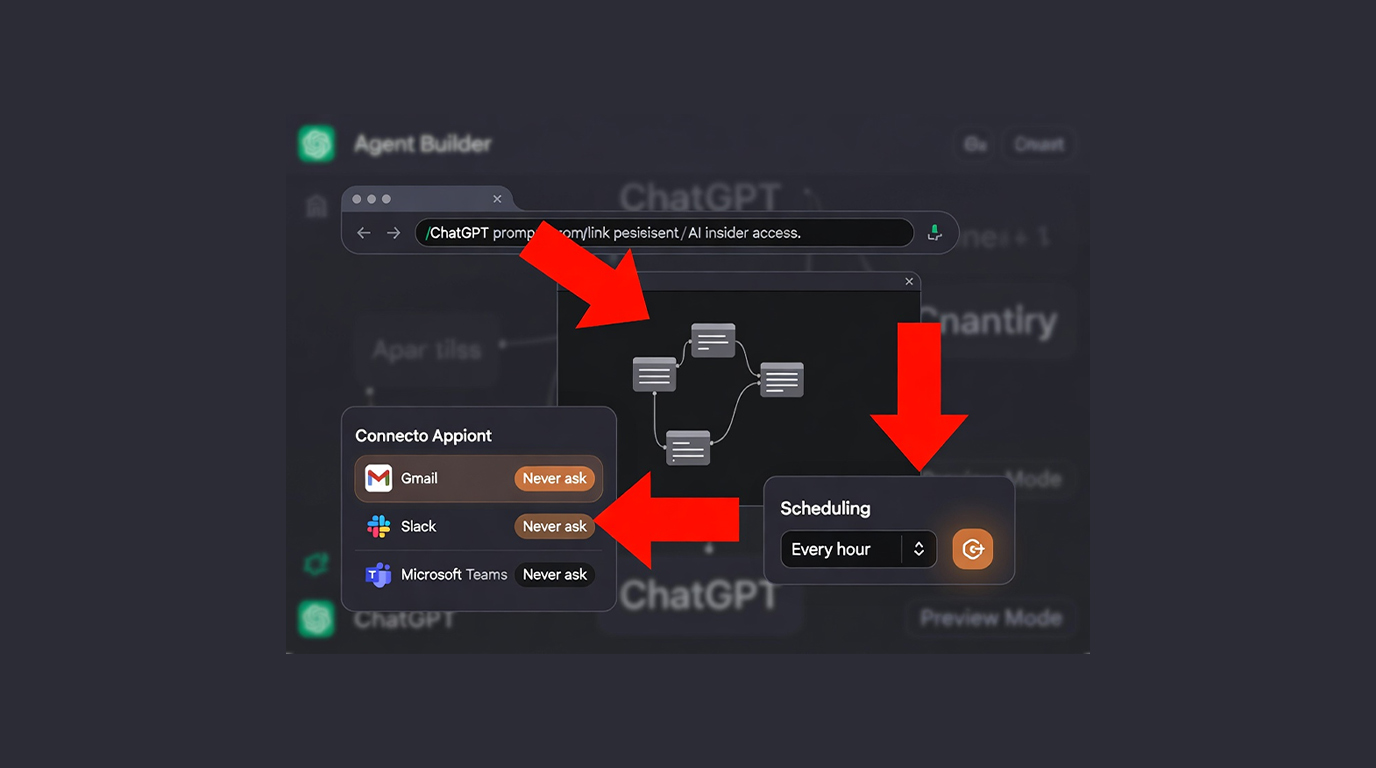
What if, for example, one of your staff members clicks on an apparently safe link, only to have an autonomous AI agent start operating within your company...
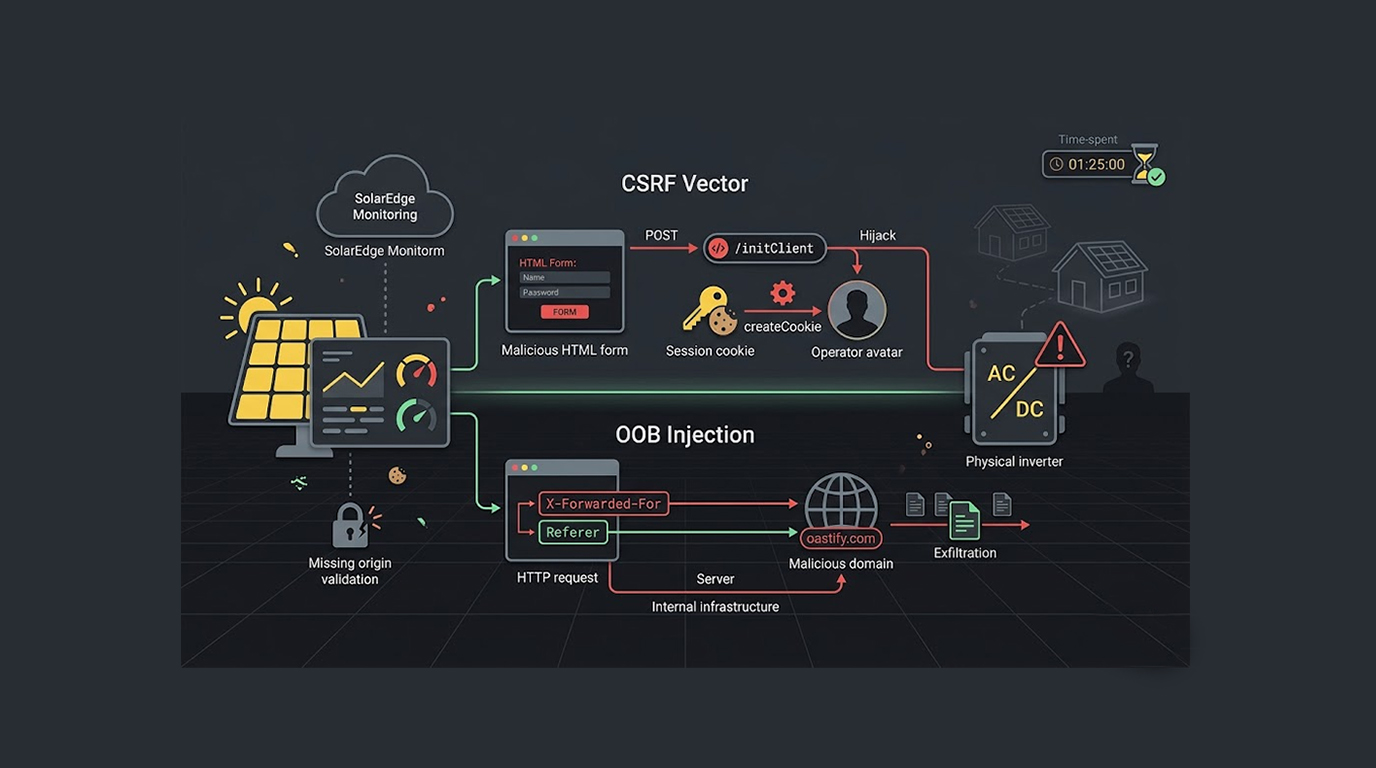
An essential flaw within the SolarEdge monitoring platform's business logic permits the takeover of an operator's session by an attacker, which will allow...
Piranha CMS version 12.0, which was released approximately halfway through 2025, has a stored cross-site scripting (XSS) vulnerability (CVE-2025-57692). An...
Cross-Site Request Forgery (CSRF) attacks are one of the most underrated web attacks, and this is even more common in legacy applications, particularly in...
Version 1.8.2 of YOURLS has a security flaw that allows authenticated users to be victimized by a CSRF attack. An attacker could log an authenticated user...
You’d think by 2025, developers would have session management nailed, right? Sadly, that’s not the case. I’ve worked on enough web apps t...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067