VEILDrive Attack Campaign Abuses Microsoft SaaS to Deliver Malware
A sophisticated new threat campaign dubbed VEILDrive is leveraging legitimate Microsoft SaaS services — including Teams, SharePoint, Quick Assist, an...
Found 214 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A sophisticated new threat campaign dubbed VEILDrive is leveraging legitimate Microsoft SaaS services — including Teams, SharePoint, Quick Assist, an...
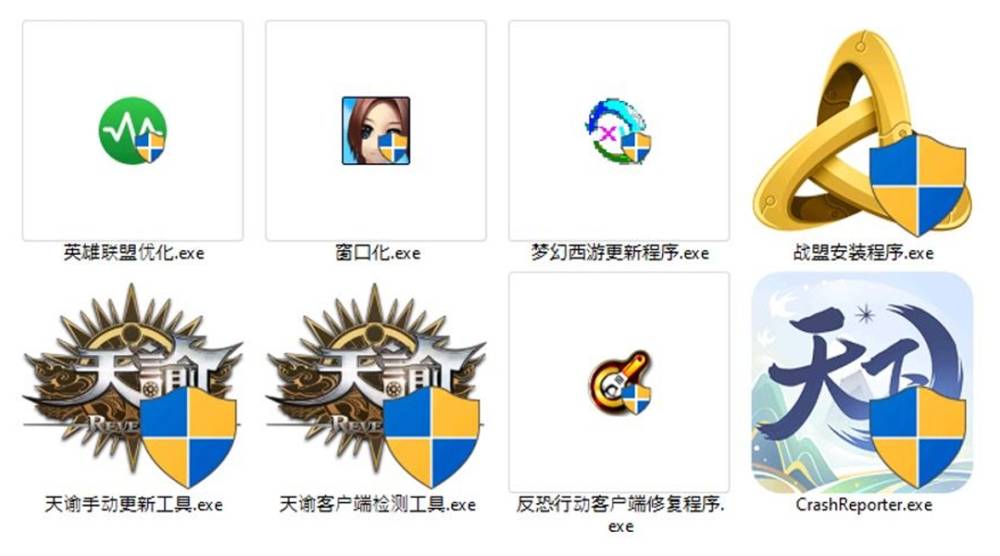
Cybersecurity experts warn that a newly enhanced malware framework, Winos 4.0, is targeting users through gaming-related apps like installation tools, spee...
Researchers have identified a new strain of Android malware, ToxicPanda, that has infected over 1,500 devices worldwide, predominantly targeting banking us...
The cryptojacking group TeamTNT appears poised for a large-scale attack campaign, setting its sights on cloud-native environments to exploit resources for...
Grandoreiro, a banking malware active since 2016, continues to evolve with new tactics aimed at bypassing anti-fraud measures. Despite law enforcement effo...
Russian-speaking users have become the focus of a sophisticated phishing campaign using Gophish, an open-source phishing toolkit, to deliver two remote acc...
The notorious Chinese nation-state actor APT41, also known as Brass Typhoon, Earth Baku, Wicked Panda, or Winnti, has been linked to a highly sophisticated...
The Russian cyber threat group RomCom has been linked to a series of cyber attacks targeting Ukrainian government agencies and Polish organizations since l...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067