Browser‑Based Attacks in 2026: Risks, Tools, and Examples
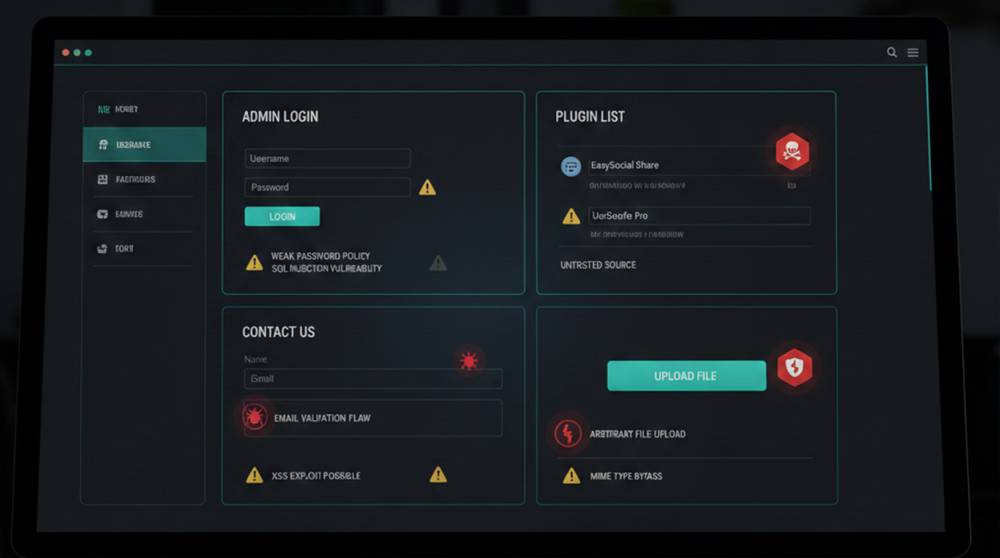
In 2026, most work still happens in a browser.Email, cloud apps, admin panels, dashboards, internal tools all run there.Attackers know this.Instead of brea...
Found 28 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
In 2026, most work still happens in a browser.Email, cloud apps, admin panels, dashboards, internal tools all run there.Attackers know this.Instead of brea...
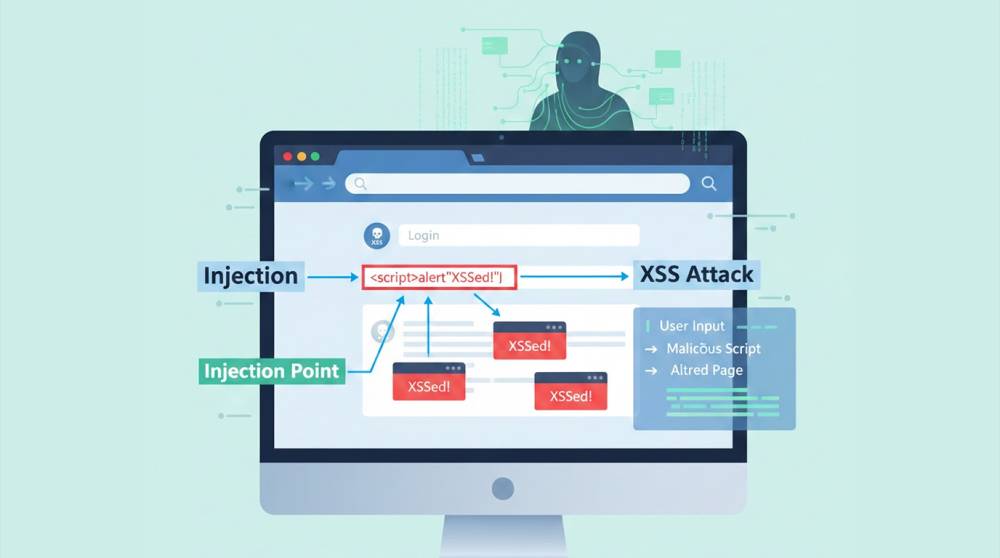
Most teams already run scanners.Many still miss XSS.That’s because XSS is rarely a simple input problem.It’s a data-flow and context problem.Re...
Cross Site Scripting, usually called XSS, happens when a website shows user input without properly checking it first.In simple terms:the website trusts dat...
Not every compromised website is used to steal data or deploy malware.Many are repurposed quietly to generate traffic.The site stays online.Pages still loa...
Breaking web apps usually doesn’t start with zero-days or Hollywood hacking.It starts with someone opening the same tools developers and testers alre...
Some website attacks are predictable, yet they continue to work year after year.Not because attackers are unusually clever but because the same weak spots...
How to Know If Your Website Is Hacked If your website is hacked, you will usually notice unusual behavior such as redirects, unknown files, or sudden traf...
If you’ve ever walked into an office and seen a CMS screaming about “12 updates available,” you already know how this story starts. Most...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067