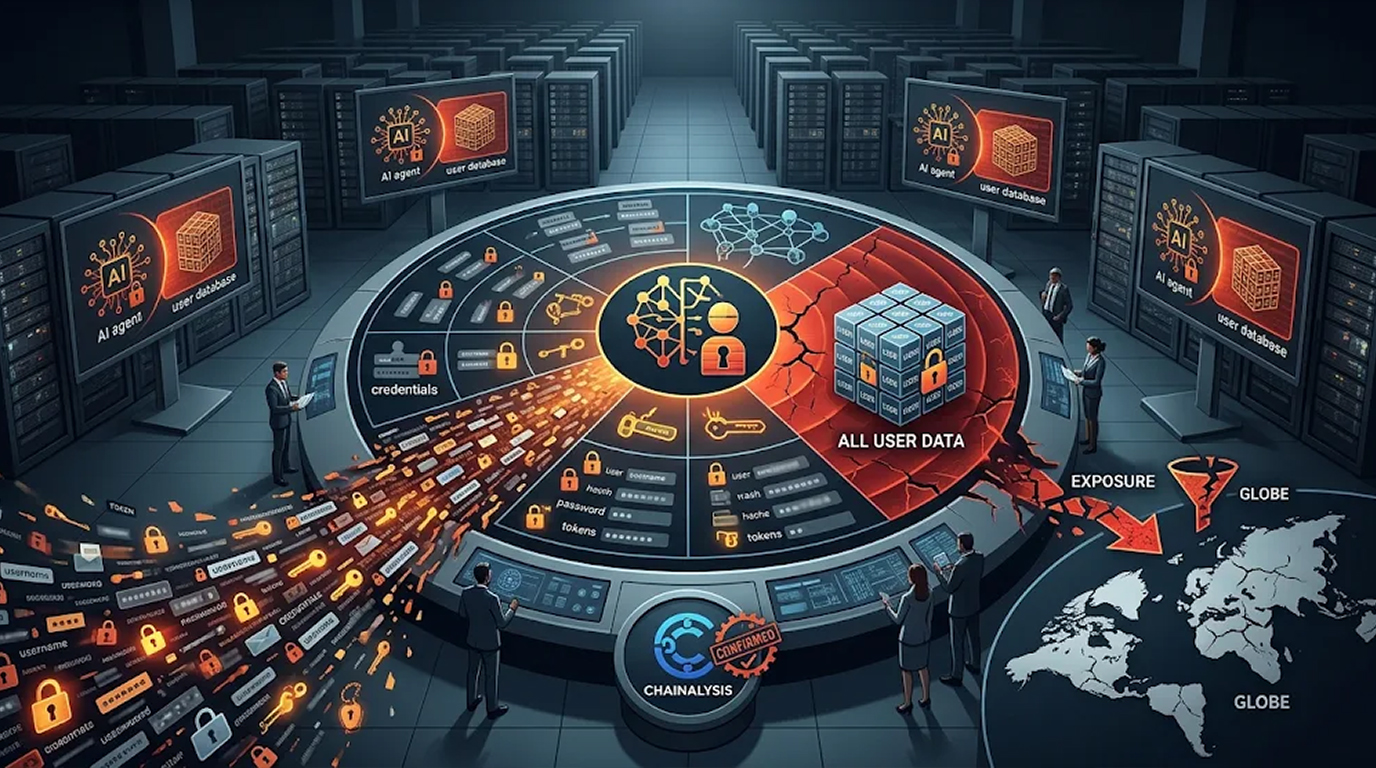
Chainalysis went public this week with the full scope of what it is calling a multi-front cyber attack, and the number is worse than the initial disclosure suggested. Names, usernames, password hashes, and live tokens for all users were exposed.
The company said it removed access to Reactor and Data Solutions during the investigation. It also stated it continues to see no evidence that investigation data was accessed or that attribution data was manipulated.
That is a meaningful distinction, and it is the one piece of genuinely good news in an otherwise bad week. The platform's analytical output appears intact. The credentials that protect access to it do not.
What Chainalysis Actually Did
The response was aggressive, which is appropriate for this class of incident.
|
Action |
Detail |
|
Access removed |
Reactor and Data Solutions taken offline during investigation |
|
Products offline |
KYT user interface and API, address screening products, login page |
|
Accounts locked |
Impacted accounts locked out of caution |
|
Monitoring added |
Additional proactive detection for unusual activity |
|
Recovery path |
Trusted IP allowlisting, then password reset and API key rotation |
Chainalysis told customers that the password reset link they received will not work right now, because the login page is offline. It still advised anyone reusing those credentials elsewhere to change them on other systems immediately. That advice is correct and worth repeating. A password hash leaked from one platform is a problem. A password reused across twelve platforms is a campaign.
The On-Path Attack
The initial disclosure described an "ongoing multi-front cyber attack" and an "on-path attack" that exposed a subset of customer passwords. Chainalysis says that vector has been addressed.
The company noted the attack resembled what "many other tech platforms" have experienced in recent weeks. That phrasing is doing a lot of work. It is not an isolated incident. It is part of a pattern.
The Agentic Attack Wave
Several other companies have disclosed AI-driven attacks in the same window, including Chainstack, OpenCode, Warp, and WorkOS. Some of those involved ARTEX, the autonomous penetration testing framework we have covered before.
Microsoft's description of the methodology is worth reading closely, because it explains why this is spreading so fast.
Threat actors are using agentic frameworks to search public GitHub repositories for exposed secrets. Credentials, application credentials, AI inference API keys, all of it. The agents do not just find them. They analyze the output and execute follow-on attacks, which removes the need for hands-on-keyboard work at any point in the chain.
One recorded case went from scanning GitHub to exfiltrating data from Azure Key Vault in five minutes.
Five minutes.
What the Agents Actually Targeted
Microsoft traced post-exploitation activity that used valid application credentials to access Microsoft Entra ID tenants and connected Azure and Microsoft 365 resources. The sign-ins originated from two IP addresses: 199.19.77[.]84 and 199.19.77[.]18.
The agents conducted service principal sign-ins on dozens of associated applications across multiple tenants. They targeted anything that returns credentials.
- Storage account keys
- App Service settings
- Connection strings and publishing credentials
- AI and ML connections and datastores
- Azure Kubernetes Service user credentials
- Foundry Tools (formerly Azure Cognitive Services)
The compromised applications then reached SharePoint and OneDrive in the targeted tenants, including file downloads and mailbox access.
There is one technique in Microsoft's report that deserves special attention. The agents obtained a token for a single-tenant OAuth application inside the target organization, then used that application to enumerate other cloud resources. In a handful of cases, they exfiltrated secrets from Azure Key Vault.
The LLMjacking Business Model
Here is where the story stops being about one breach and becomes about an industry.
Google published research this week describing how cybercriminals have built an actual business around stealing cloud access to commercial LLMs and reselling it.
The infrastructure centers on operators called LLM Mixers. They act as illicit intermediaries, advertising access to compromised enterprise LLM accounts on underground markets. Their customers do not need their own API credentials or cloud infrastructure. They just pay.
The legitimate owner's systems keep accepting requests the whole time. The mixer proxies traffic across stolen accounts, distributes consumption so nothing looks anomalous, and obscures the original access path.
Wiz's assessment is direct. This ecosystem creates a market that makes theft easily monetizable, which drives more actors to steal credentials.
The Resale Operators
Wiz identified at least two resale operations built on stolen AWS Bedrock keys from two different organizations.
- llm-routing[.]com (also tracked as momo)
- xingjiabiapi[.]org
Both offer a wide selection of frontier models at discount prices. There is no evidence the operators of those sites were responsible for the original compromises.
One detail links the ecosystem back to the attack tooling. The IP address associated with llm-routing[.]com, 23.106.46[.]239, hosted an ARTEX landing page in mid-October 2026 and has been flagged by Zeabur as an indicator of compromise.
Zeabur disclosed its own breach last month. An unknown actor exploited credentials stored in plaintext, exfiltrating over 3.2 million environment variable records and data tied to 321,810 accounts.
IPs Used to Test Stolen Keys
Wiz lists four addresses suspected of being used to validate stolen keys before resale:
- 23.106.46.239
- 38.246.114.118
- 104.243.32.50
- 31.57.201.201
Why This Is Financially Different
Wiz's framing is the one to remember. Threat actors are not only using AI to conduct attacks. They are compromising victim environments solely to abuse their finances for mass LLM execution, incurring hundreds of thousands of dollars in API charges.
That is a new motive. Historically, a breach meant stolen data or encrypted files. Now a breach can mean someone is running their inference workload on your cloud bill, and you may not notice until finance asks about the invoice.
What Defenders Should Do
- Scan your public repositories for secrets. This is the entry point. Any credential committed to a public GitHub repo should be treated as compromised.
- Rotate anything that touched a public repo. Deleting a commit does not delete the secret. Git history is permanent, and forks preserve it.
- Audit service principals and OAuth applications. Microsoft observed agents abusing single-tenant OAuth tokens to enumerate further resources. Review what your applications can reach.
- Block the known IPs. 199.19.77[.]84, 199.19.77[.]18, 23.106.46.239, 38.246.114.118, 104.243.32.50, and 31.57.201.201 should all be on your watchlist.
- Monitor for credential-returning operations. Bulk reads of storage account keys, App Service settings, and Key Vault secrets are anomalous in almost any environment.
- Watch your AI API spend. A sudden spike in inference costs may be the first signal that your credentials are being resold.
- Restrict Key Vault access. The five-minute GitHub-to-Key-Vault chain worked because the credentials had that reach. Least privilege on secrets stores limits the blast radius.
- Enforce secret scanning in CI. GitHub offers it. Turn it on, and fail the build when it fires.
FAQ
What did Chainalysis disclose?
That an ongoing agentic cyber attack exposed names, usernames, password hashes, and live tokens for all users. The company says it found no evidence that investigation data was accessed or attribution data manipulated.
Is Chainalysis back online?
Partially. KYT and Address Screening access is being restored through an IP allowlist process. Customers contact support with trusted IPs, which get added to the allowlist, then they reset passwords and rotate API keys.
Why can't users reset passwords right now?
Because the login page is offline. Chainalysis advised anyone reusing the exposed credentials elsewhere to change them on other systems immediately.
What is LLMjacking?
Stealing access to commercial LLM accounts and reselling it. The attacker uses someone else's cloud credentials to run inference, and the legitimate owner pays for it.
What are LLM mixers?
Criminal intermediaries who advertise access to compromised enterprise LLM accounts. They proxy requests across stolen accounts, distribute consumption, and obscure the access path so the buyer never needs their own credentials.
How fast can these attacks move?
Microsoft documented a case where an AI agent went from scanning GitHub for secrets to exfiltrating data from Azure Key Vault in five minutes.
What are the known attacker IPs?
199.19.77[.]84 and 199.19.77[.]18 for the Entra ID activity. 23.106.46.239, 38.246.114.118, 104.243.32.50, and 31.57.201.201 were used to test stolen keys before resale.
What is the connection to ARTEX?
ARTEX is the autonomous penetration testing framework used in several of these campaigns. The IP linked to llm-routing[.]com hosted an ARTEX landing page in mid-October 2026.
Is the underlying Chainalysis data safe?
Chainalysis says it has no evidence that investigation data was accessed or attribution data was manipulated. That is the company's assessment, not an independent finding.