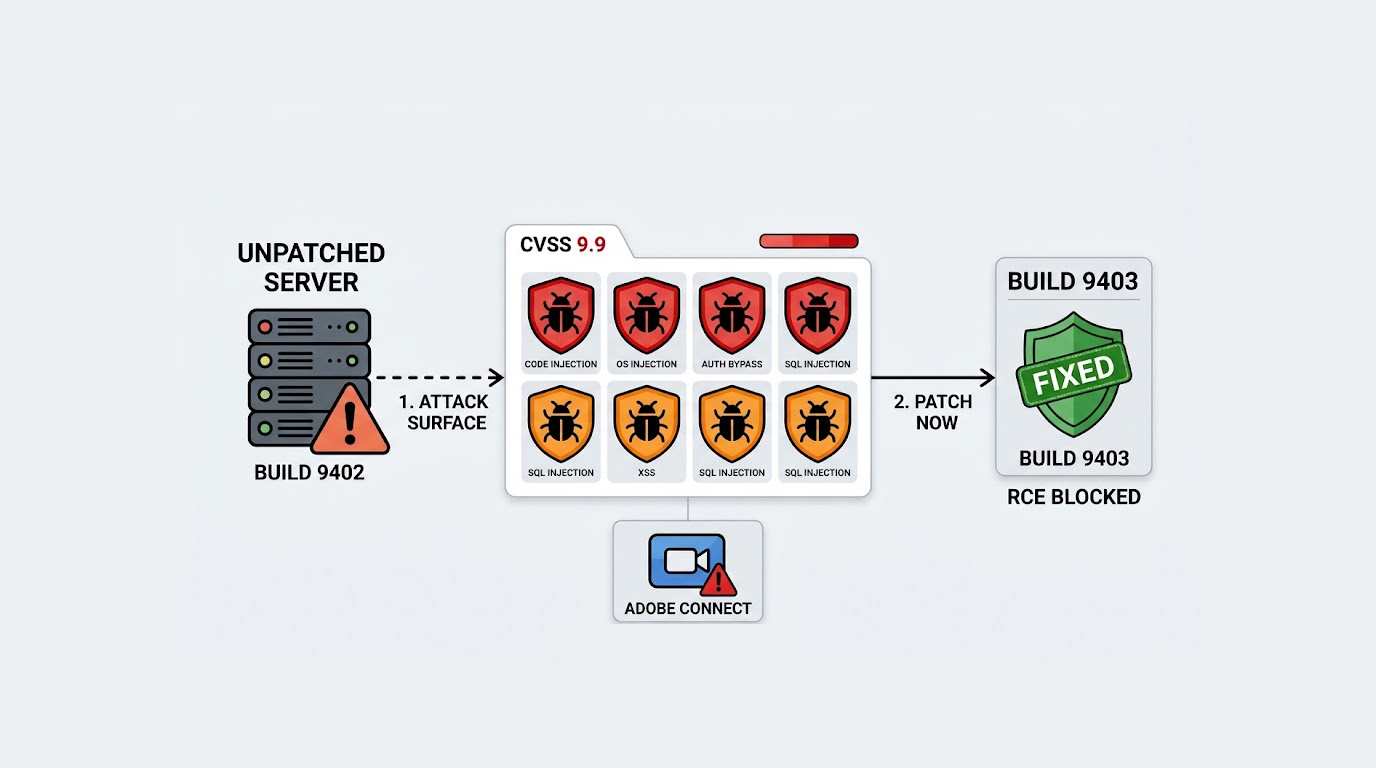
Adobe just dropped a massive security update, and if you are running Adobe Campaign Classic on Windows or Linux, you need to patch your servers right now, because the company just fixed eight critical vulnerabilities, and several of them score a near-perfect 9.9 on the CVSS scale.
These are not minor annoyances. If a bad actor successfully exploits these flaws, they can execute arbitrary code, bypass your security features, and escalate their privileges to take full control of your environment.
The Eight Critical Flaws in Campaign Classic
The issues affect Adobe Campaign Classic versions 7.4.4 build 9402 and earlier, and they have all been patched in version 7.4.4 build 9403.
Here is the breakdown of exactly what Adobe fixed.
|
CVE Identifier |
Vulnerability Type |
Impact |
CVSS Score |
|
CVE-2026-104351 |
Code injection |
Arbitrary code execution |
9.9 |
|
CVE-2026-104353 |
Operating system code injection |
Arbitrary code execution |
9.9 |
|
CVE-2026-105780 |
Incorrect authorization |
Arbitrary code execution |
9.9 |
|
CVE-2026-105489 |
SQL injection |
Security feature bypass |
9.9 |
|
CVE-2026-105781 |
SQL injection |
Security feature bypass |
9.8 |
|
CVE-2026-104350 |
Reflected cross-site scripting |
Privilege escalation |
9.3 |
|
CVE-2026-104354 |
SQL injection |
Security feature bypass |
9.1 |
|
CVE-2026-105779 |
SQL injection |
Security feature bypass |
9.1 |
The Adobe Connect Vulnerability
Campaign Classic is not the only product in the crosshairs, because Adobe also patched a critical code injection flaw in Adobe Connect Desktop and Mobile.
Tracked as CVE-2026-48360 with a 9.6 CVSS score, this flaw could also result in arbitrary code execution on Windows, macOS, and Android. You need to make sure your users are running the fixed versions.
|
Adobe Connect Platform |
Fixed Version |
|
Windows Desktop |
2026.9.61 |
|
macOS Silicon |
2026.10.66 |
|
macOS Intel |
2026.10.170 |
|
Android Mobile |
4.5 |
What Defenders Need to Do Right Now
Adobe says it is not aware of any exploits in the wild for any of the issues addressed in this update, but that is not a reason to wait. The severity of these flaws means a working exploit could surface at any moment.
- Patch Campaign Classic: Upgrade to version 7.4.4 build 9403 immediately on all Windows and Linux servers.
- Adobe Connect Update: Roll out the latest version for both desktop and mobile to all Adobe Connect users.
- Audit exposure: Look for any remaining Campaign Classic environments which may have been overlooked in a test or on a sub-net.
FAQ
What is CVE-2026-104351?
It is a 9.9 severity code injection flaw in Adobe Campaign Classic. If an attacker exploits it, they can run their own code on your server.
Could I be vulnerable while using Adobe Connect?
Certainly, if you use an older version. The vulnerability (CVE-2026-48360) allows the attacker to run any code on Windows, macOS, and Android systems; however, it has been fixed in the latest versions.
How do I fix the Campaign Classic flaw?
You need to upgrade to Adobe Campaign Classic version 7.4.4 build 9403. There is no mention of a workaround, so patching is the only real fix.
Have these vulnerabilities been exploited in the wild?
Adobe says they are not aware of any exploits in the wild for these specific issues. That said, the 9.9 severity scores mean you should treat this as an urgent patch anyway.
Why are there so many SQL injection flaws?
Adobe did not specify why there was a cluster of SQL injection issues in this release. Regardless, all four of them are rated above 9.1 and need to be patched immediately.