Antino Backdoor: How a China-Nexus Actor Hides in Microsoft 365
A spear-phishing email arrives. It looks like a routine message from a trusted sender, and it contains what appears to be an attachment preview, rendered e...
Found 13 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A spear-phishing email arrives. It looks like a routine message from a trusted sender, and it contains what appears to be an attachment preview, rendered e...
You have done everything right. Firewalls. WAF rules. Rate limiting. You feel pretty good about your security posture. Then an AI agent shows up. It does...
Telegram is now a fight for the future. On one side: platform moderators and automated bots are working extra hard to get rid of illegal content (online sc...
Most organizations have a WAF and firewall, but a surprising amount of malicious traffic still slips through because the rules are either too generic or fo...
We’ve entered the phase where the most interesting (and dangerous) cyber conflicts are no longer human hacker vs. human defender. They’re incre...
Automation has quietly changed the balanceCyber-attacks are no longer driven only by people sitting behind screens.Much of the activity now comes from syst...
API abuse rarely announces itself.Requests succeed. Responses are valid. No errors are thrown.From a logging perspective, nothing looks broken.From a busin...
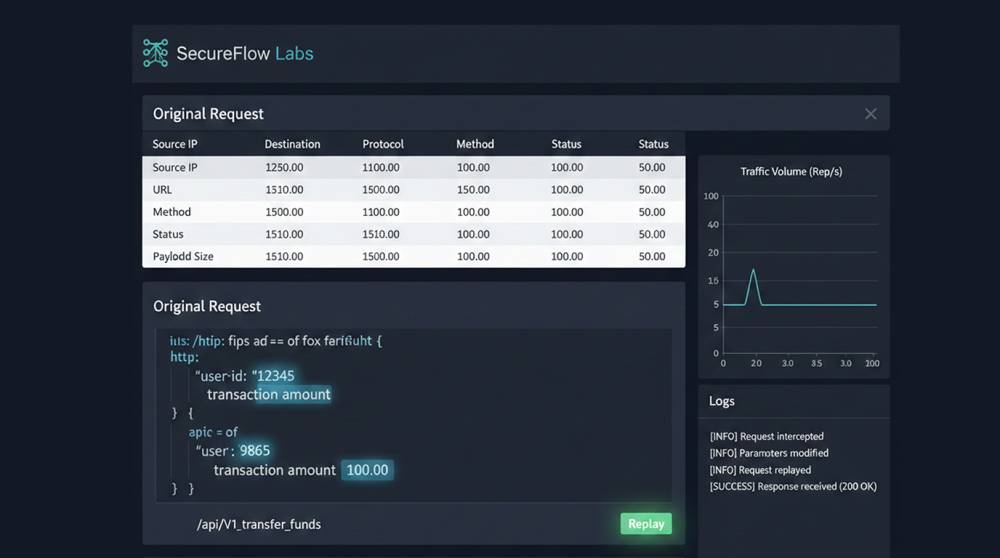
Breaking web apps usually doesn’t start with zero-days or Hollywood hacking.It starts with someone opening the same tools developers and testers alre...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067