Malware Using BSOD as Cover
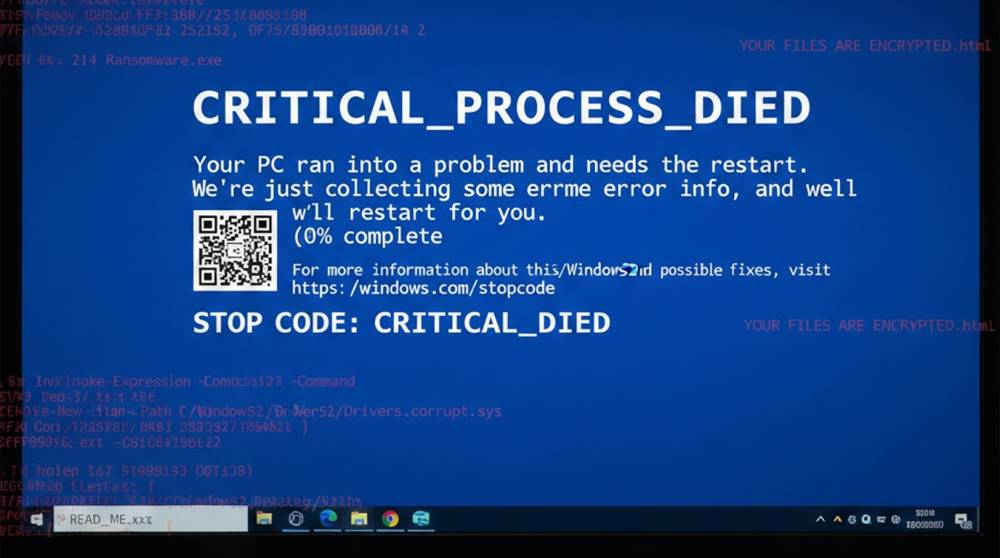
Malware sometimes deliberately triggers a Blue Screen of Death (BSOD) on Windows systems. It’s not a bug , it’s a tactic. The crash either hide...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
Malware sometimes deliberately triggers a Blue Screen of Death (BSOD) on Windows systems. It’s not a bug , it’s a tactic. The crash either hides what the malware just did, disrupts forensi...
Read Full ArticleMalware sometimes deliberately triggers a Blue Screen of Death (BSOD) on Windows systems. It’s not a bug , it’s a tactic. The crash either hide...
These three vulnerabilities are among the most common ways attackers break into web applications. They all happen through normal-looking HTTP GET or POST r...
The open-source webcam security software, MotionEye, is vulnerable to remote code execution, identified as CVE-2025-60787 (motionEye <= 0.43.1b4). Authe...
The defense industrial base (DIB), companies that design, build, and support military systems , remains one of the most intensely targeted sectors in globa...
In recent months, Cisco Talos has identified a new modular malware framework referred to as VoidLink. The framework was discovered to have been utilized an...
Google Postmaster Tools is a free dashboard provided by Google that lets email senders (companies, marketers, newsletter creators, anyone sending bulk mail...
Spam traps (sometimes called honeypot emails or spamtrap addresses) are email addresses that no real person ever owns, uses, or signs up with. They exist o...
Malware honeypots are decoy systems set up on purpose to look easy to hack. The idea is simple: make them seem like juicy targets (unpatched servers, open...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067