Claude Fable 5.2: Anthropic's Cyber Model Benchmarks
Anthropic released two models on Monday, and the benchmark that matters most is not the one about coding. Claude Fable 5.2 and Claude Mythos 5.2 both ship...
Found 11 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Anthropic released two models on Monday, and the benchmark that matters most is not the one about coding. Claude Fable 5.2 and Claude Mythos 5.2 both ship...
You build an image, you push it to a registry, you deploy it to production, and somewhere inside that image is a vulnerable package nobody noticed, sitting...
You have 40,000 new vulnerabilities reported in a single year. Your security team can realistically patch maybe 5% of them. The rest will sit there, unpatc...
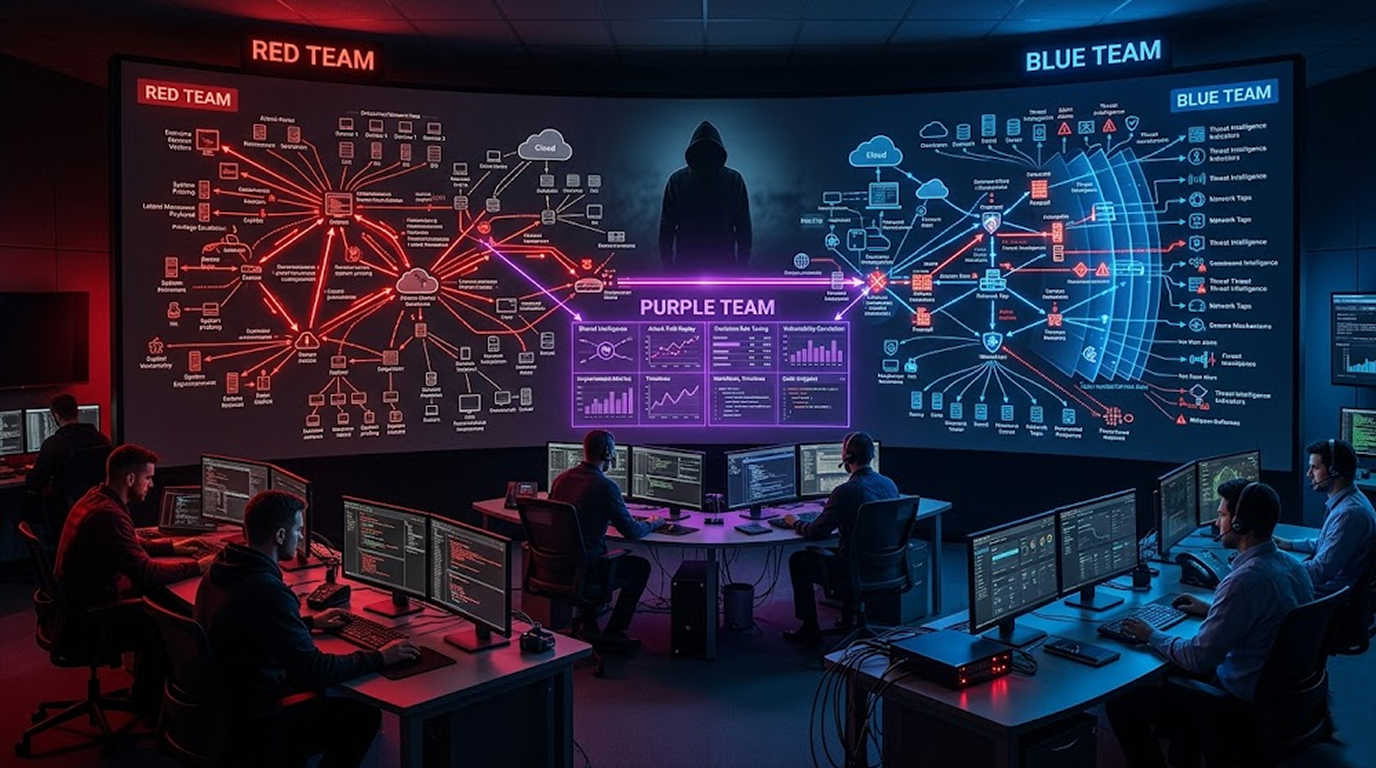
You have heard the terms thrown around at security conferences and in vendor pitches. Red team finds vulnerabilities. Blue team defends. Purple team does b...
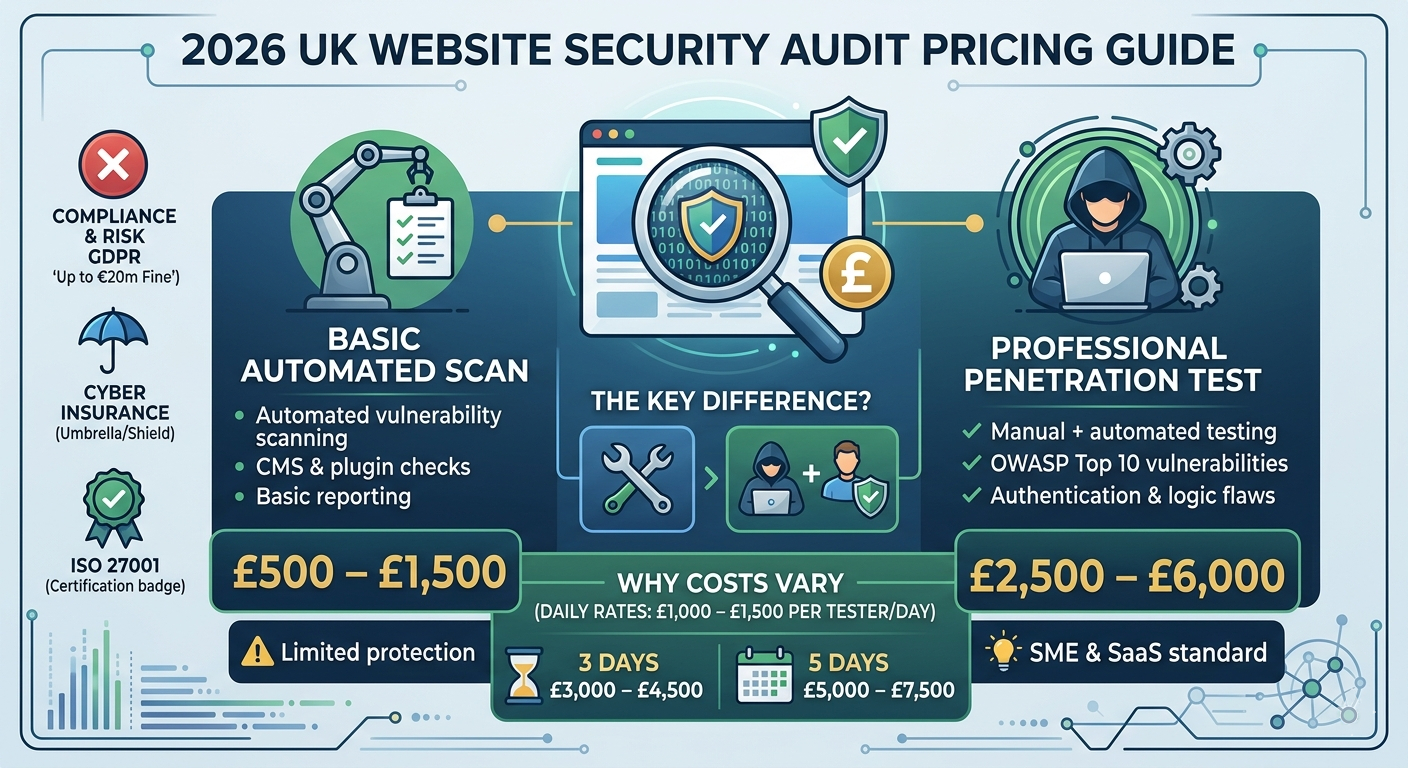
If you're researching website security audit cost in the UK, you’ve probably noticed something confusing: Some providers charge £500… o...
Running a vulnerability scanner often gives you a long list of findings. Many are low-priority noise, but a few high/critical issues appear again and again...
Many companies still treat penetration testing as a yearly checkbox.Schedule the test, get the report, fix the findings, move on.The problem is simple: att...
Zero-day vulnerabilities are flaws in software or hardware unknown to the vendor or developers. Hackers exploit these gaps before they’re patched, ma...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067