Find Undocumented API Endpoints in 5 Minutes
Undocumented (or “hidden”) API endpoints often called shadow APIs represent one of the biggest risks in modern web applications. These endpoint...
Found 199 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Undocumented (or “hidden”) API endpoints often called shadow APIs represent one of the biggest risks in modern web applications. These endpoint...
Many people assume their private chats on messaging apps like WhatsApp, Signal, or Telegram stay visible only on their own devices. However, a common and e...
While many website owners place importance on website content, how the content appears to visitors., the hidden data is the one of the most important parts...
Your website is down. Customer data is leaking. Orders have stopped. Google has flagged your site as unsafe. For thousands of small-to-medium businesses an...
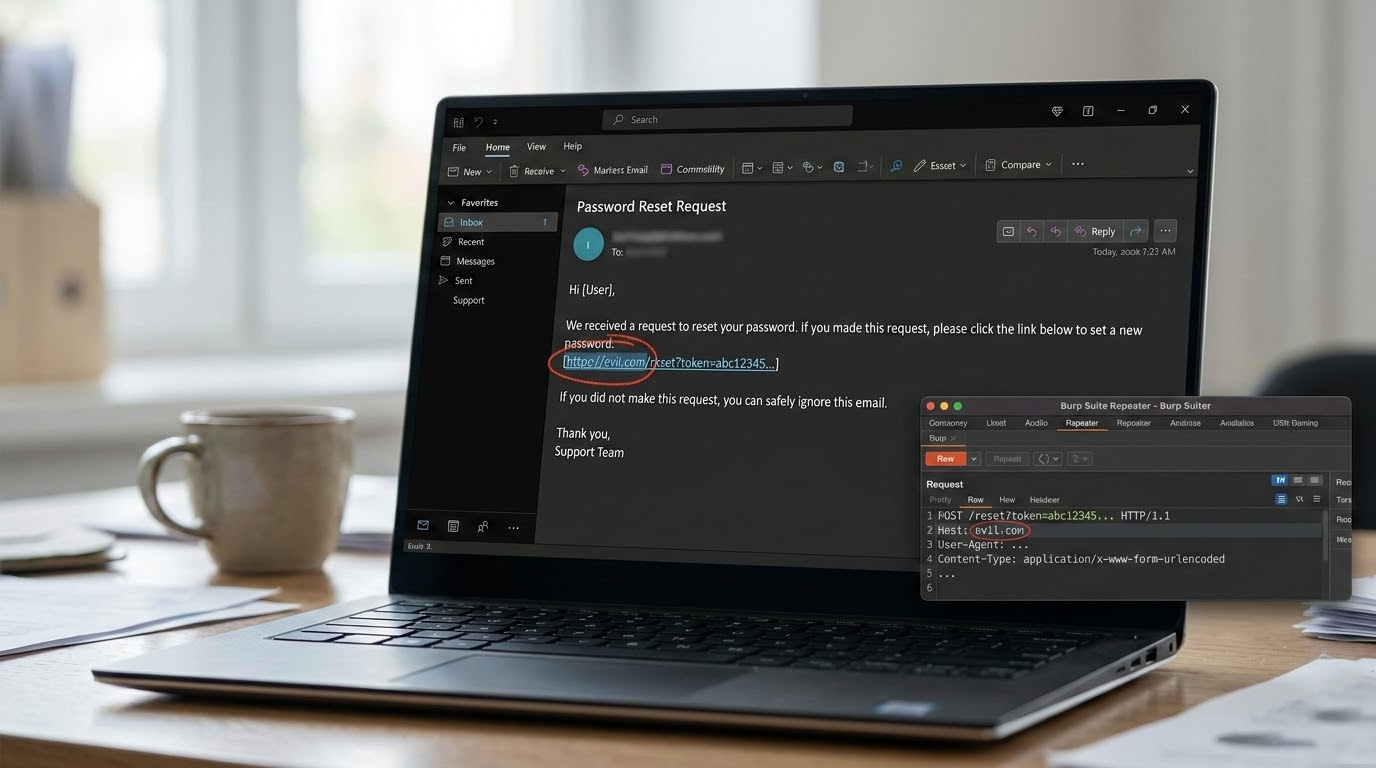
Password reset poisoning (also called Host header poisoning in reset flows) is one of those “old but gold” vulnerabilities that refuses to die....
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a recently disclosed vulnerability in Soliton Systems FileZen , a file transfer solu...
The open-source webcam security software, MotionEye, is vulnerable to remote code execution, identified as CVE-2025-60787 (motionEye <= 0.43.1b4). Authe...
Versions of Docker Desktop before 4.44.3 (released on 20 August 2025) had a serious vulnerability that could enable an attacker to use Linux containers to...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067