How a Mobile App API Caused a Silent Data Leak
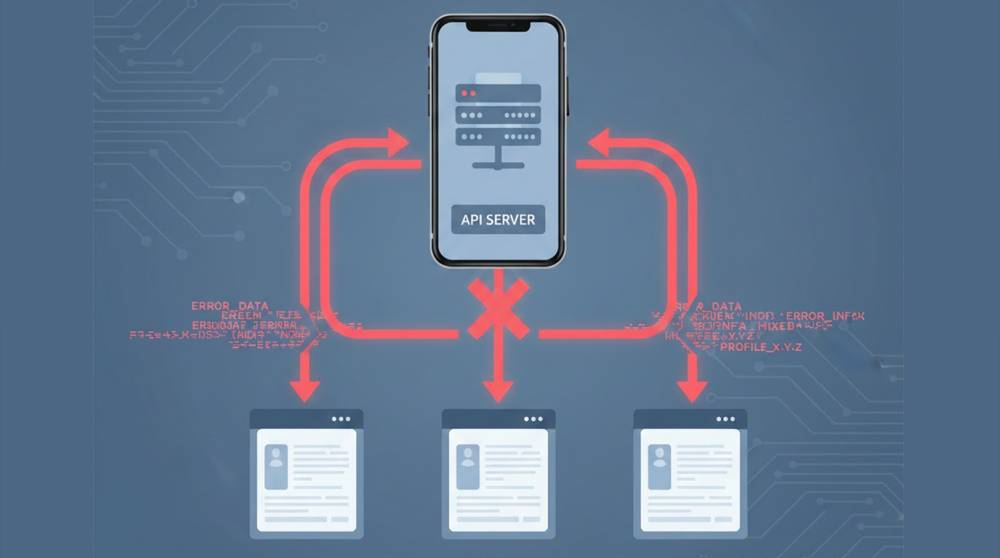
The mobile app wasn’t hacked.The API was trusted too much.That trust exposed user data—quietly, consistently, and at scale.This is one of the m...
Found 562 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The mobile app wasn’t hacked.The API was trusted too much.That trust exposed user data—quietly, consistently, and at scale.This is one of the m...
Think of your smartphone as a central hub for all of your electronic communication and transactions; where the banking app, emails, photographs, work-relat...
A newly disclosed security flaw in SmarterTools SmarterMail is already being exploited in the wild, just two days after a patch was released, raising conce...
Many traditional red team exercises are ineffective for a single reason: they focus on testing types of attack instead of the detection effectiveness. ...
Modern mobile apps are mostly UI.The real logic lives in:1. APIs2. Backend services3. Third party integrationsAttackers rarely attack the app itself.They a...
As of January 19, 2026, LastPass has begun notifying customers of an increasing number of phishing emails targeting their customers. As part of this attack...
There is a substantive security vulnerability within RPi-Jukebox-RFID (version 2.8.0). RPi-Jukebox-RFID is an open-source media jukebox system designed for...
Siklu EtherHaul EH 8010 and EH 1200 wireless backhaul devices have been identified to have a critical vulnerability allowing remote command execution witho...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067