GitHub Breach Traced to Poisoned Nx Console Extension
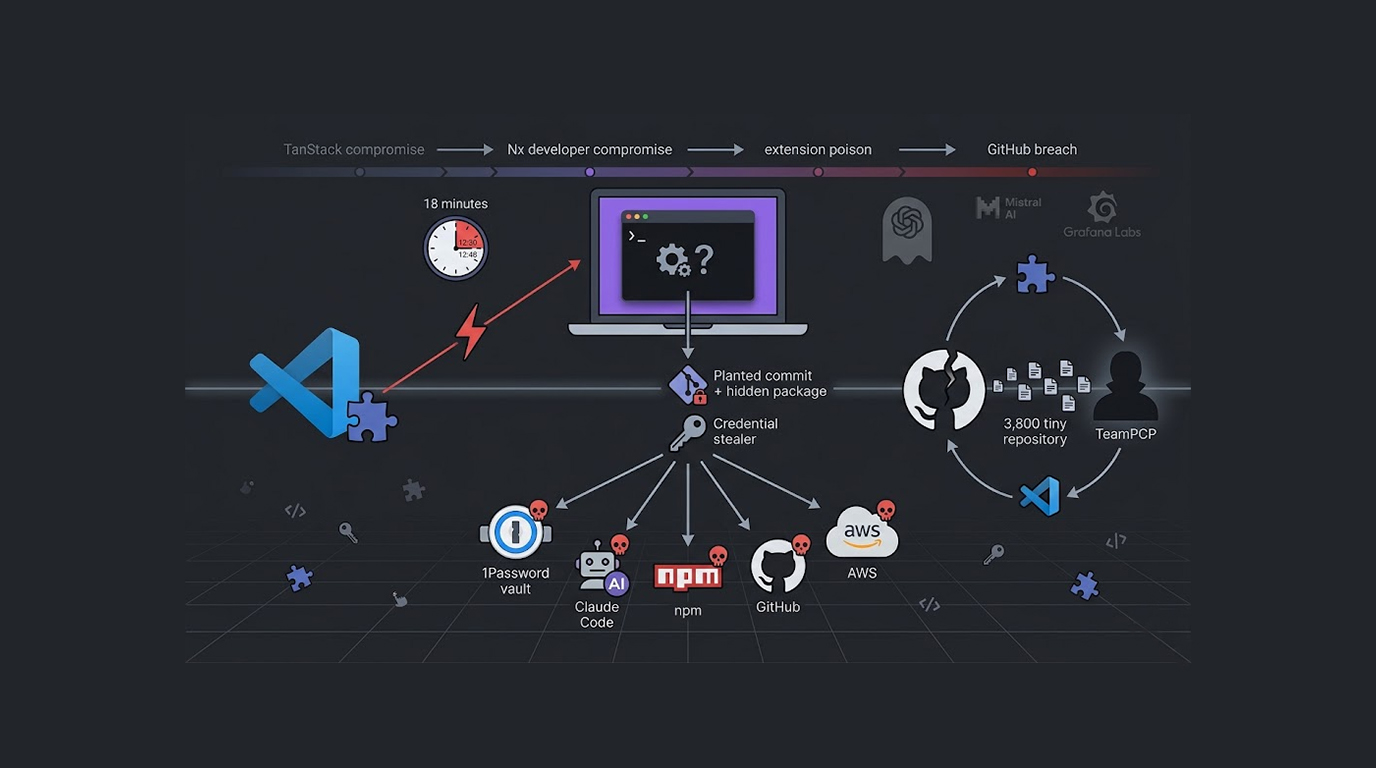
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
Found 59 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
GitHub has officially confirmed that the breach of its internal repositories was the result of a compromised employee device, and the attack vector was a p...
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
A video game platform used by ethnic Koreans living along China's border with North Korea has been compromised. The attackers? A North Korean state-sponsor...
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
You sit down at your computer. You need to edit a configuration file. You open Notepad++. It has been on your machine for years. Lightweight. Fast. Trustwo...
Vercel has revealed they were exposed to a security breach which enabled unauthorised access to company internal systems because of an employee's Google Wo...
A lot of people think that their phones' cameras only turn on when they use the camera app. However, malicious apps can activate either the front or back c...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067