Arista VeloCloud Vulnerability Under Active Exploitation
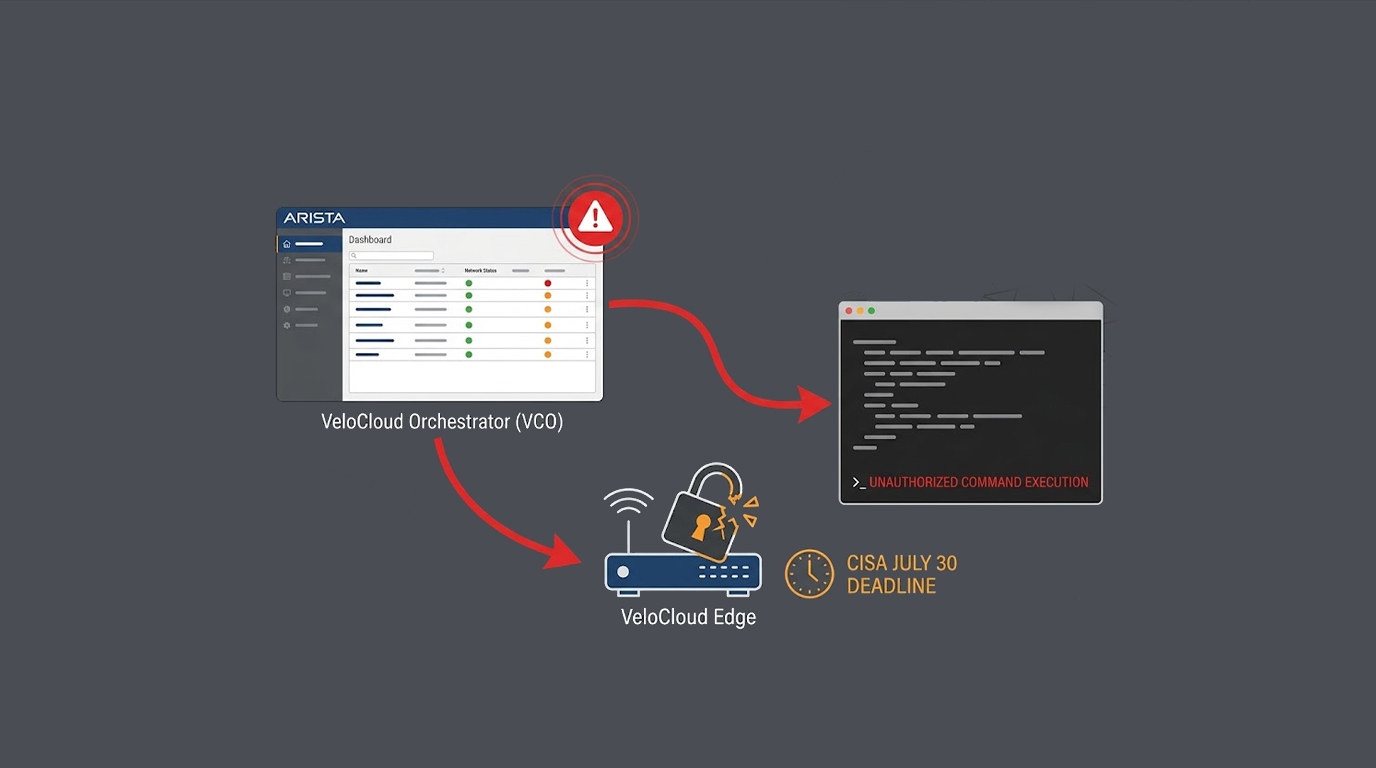
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
Found 41 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
If you are running an on-premises version of Arista VeloCloud Orchestrator, you need to stop what you are doing and check your systems right now. A maximum...
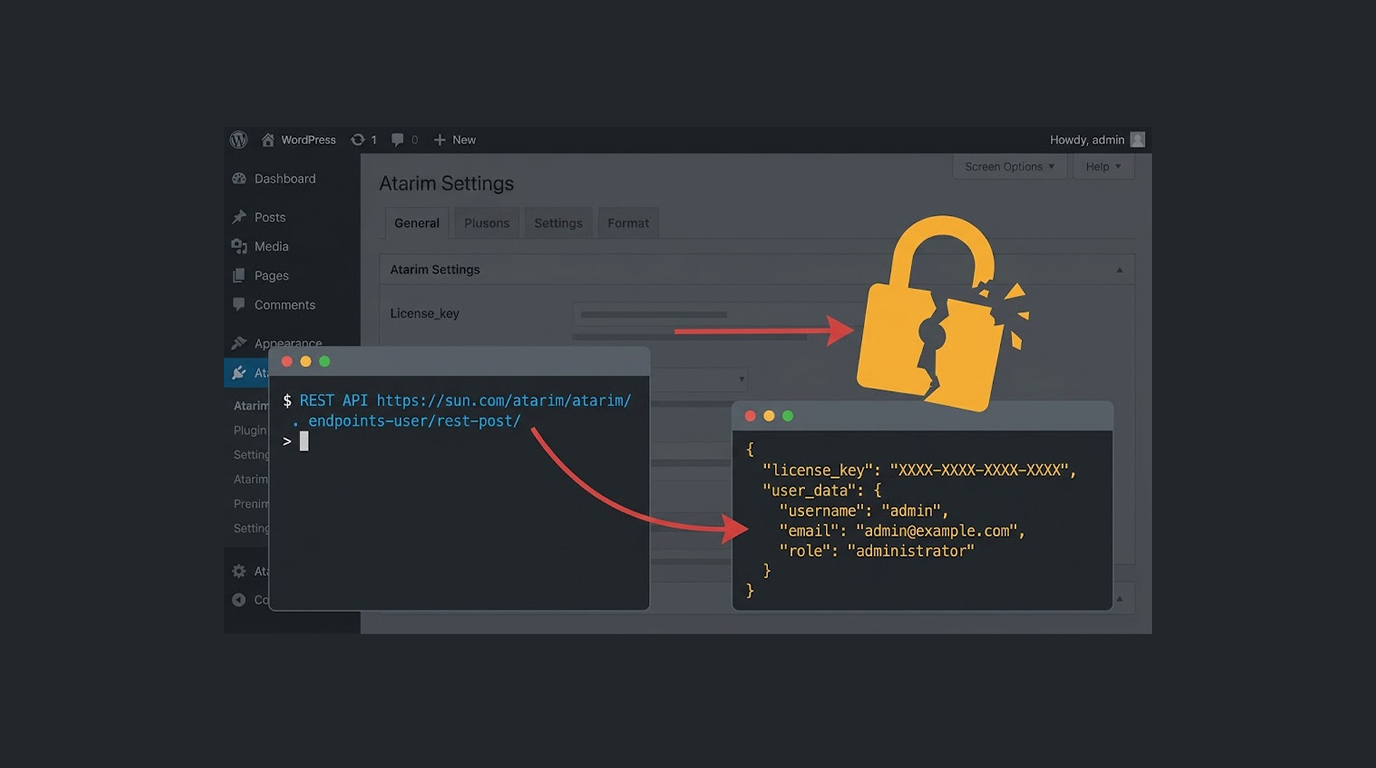
There exists a security vulnerability in the Atarim plug-in which exposes attackers to steal sensitive data without going through any kind of authenticatio...
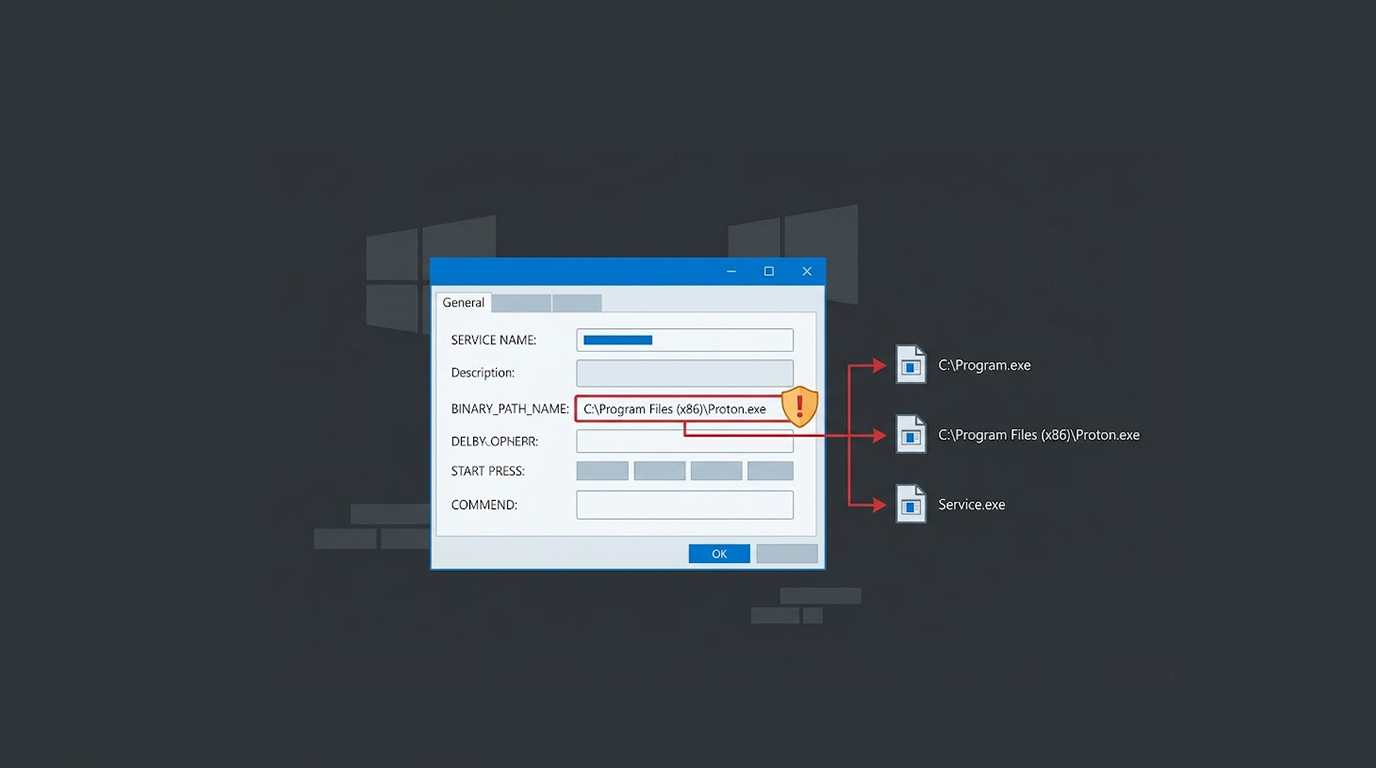
A security vulnerability in ProtonVPN version 4.4.1 could allow a local user to escalate their privileges to the highest level available on the system. The...
The U.S. Cybersecurity and Infrastructure Security Agency just added a new vulnerability to its Known Exploited Vulnerabilities catalog. Federal agencies n...
You have antivirus software. You have a firewall. You have been running the same security setup for years without any major problems.But are you actually s...
Here's a scenario you don't want to face. A receptionist with basic login privileges, someone who only schedules appointments, clicks a link they shouldn't...
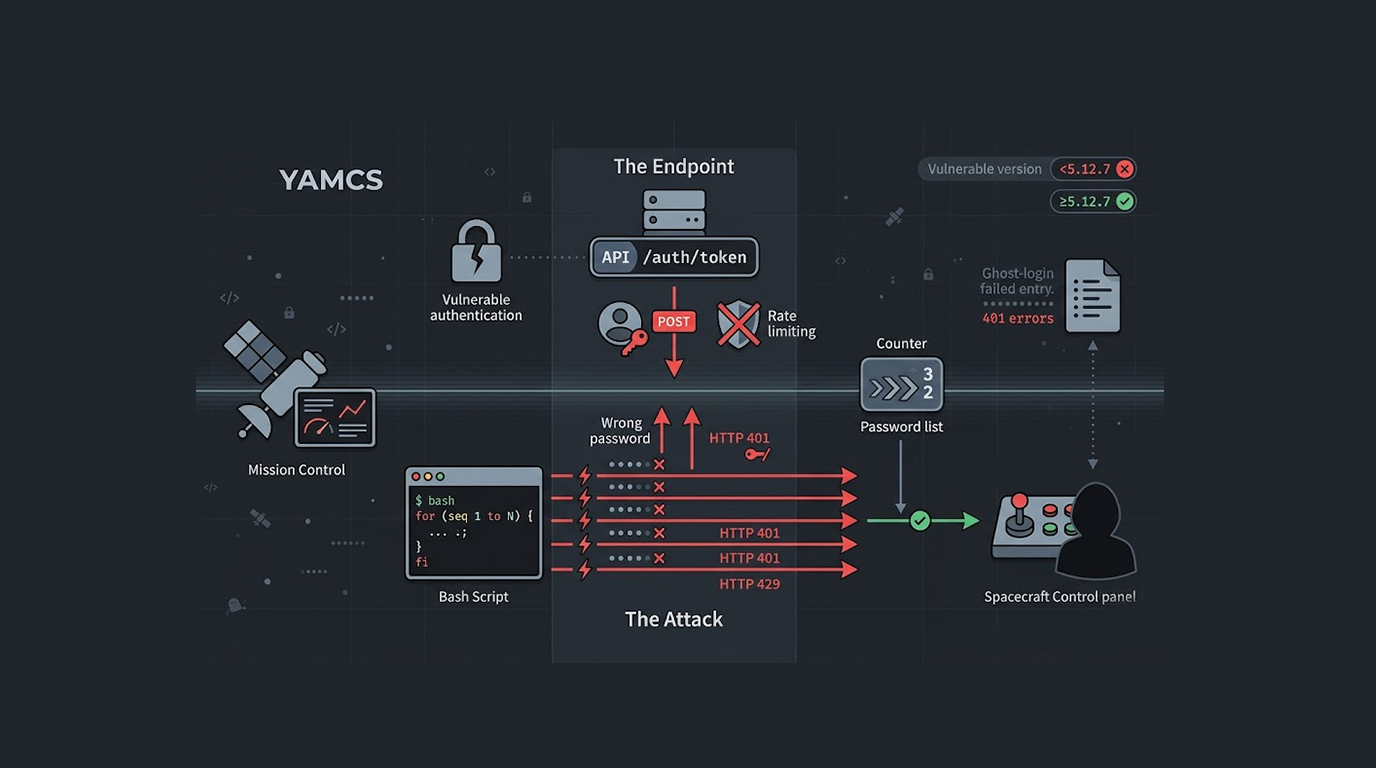
YAMCS contains an exploitable security vulnerability that allows endless brute-force attempts to log into the user accounts, meaning there is no limit on t...
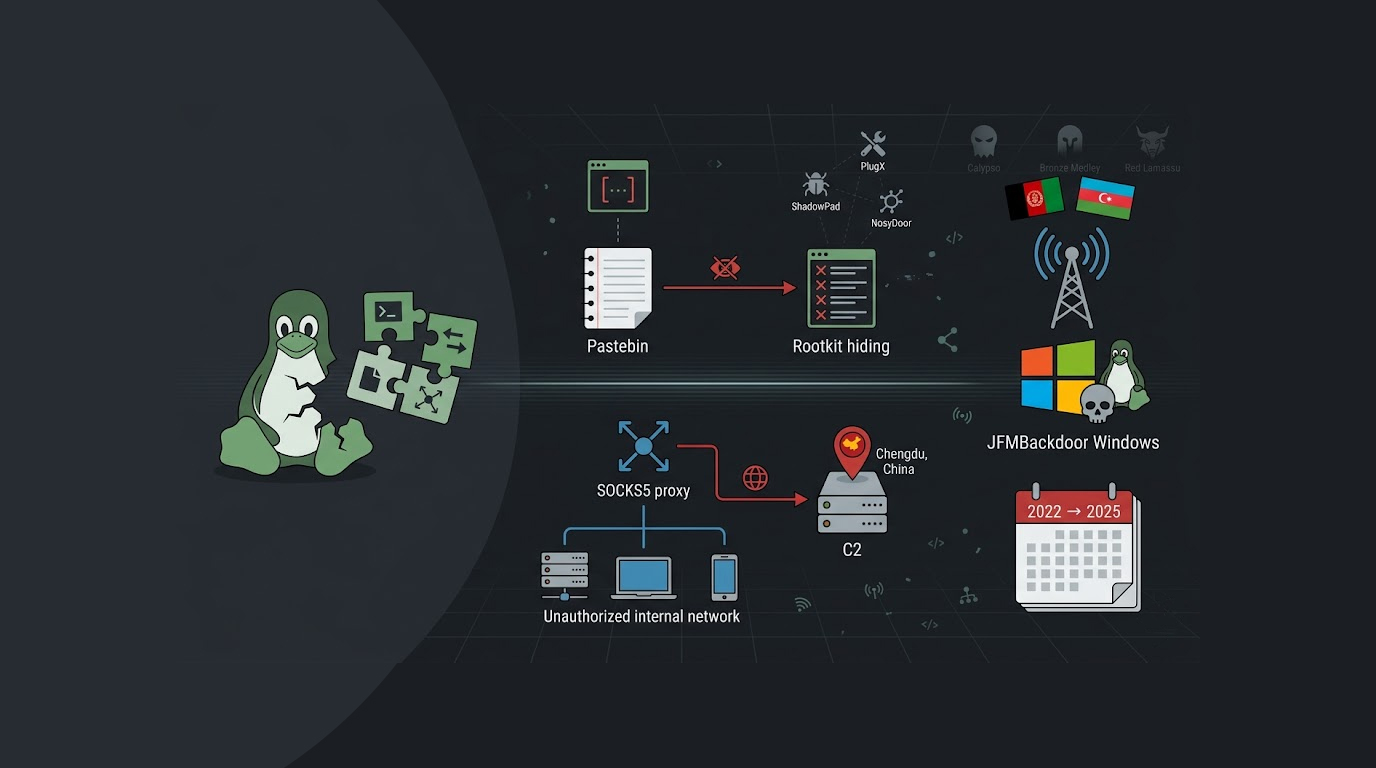
Showboat malware targets MT companies in the Middle East. It looks like was created by someone linked to Chinese-sponsored organizations and has been utili...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067