Double Extortion Ransomware Explained
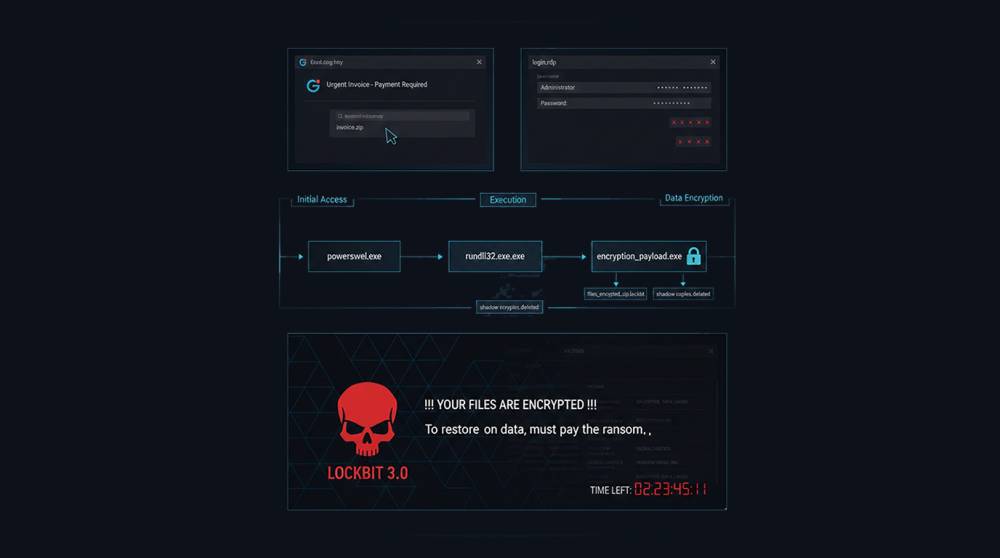
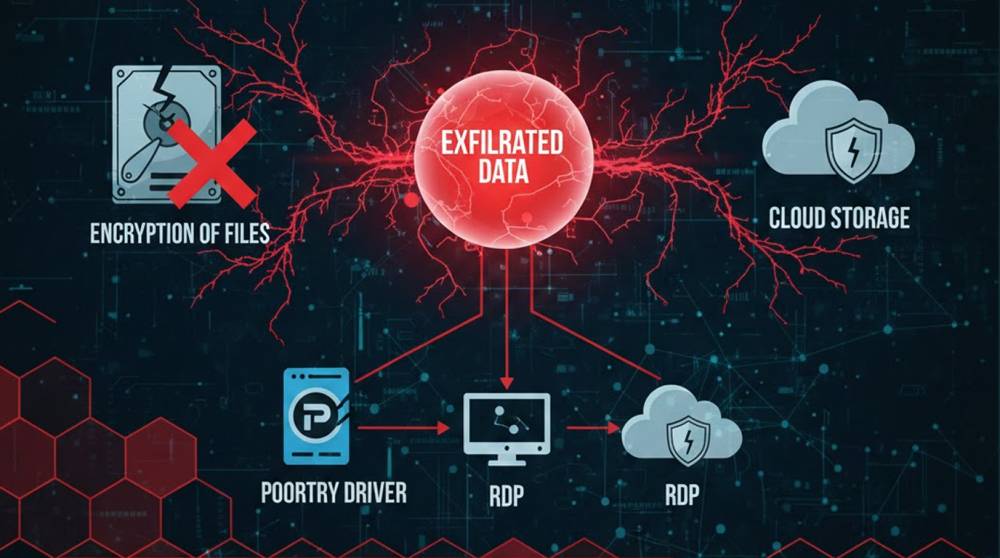
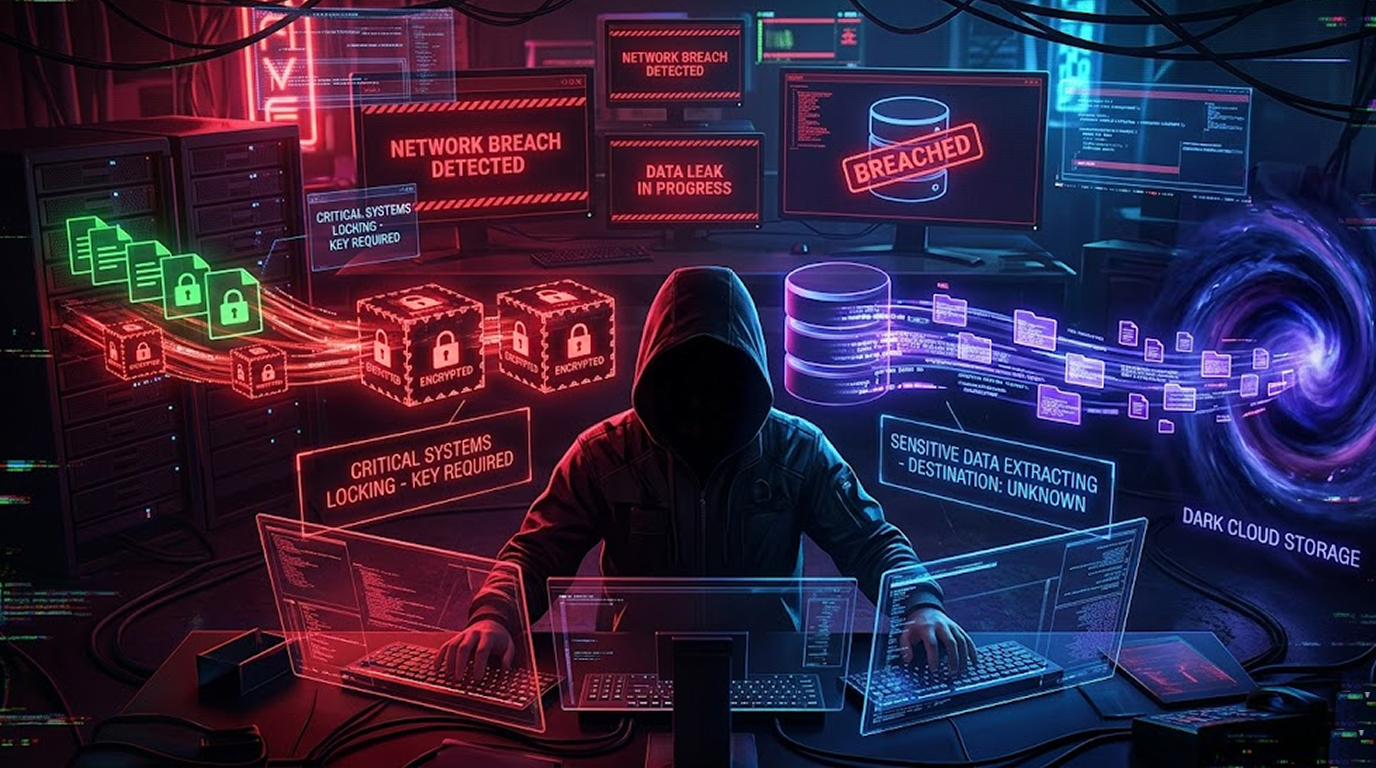
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
Found 22 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
The term "Garage APTs" (Advanced Persistent Threats/small teams) in cyber security defines entities that are small, but now can implement APT level operati...
The latest version of ransomware known as Osiris has been reported by Security research firm Crowdstrike after a Southeast Asia-based operator of multiple...
The U.S. Cybersecurity and Infrastructure Security Agency has added a long-standing OpenPLC ScadaBR vulnerability to its Known Exploited Vulnerabilities ca...
Ransomware used to be pretty straightforward: a hacker encrypts your files, demands a ransom, and you either pay or lose access. Simple, if terrifying. Bu...
Ransomware has become one of the most dangerous cyber threats, targeting businesses, hospitals, governments, and even individuals. These attacks involve ma...
Cybersecurity researchers have identified a new ransomware strain named Ymir, deployed in a recent cyberattack only two days after the targeted system was...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067