npm Malicious Packages Deploy Windows RAT Malware
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
Found 25 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
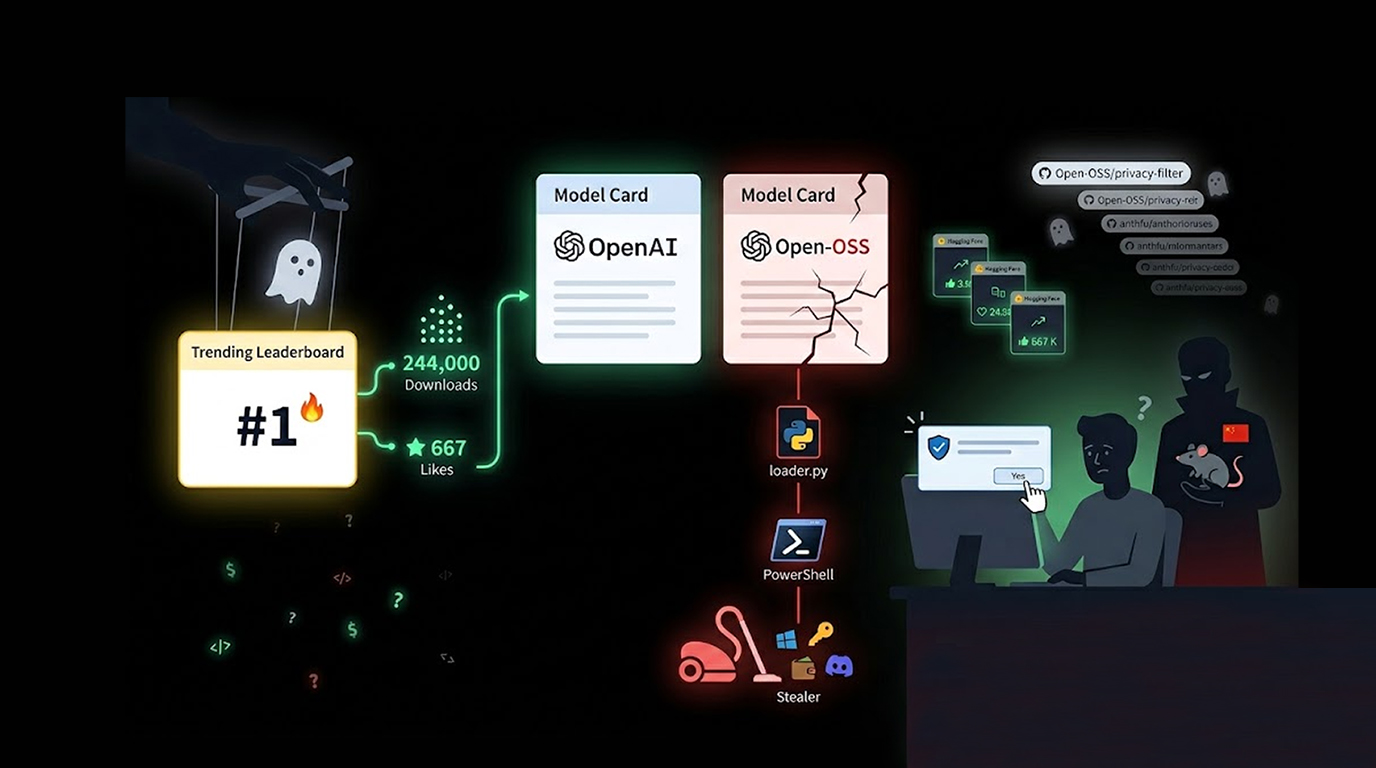
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
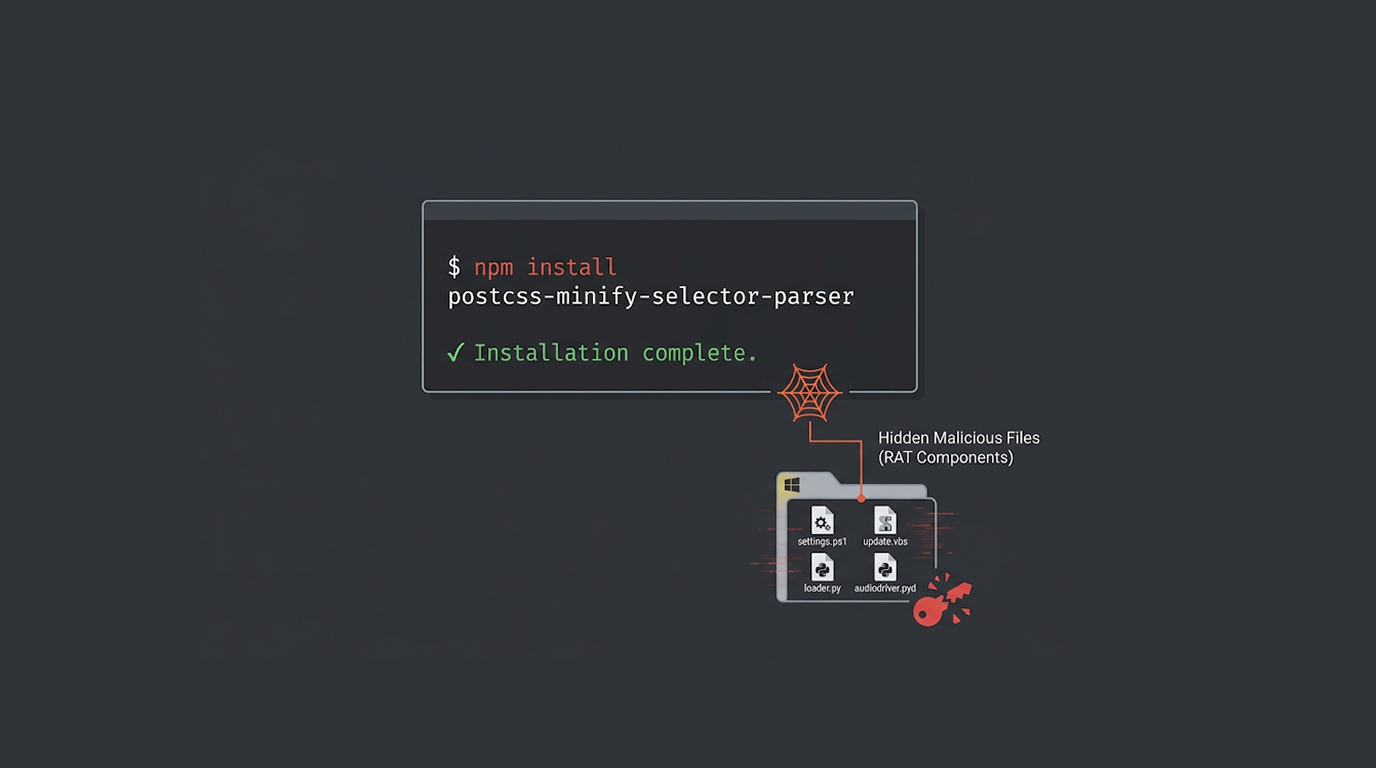
You run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically...
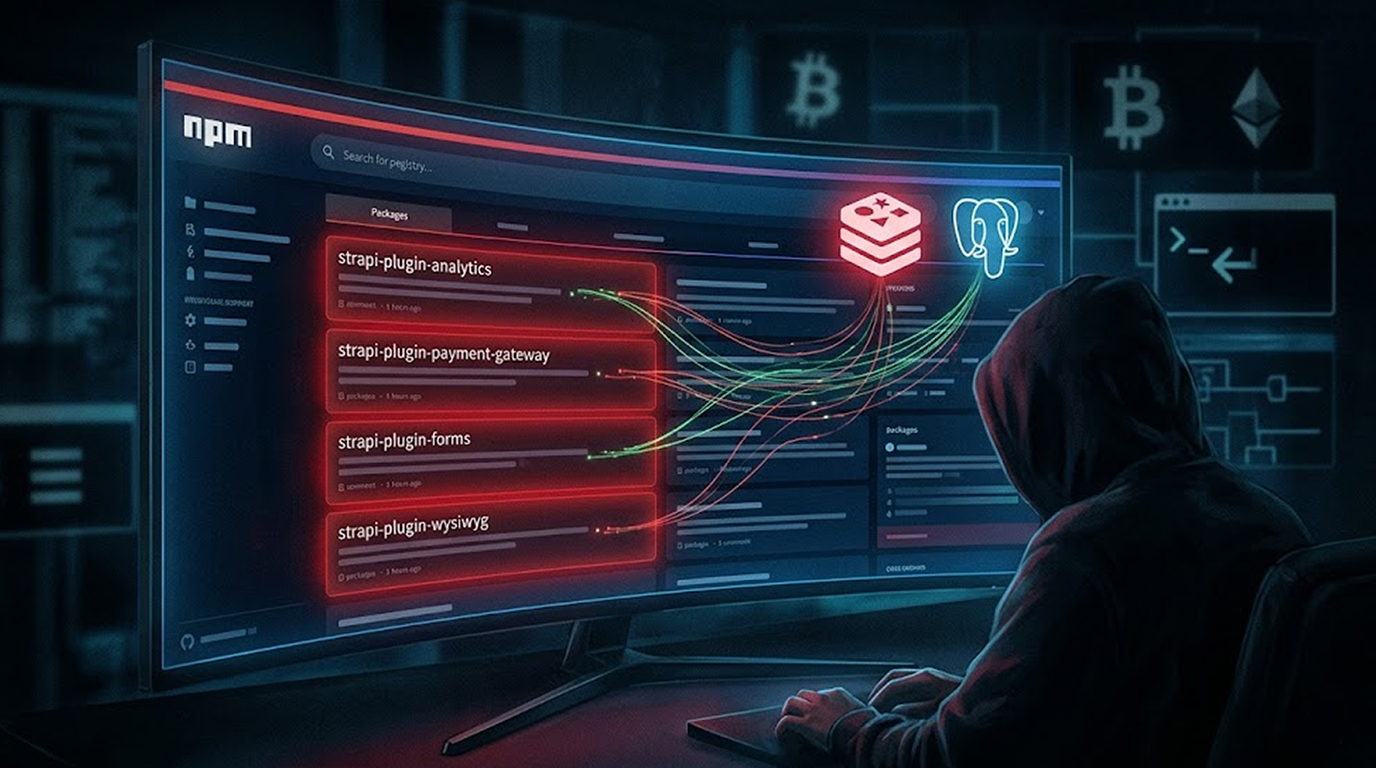
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
North Korean-linked hackers are running a slick, persistent operation that turns the job hunt into a security nightmare for developers. They have created p...
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
On February 17, 2026, at 3:26 AM PT, an unauthorized actor used a compromised npm publish token to release version 2.3.0 of the popular AI-powered coding a...
Cybersecurity researchers have identified three malicious npm packages that were distributing a previously undocumented remote access trojan (RAT) now know...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067