How Attackers Discover and Exploit Shared Credentials in Cloud Environments
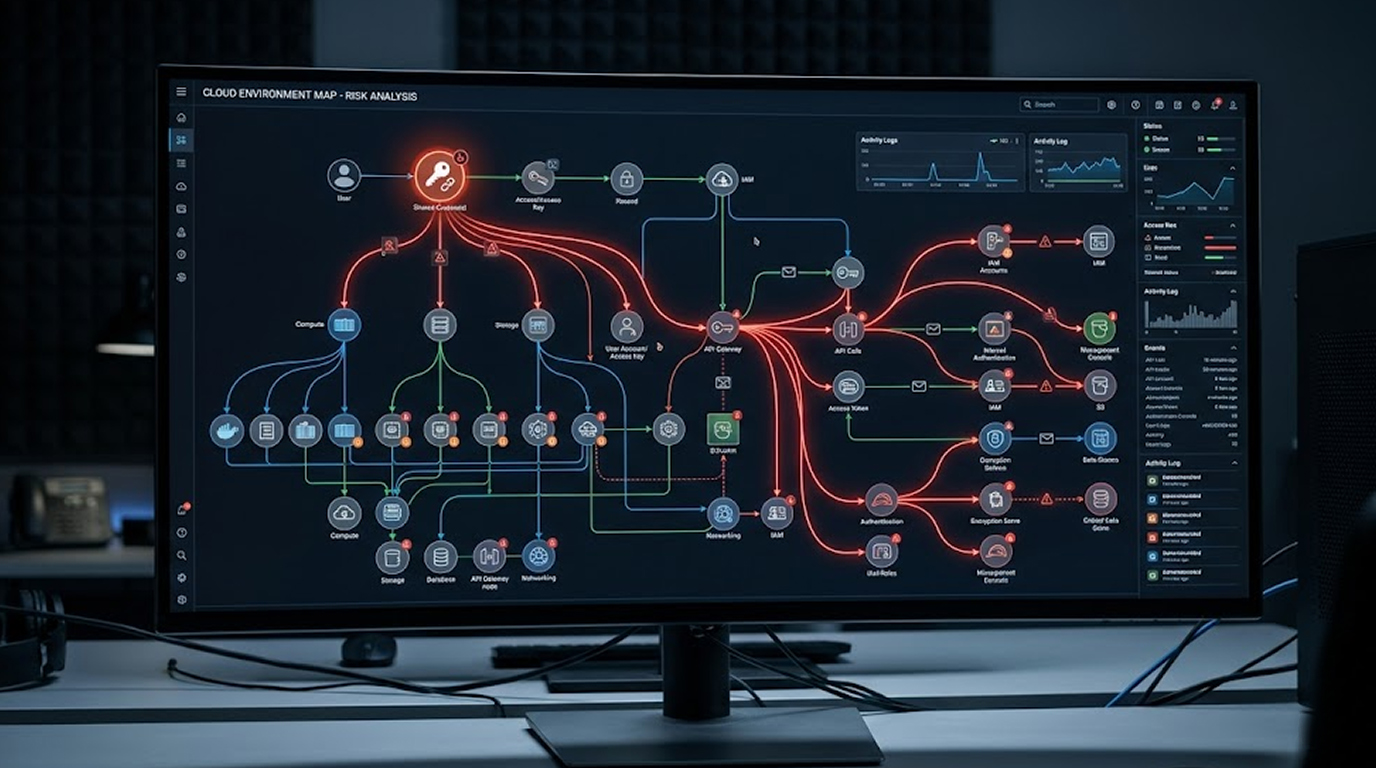
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
Found 23 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
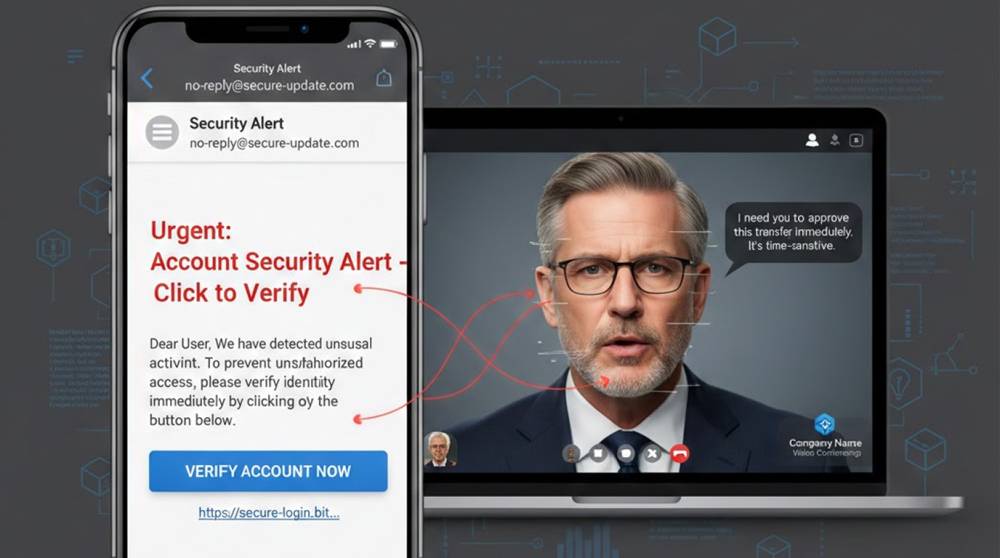
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
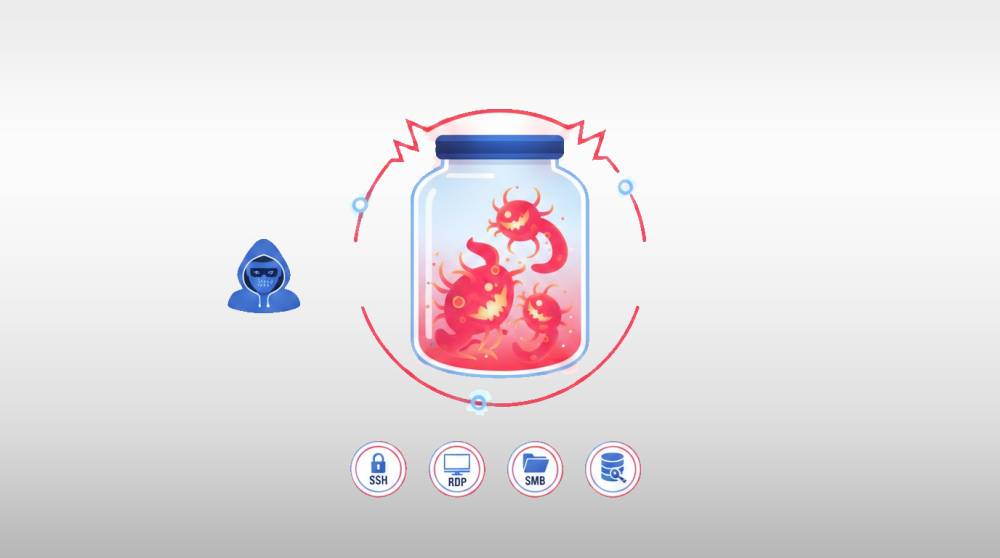
Malware honeypots are decoy systems set up on purpose to look easy to hack. The idea is simple: make them seem like juicy targets (unpatched servers, open...
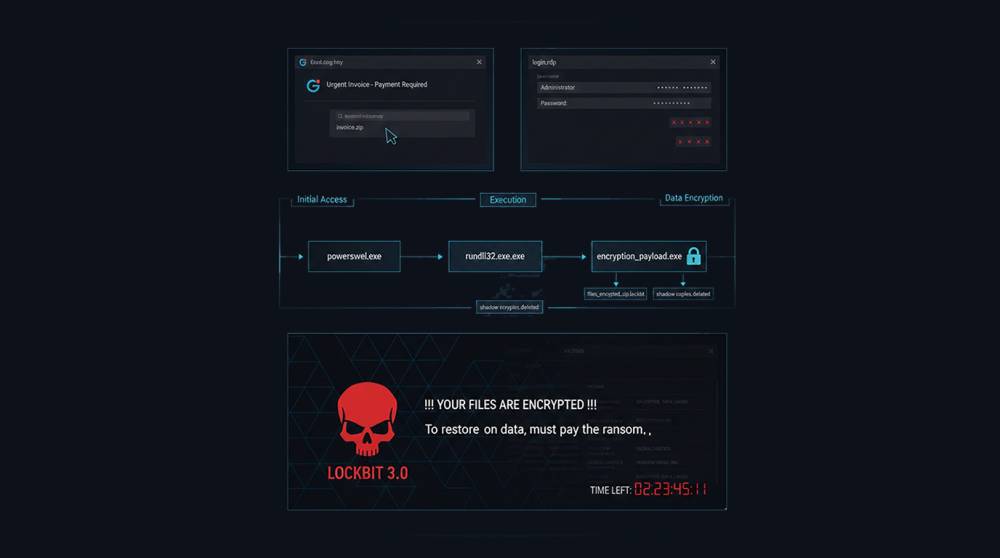
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
For executives and board members, credentials of a company are not only an IT issue; credential security is also a governance and risk management priority....
MalwareBazaar is a free public malware sharing and intelligence platform hosted by abuse.ch (the organization running URLhaus, Feodo Tracker and SSL Blackl...
The Microsoft Defender team has issued an explicit alert that, for many years, malware has been a threat to Windows computer users; however, starting in la...
Olevba is a powerful, free tool specifically designed to analyze Microsoft Office documents (Word, Excel, PowerPoint) for malicious VBA macros and other em...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067