Cereal Espionage Toolset: Stealing Email From Exchange
Most breaches you read about are loud in the way that matters to defenders, because they involve ransomware, a leak site, a demand, and a countdown, and th...
Found 562 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Most breaches you read about are loud in the way that matters to defenders, because they involve ransomware, a leak site, a demand, and a countdown, and th...
Nine hours. That is how long it took from CVE publication to the first exploitation attempt. The vulnerability is CVE-2026-123158, and it now has a name:...
A 5.5 medium-severity vulnerability just landed in CISA's Known Exploited Vulnerabilities catalog, and the reason is a lesson every security team should in...
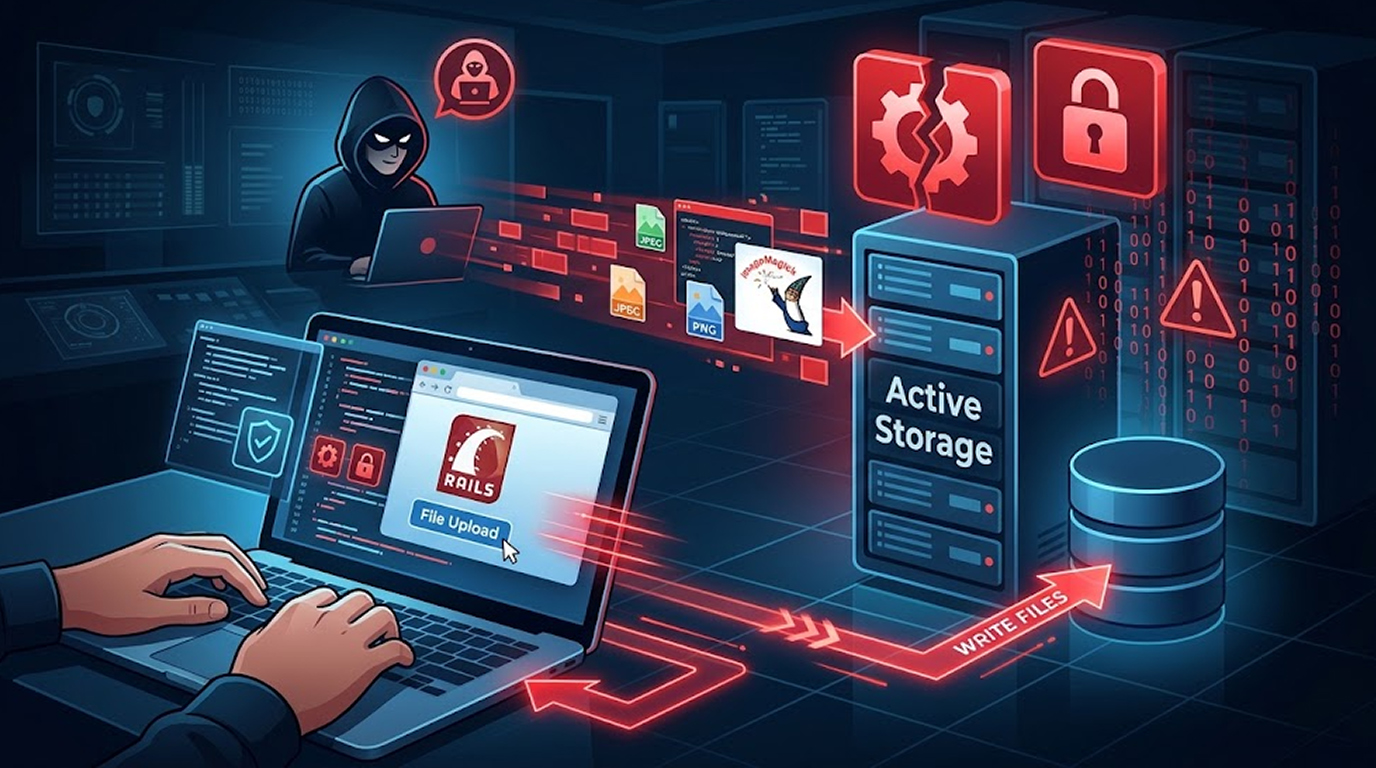
A single file upload is enough. No authentication, no variant generation, no preview call, no explicit analyze invocation. Just attach the file and the fla...
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
VulnCheck has confirmed what every industrial security team was dreading. A maximum-severity vulnerability in Siemens SIMATIC IoT2050 Advanced devices is n...
The mental image most people carry of state-sponsored espionage is a team of elite operators, custom zero-days, and infrastructure that costs more than a s...
If you've read a headline claiming that roughly half of AI-generated code fails security testing, the number itself is less interesting than what it descri...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067