If you're running PaperCut NG or MF, you need to update again. The company just released new maintenance releases that replace all the emergency patches they pushed out earlier. And this time, the updates have gone through full quality assurance testing.
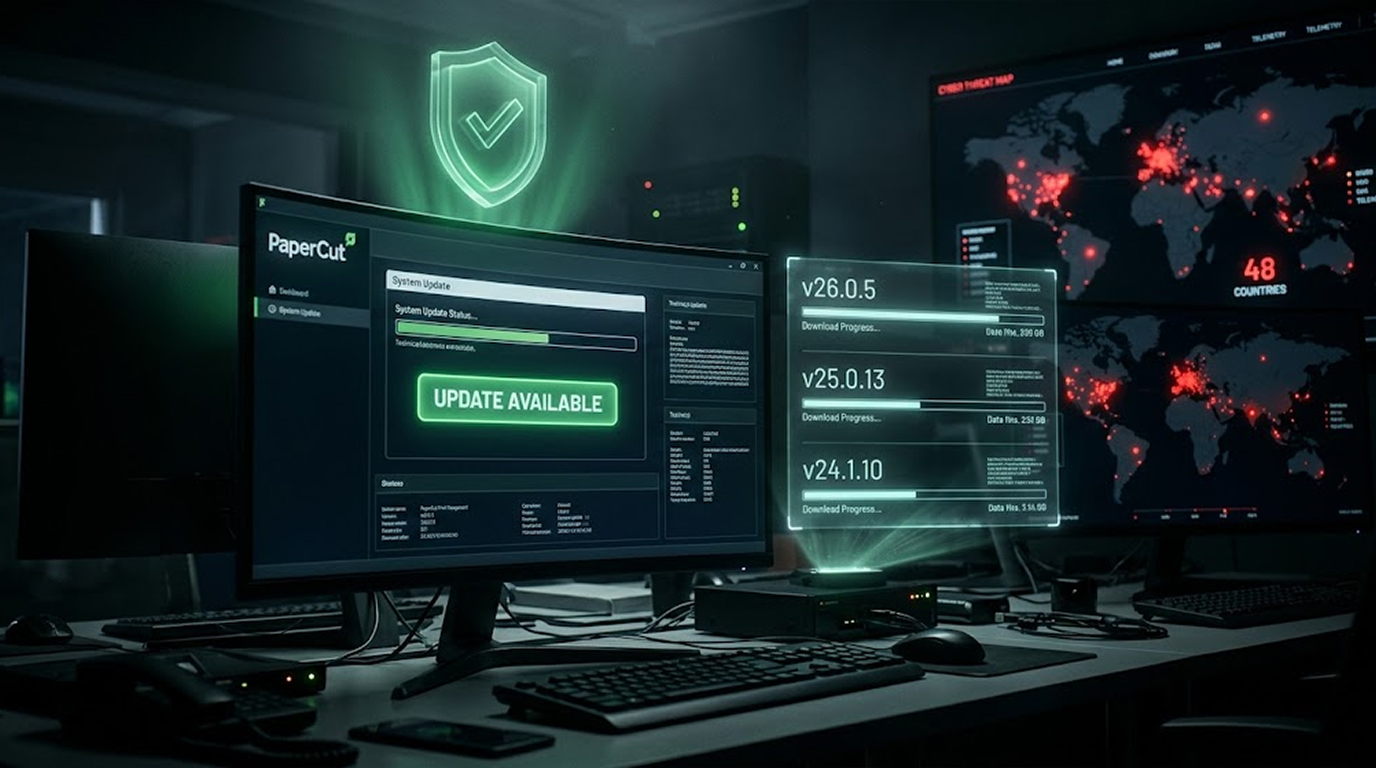
PaperCut announced the new releases on Thursday. Versions 26.0.5, 25.0.13, and 24.1.10 are now available. The Hacker News covered the announcement.
Here's what you need to know.
Quick Summary
|
What |
Details |
|
New Releases |
26.0.5, 25.0.13, 24.1.10 |
|
Replaces |
Emergency Patch Releases 1, 2, and 3 |
|
Vulnerabilities |
CVE-2026-81578, CVE-2026-82078 |
|
Status |
Active exploitation |
|
Campaign Scale |
395 organizations, 48 countries |
|
Attacker IP |
45.142.193[.]132 |
What's in the New Release?
PaperCut says these are "Regular Maintenance Releases" that have gone through complete QA testing. They contain all the security fixes from the emergency patches, plus additional security hardening.
What They Replace:
- Emergency Patch Release 1
- Emergency Patch Release 2
- Emergency Patch Release 3
- Two regressions from those patches
- Various hardening and mitigations against potential attack chains
The emergency patches were released quickly to address the immediate threat. But they weren't fully tested. The new maintenance releases are.
Why This Matters:
If you applied an emergency patch, you should move to a maintenance release. PaperCut says customers running an emergency patch build should upgrade.
The Vulnerabilities
The two flaws are CVE-2026-81578 and CVE-2026-82078. Together, they allow an attacker to bypass authentication and execute arbitrary code on vulnerable PaperCut instances.
The Impact:
An attacker who exploits these flaws can:
- Bypass authentication
- Execute code remotely
- Gain full control of the PaperCut server
- Move laterally into the network
These aren't theoretical vulnerabilities. They're being actively exploited in the wild.
The Active Exploitation Campaign
The Hacker News reported on a campaign that's been using these flaws to break into organizations at scale. GreyNoise and Blackpoint Cyber tracked the activity.
The Numbers:
|
Metric |
Number |
|
Compromised instances |
440 |
|
Victim organizations |
395 |
|
Countries affected |
48 |
|
Primary target |
U.S. education sector |
The Attacker:
A suspected Russian-speaking threat actor. The action comes from the IP address 45.142.193[.]132.
Connection between AI and the Attack:
What makes the mentioned attack unique is that the hundreds of AI agents, which were controlled via the OpenAI Codex harness and DeepSeek model, participated in the process.
The attacker also tried to avoid targeting entities in Russia, China, Hong Kong, Thailand, Iran, and 23 other countries. But GreyNoise noted that the "attempted restraint failed in some instances."
What We Don't Know:
"It is unclear if this actor is solely focused on access development to be handed off to other affiliated actors or if they will directly leverage their accesses to achieve follow-on objectives such as data theft or ransomware deployment," GreyNoise said.
What You Should Do
1. Update to the Latest Maintenance Release
- PaperCut NG/MF 26.0.5
- PaperCut NG/MF 25.0.13
- PaperCut NG/MF 24.1.10
If you're running an emergency patch build, move to one of these maintenance releases.
2. Indicators of Compromise
Look for the following:
- Unusual outbound connections
- Unusual registry changes
- Unusual process creation
- Unusual admin accounts
3. Assess Your Vulnerability
Is your PaperCut server Internet-exposed? Do you need to be? Make sure that only authorized networks can access the server.
4. Identify Indicators of AI-enabled Behavior
Signs that indicate attempts to exploit vulnerabilities using automation include:
- Retry attacks
- System enumeration
- Multi-system attacks
The Bottom Line
PaperCut has released new maintenance updates that replace the emergency patches for CVE-2026-81578 and CVE-2026-82078. These releases have gone through full QA testing and include additional hardening. Active exploitation continues, so if you haven't updated yet, do it now.
What You Need to Know:
|
Key Point |
Detail |
|
New Releases |
26.0.5, 25.0.13, 24.1.10 |
|
Replaces |
Emergency Patch Releases 1, 2, 3 |
|
Vulnerabilities |
CVE-2026-81578, CVE-2026-82078 |
|
Status |
Active exploitation |
|
Campaign Scale |
395 organizations, 48 countries |
What You Need to Do:
- Update to the latest maintenance release
- Check for indicators of compromise
- Review your exposure
- Monitor for AI-assisted activity
FAQ Section
What is the new PaperCut release?
PaperCut released maintenance versions 26.0.5, 25.0.13, and 24.1.10. These replace the emergency patches for CVE-2026-81578 and CVE-2026-82078 and include additional security hardening.
Why did PaperCut release updates?
Emergency patching was done to fix a problem that is being exploited. New maintenance patches have been tested and resolve the regression in emergency patches.
Which vulnerabilities does the update patch?
CVE-2026-81578 and CVE-2026-82078 allow authentication bypass and remote code execution.
Are these vulnerabilities being exploited?
Yes. A suspected Russian-speaking actor has compromised at least 395 organizations in 48 countries.
What should I do if I applied an emergency patch?
Upgrade to one of the new maintenance releases. PaperCut says customers running emergency patch builds should move to a maintenance release.