Monitoring Gap: Why Runtime Detection Misses Attacks
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
Found 16 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
Qilin is not just another ransomware group. It is the most operationally active ransomware operation on the planet. And it has figured out how to use artif...
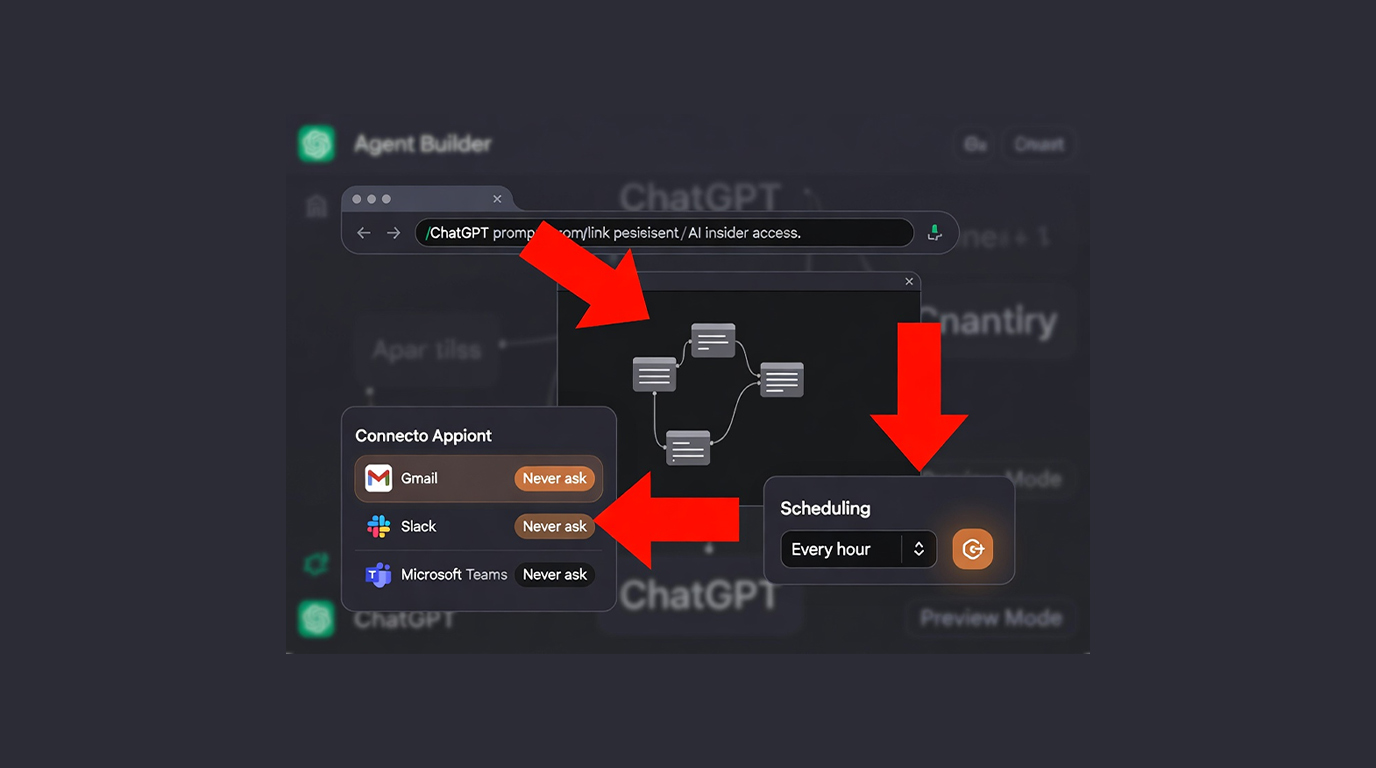
What if, for example, one of your staff members clicks on an apparently safe link, only to have an autonomous AI agent start operating within your company...
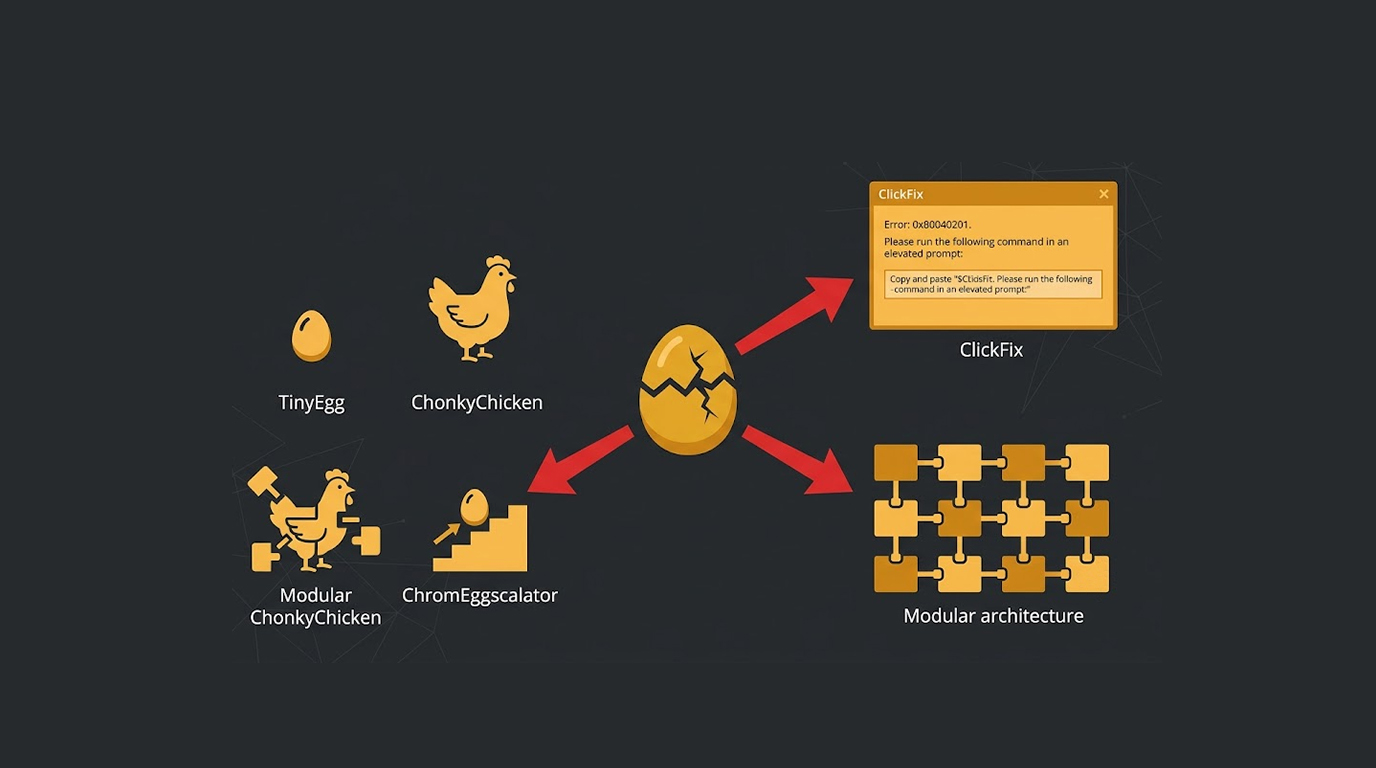
You would think that getting caught in the spotlight would make a cybercriminal group pack up and disappear. But with the Golden Chickens malware-as-a-serv...
Traditional antivirus looks for known signatures. It has a list of bad files and checks every file against that list. If the malware is new, the antivirus...
You do not have time for a 20-page threat intelligence report. You have a board meeting in an hour. Your SOC is flagging anomalies. And there is a new thre...
ZionSiphon malware is a specialized Operational Technology (OT) malware designed to sabotage water treatment and desalination facilities According to a rep...
PHANTOMPULSE RAT is a newly developed and highly advanced Remote Access Trojan (RAT) that is getting a lot of attention within the cybersecurity community...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067