WordPress Core RCE: Urgent 7.1.4 Patch
WordPress site owners are under active attack right now, because threat actors have been observed attempting to exploit a high-severity security flaw in Wo...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
WordPress site owners are under active attack right now, because threat actors have been observed attempting to exploit a high-severity security flaw in Wo...
Two critical WordPress plugin vulnerabilities are making the rounds. One is being actively exploited right now. The other is a pair of flaws that could let...
Security researcher just dropped a working exploit for a vulnerability in ProFTPD. It's a post-auth SQL injection that leads to remote code execution. Basi...
A critical unauthenticated remote code execution vulnerability in the JCE extension for Joomla has been exploited. A public proof-of-concept is now availab...
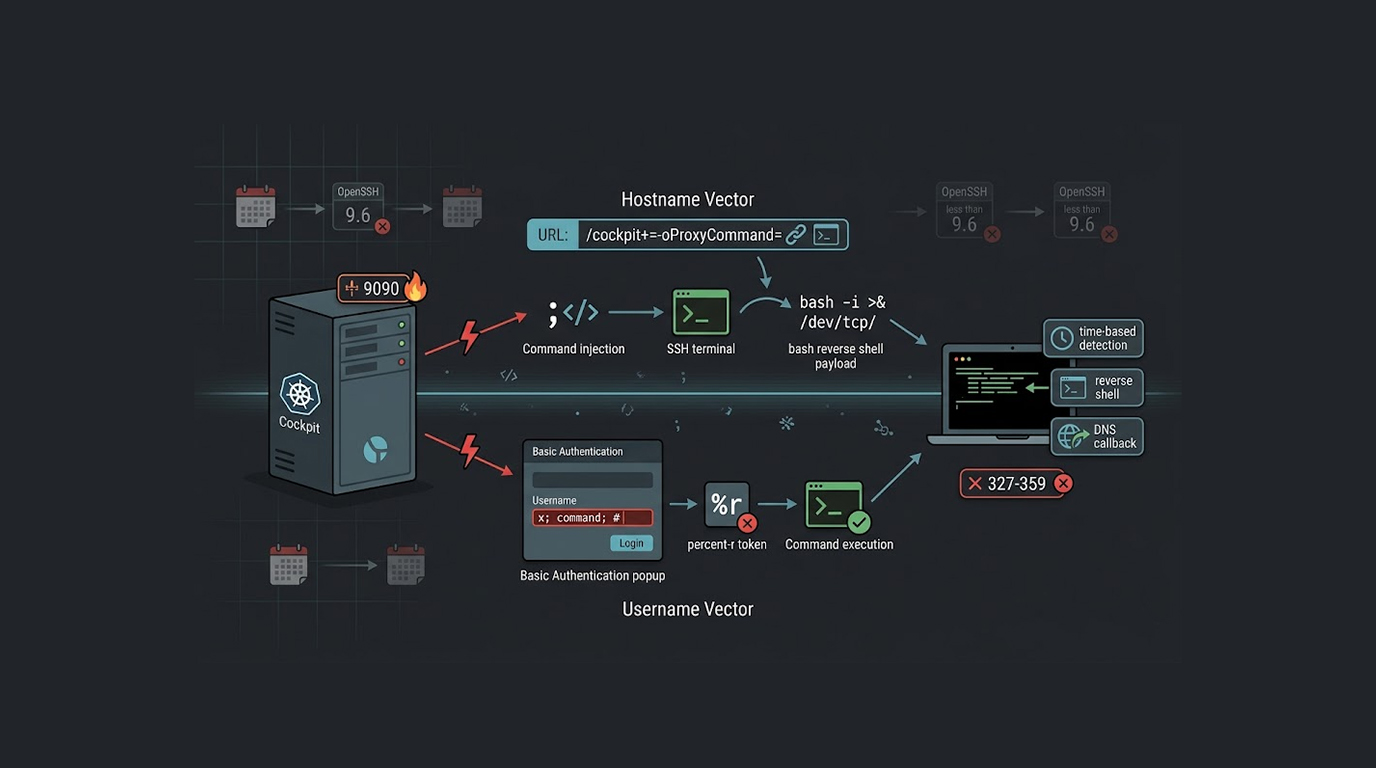
A security flaw in Cockpit allows an attacker to run arbitrary code on the server without authenticating first. The problem manifests itself through Cockpi...
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
Flare, a cybersecurity company, announced a new type of large-scale initiative -- the PCPcat campaign -- which is a worm-like cyberattack that will exploit...
A bug called React2Shell (CVE-2025-55182) showed up, and it’s the kind of issue that makes security people stare at logs like they’re trying to...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067