AI-Generated PHP That Calls unserialize(): The Unsafe Pattern
You ask an AI assistant for a quick PHP snippet, it needs to store some session data, or cache an object, or pass a configuration array between requests, t...
Found 7 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You ask an AI assistant for a quick PHP snippet, it needs to store some session data, or cache an object, or pass a configuration array between requests, t...
Two critical WordPress plugin vulnerabilities are making the rounds. One is being actively exploited right now. The other is a pair of flaws that could let...
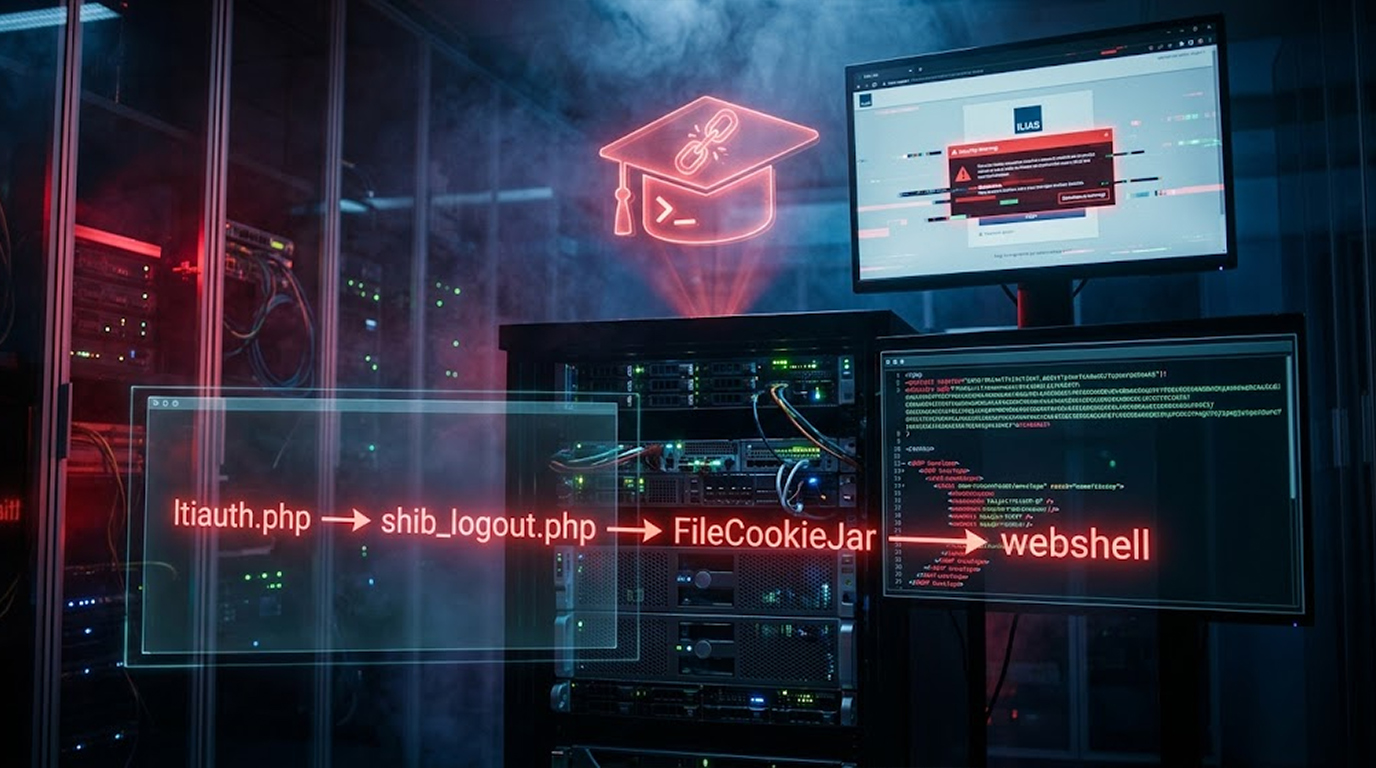
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
If you run a WordPress site, you need to read this. Five critical security holes were just found in some really popular plugins and themes. We're talking a...
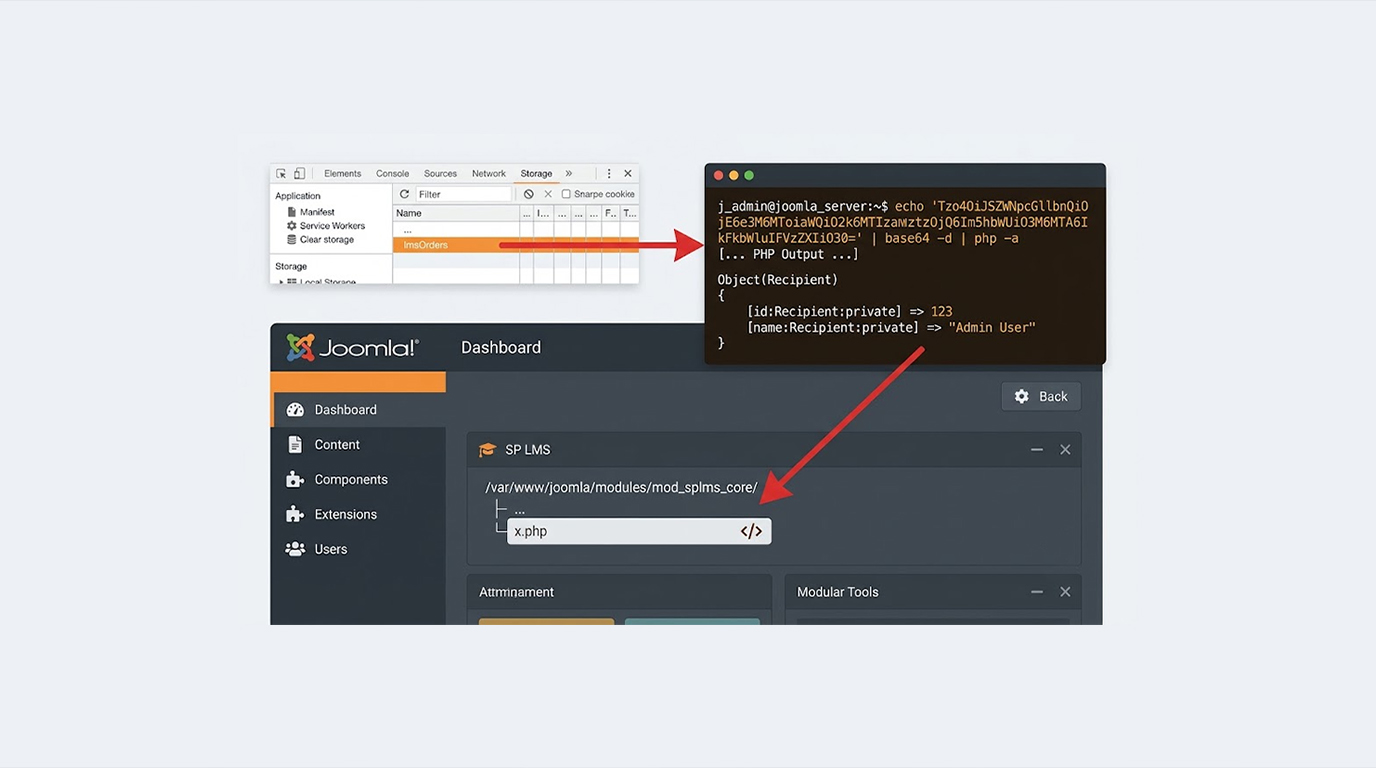
Joomla extension JoomShaper SP LMS contains an object injection vulnerability leading to remote code execution for the attacker. This vulnerability is iden...
A high-severity security flaw has been revealed in the LiteSpeed Cache plugin for WordPress, exposing users to the risk of unauthorized access and potentia...
A maximum-severity security flaw has been disclosed in the WordPress GiveWP donation and fundraising plugin that exposes more than 100,000 websites to remo...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067