AI-Generated DOM XSS: When the Payload Targets Client-Side Logic
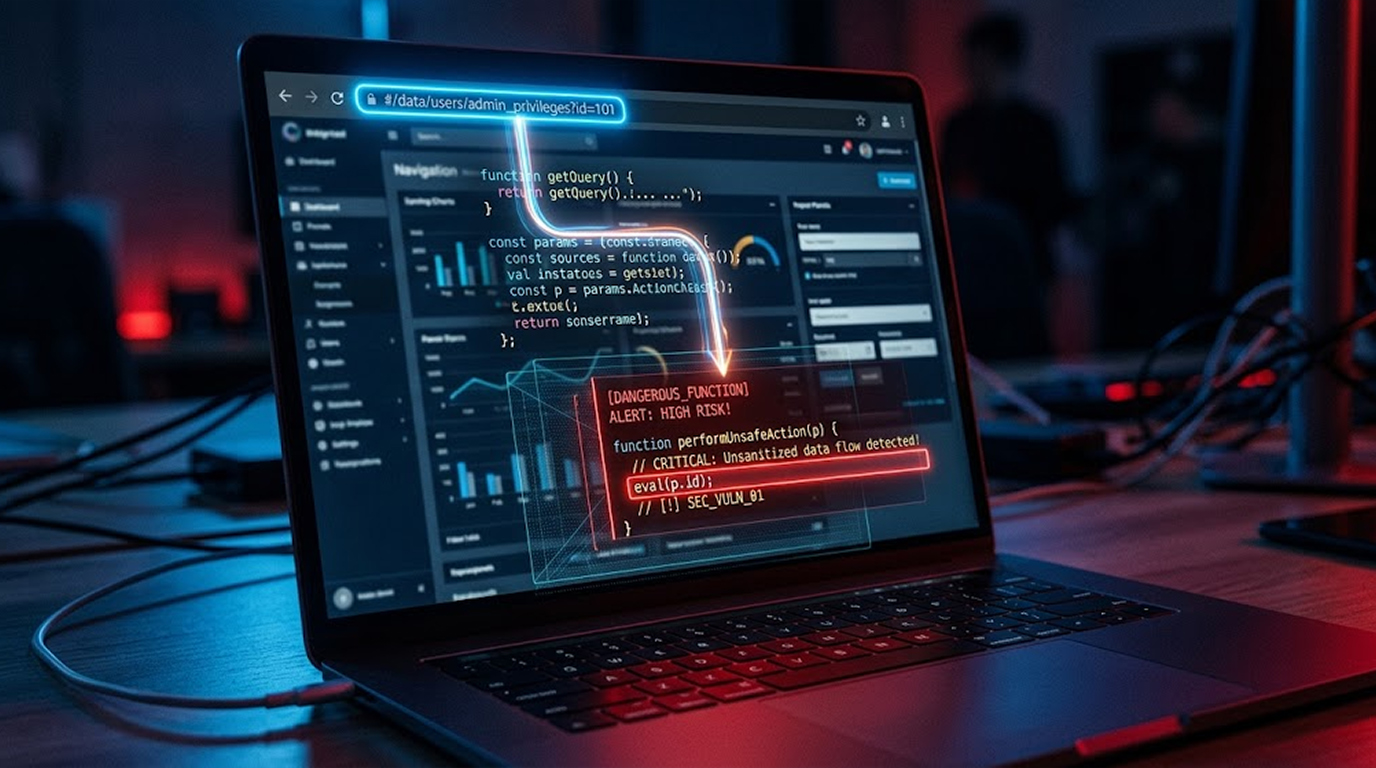
You have a Content Security Policy that blocks inline scripts, you have a web application firewall that catches known XSS patterns, and you have input vali...
Found 3 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have a Content Security Policy that blocks inline scripts, you have a web application firewall that catches known XSS patterns, and you have input vali...
Most teams already run scanners.Many still miss XSS.That’s because XSS is rarely a simple input problem.It’s a data-flow and context problem.Re...
XSStrike is an open-source toolkit focused on cross-site scripting (XSS) discovery. It blends a smart payload generator, context awareness, and filtering/W...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067