Dell RecoverPoint Zero-Day Exploited by China APT UNC6201
According to a joint report by the Google Mandiant and Google Threat Intelligence Group, a suspected China-related threat cluster identified as "UNC6201" h...
Found 152 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
According to a joint report by the Google Mandiant and Google Threat Intelligence Group, a suspected China-related threat cluster identified as "UNC6201" h...
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
The SMB (Server Message Block) is a popular protocol used by ransomware gangs to move between computers in networked environments like Windows. Port 445 is...
The open-source webcam security software, MotionEye, is vulnerable to remote code execution, identified as CVE-2025-60787 (motionEye <= 0.43.1b4). Authe...
In recent months, Cisco Talos has identified a new modular malware framework referred to as VoidLink. The framework was discovered to have been utilized an...
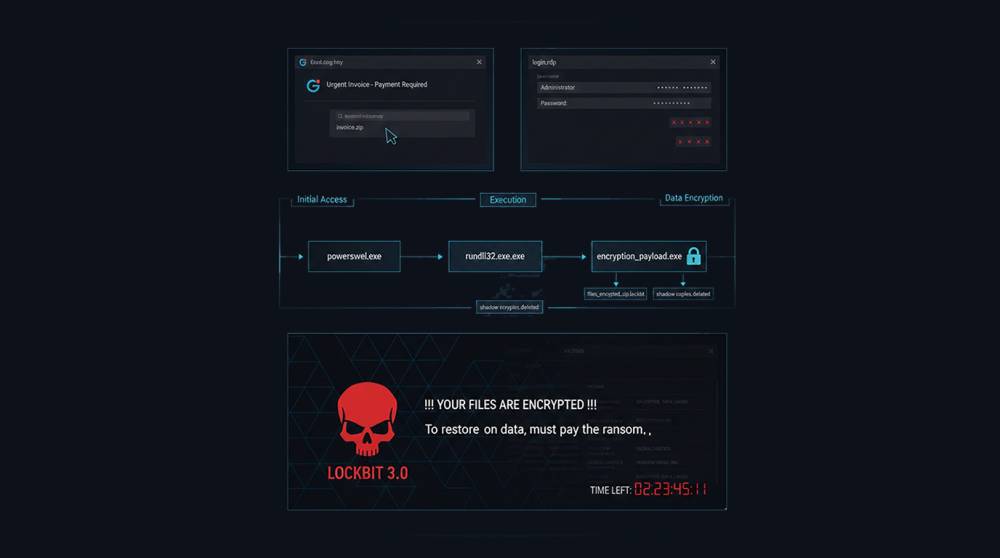
LockBit is (or was) the most active and profitable ransomware-as-a-service (RaaS) operation in recent years. The group provides the LockBit ransomware buil...
AccessEnum is one of those Sysinternals tools that quietly does a ton of work with almost no effort. It's free, tiny (under 150 KB), doesn't need to be ins...
CVE-2025-58180 is a critical remote code execution vulnerability (CVSS 7.5) in OctoPrint versions ≤ 1.11.2 (patched in 1.11.3, released September 2025)....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067