Third-Party Risk Red Teaming: Attacking Through Vendors and Partners
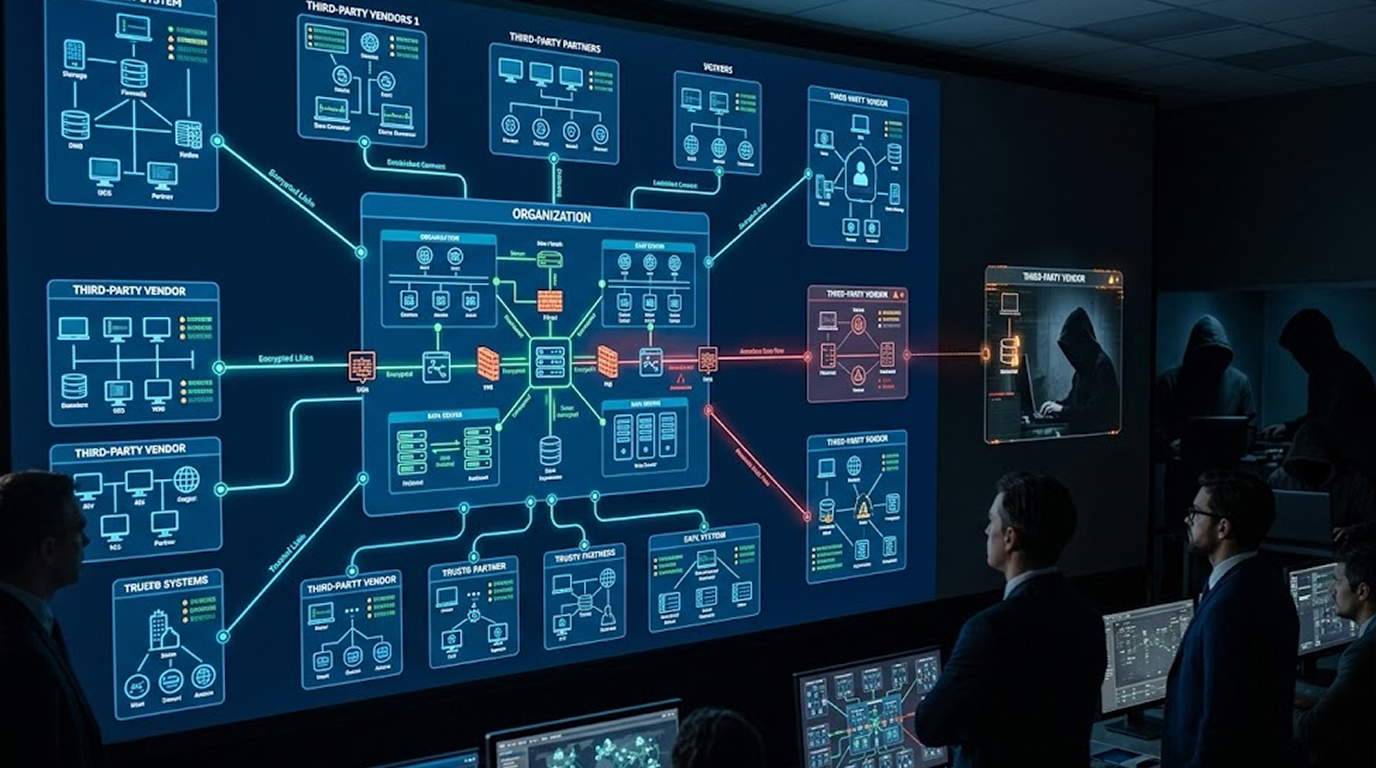
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
Found 152 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
While many organizations are placing high levels of effort into securing their own perimeter, attackers are increasingly finding new ways to bypass perimet...
Google has officially made available Device Bound Session Credentials (DBSC) for all Windows users using Chrome v146! This is a significant development in...
Your business relies on service accounts. They connect your website to email platforms, your CRM to marketing tools, your cloud storage to backup systems....
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
One of the best ways to identify early-stage intruders (i.e., stalking while still being able to gain access to valuable information) is through the use of...
All three techniques are still responsible for a huge portion of account takeovers in 2026, but the balance has shifted noticeably over the last two years....
When you see clear signs that ransomware is spreading inside your network (multiple machines encrypting files, ransom notes appearing, abnormal process cha...
Cybersecurity researchers at OX Security have disclosed four serious vulnerabilities across hugely popular Visual Studio Code extensions, collectively inst...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067