Laravel Lang PHP Supply Chain Attack Steals Credentials
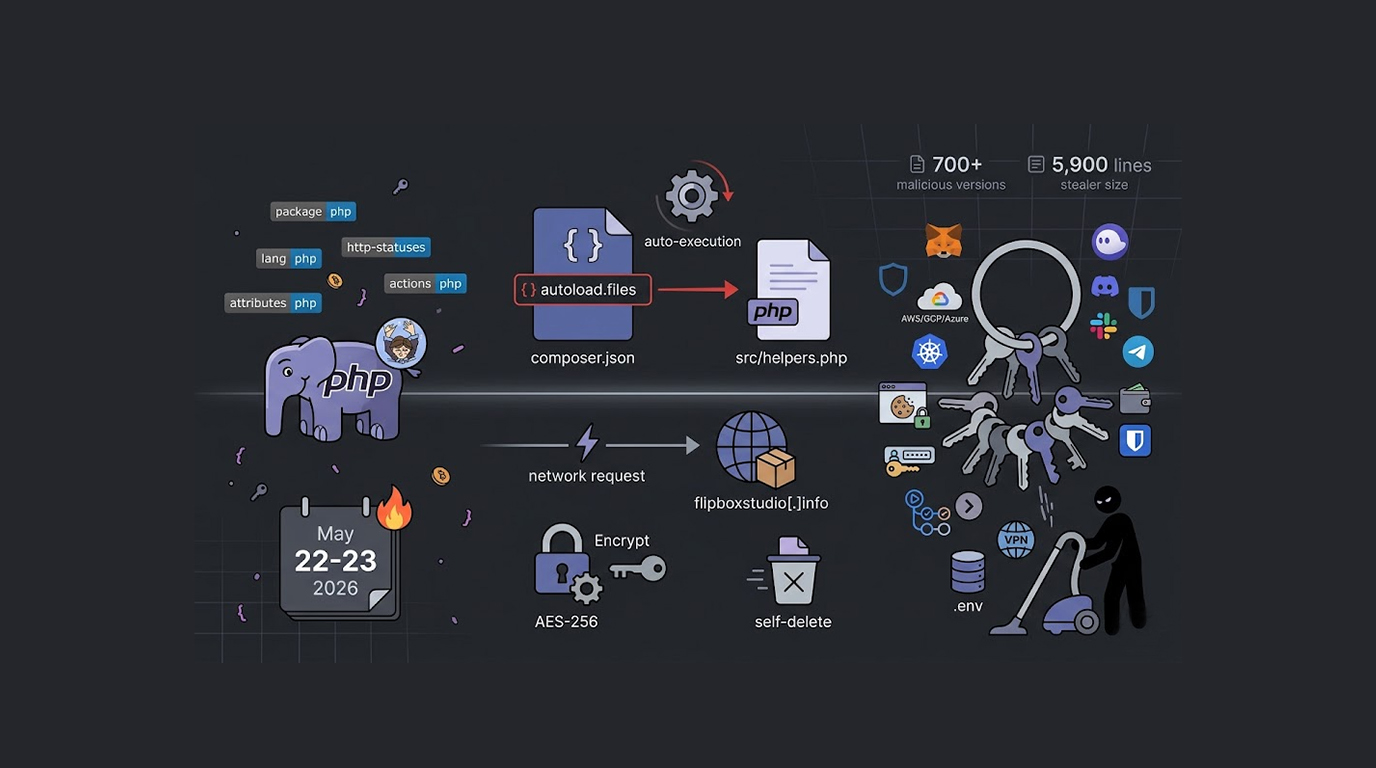
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
Found 81 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
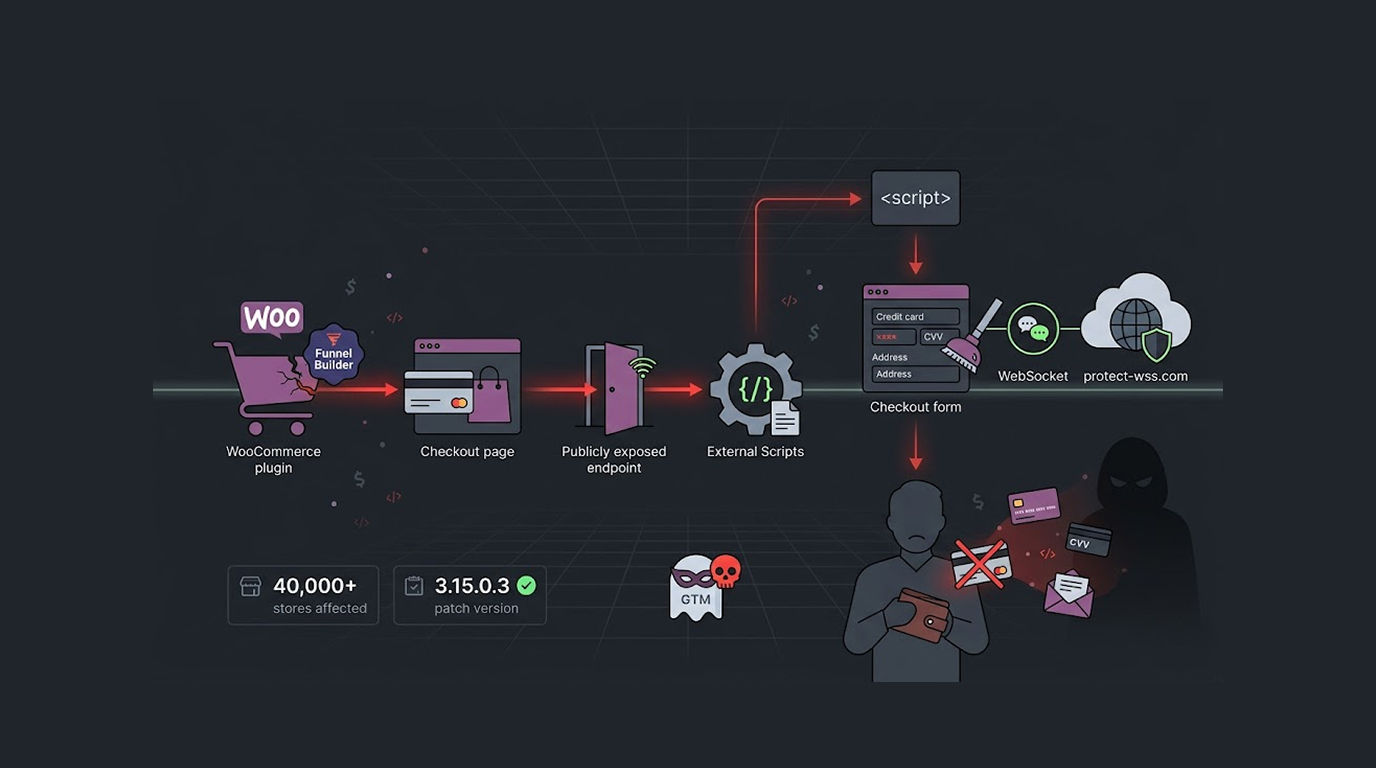
A critical security vulnerability in the Funnel Builder plugin for WordPress is under active exploitation, and attackers are using it to inject malicious J...
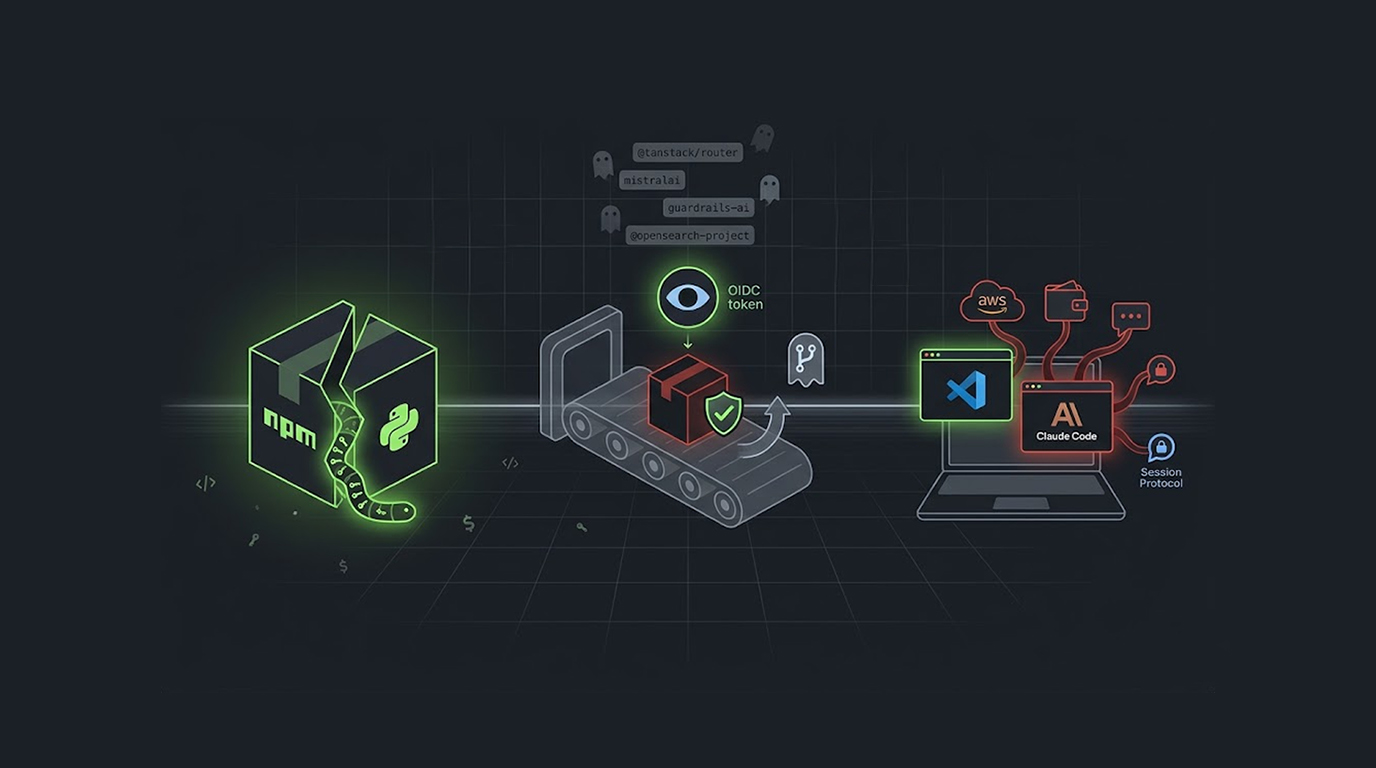
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
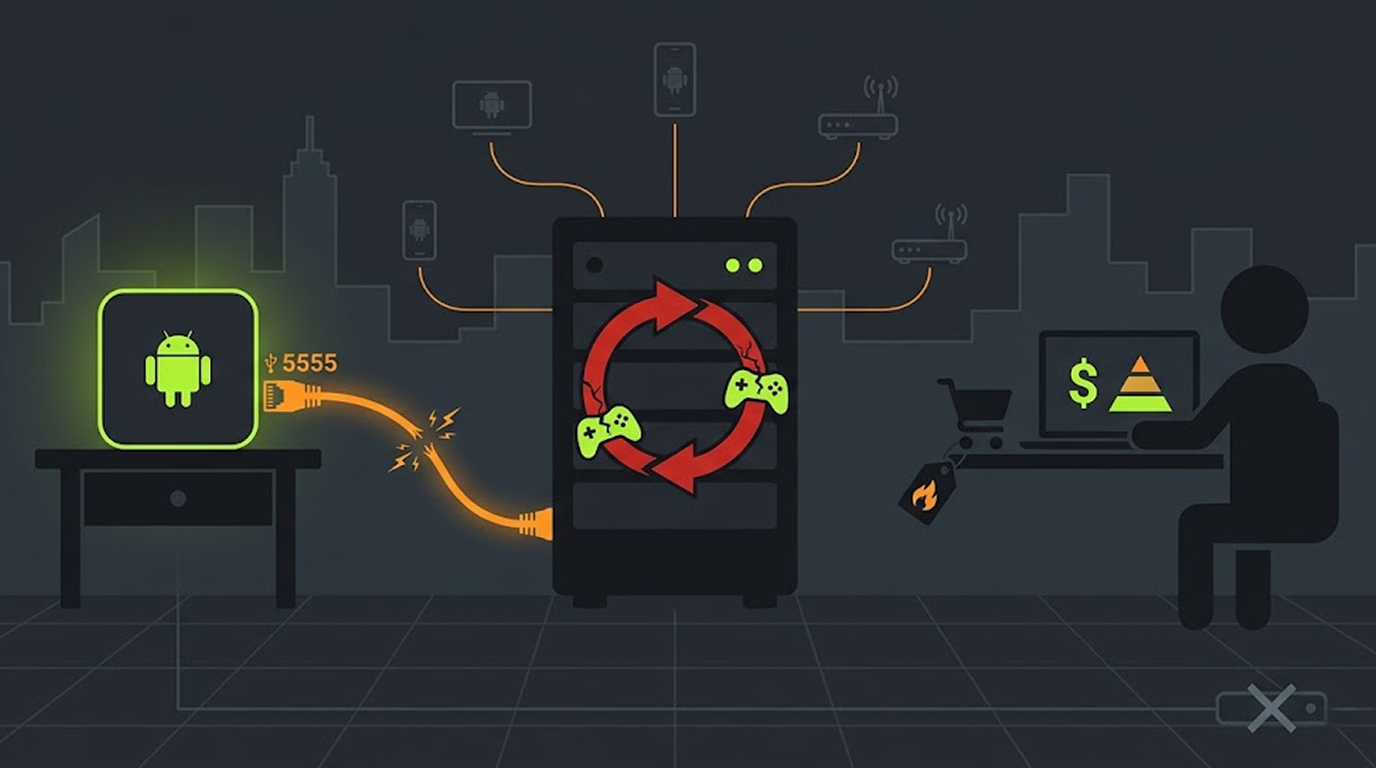
Your Android TV box or smart TV could be part of a DDoS army right now. And you would never know.Security researchers at Hunt.io have uncovered a new Mirai...
You run npm install. Packages download. Dependencies resolve. The terminal shows a success message.Behind the scenes, postinstall.js executes automatically...
A single 732-byte Python script. Four controlled bytes. And root access on virtually every Linux machine shipped since 2017. That is the reality of Copy F...
Open source security just got another wake up call. A self propagating worm has been quietly compromising npm packages, and its goal isn’t just to st...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067