OpenSSF Package Analysis: Free Malware Scanner for Packages
There is an increase in supply chain attacks against open-source packages in 2026. Hackers or other malicious actors will either publish or compromise pack...
Found 59 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is an increase in supply chain attacks against open-source packages in 2026. Hackers or other malicious actors will either publish or compromise pack...
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
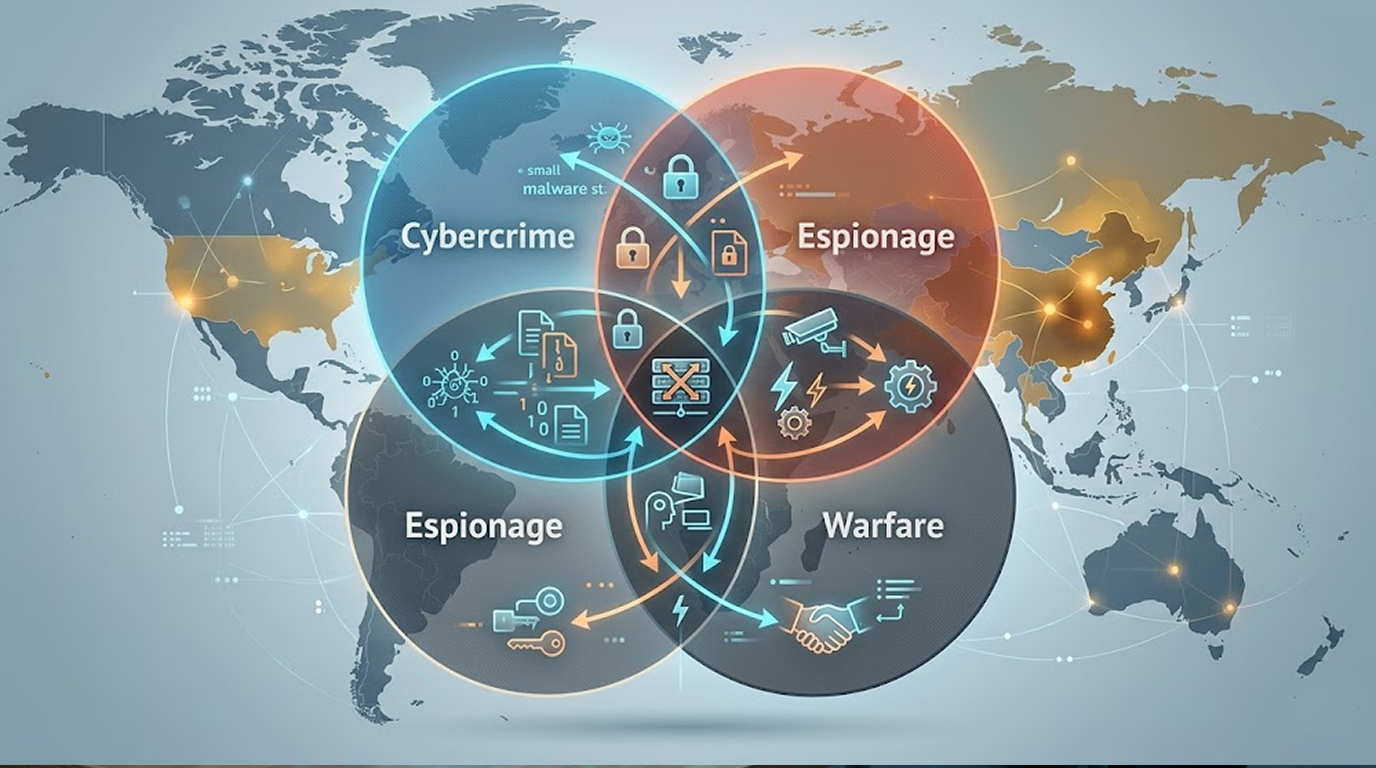
In 2026, the borders which had once separated different areas of cybercrime from government sponsored spying and that of cyber warfare is becoming less dis...
When an incident like this happens and your website is down, no way for customers to check out and Google is displaying scary security warnings. In 2025 (a...
The modern reality is that geopolitical tensions are increasingly being played out through cyber-attacks, which can impact everyday citizens. The year 2026...
Cybersecurity firm Socket has uncovered an active supply-chain worm campaign codenamed SANDWORM_MODE that abuses at least 19 malicious npm packages to harv...
The defense industrial base (DIB), companies that design, build, and support military systems , remains one of the most intensely targeted sectors in globa...
Free and open-source software (FOSS) powers most of the internet, mobile devices, servers, cloud infrastructure, IoT products, and even many proprietary ap...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067