CISA Adds 2 Exploited Roundcube Flaws to KEV Catalog
CISA has updated its Known Exploited Vulnerabilities (KEV) catalogue, which now contains two vulnerabilities in Section Four of the Roundcube webmail softw...
Found 562 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
CISA has updated its Known Exploited Vulnerabilities (KEV) catalogue, which now contains two vulnerabilities in Section Four of the Roundcube webmail softw...
TikTok can kill your visibility almost instantly if someone knows how to “poison” the algorithm against you. It’s not a hack, not a ban,...
This is one of the most effective and low-risk ways people (competitors, disgruntled ex-employees, jealous creators, or coordinated groups) permanently kne...
The fastest way attackers permanently destroy a brand’s entire social media presence isn’t hacking every account individually , it’s comp...
The message “Error 404: Page Not Found” is something we all see daily on websites. But when an entire business or critical parts of it suddenly...
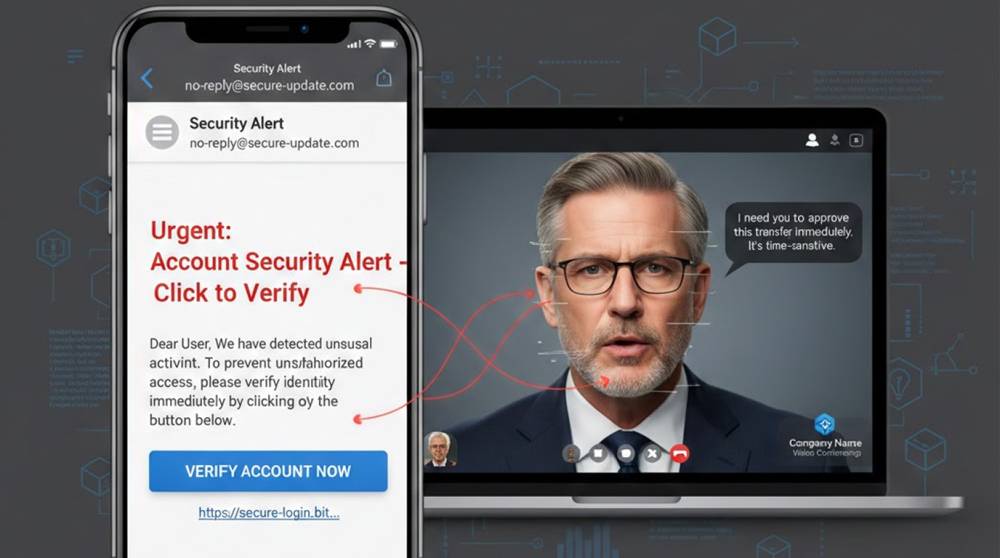
Criminals and state entities are currently applying AI to execute assaults on individuals and businesses. This has been done in a well-known manner through...
There's a new commercially available spyware platform for sale and advertised through Telegram called ZeroDayRAT. It comes with everything someone might ne...
Agentic AI systems (autonomous agents, tool-calling LLMs, multi-step reasoning chains, etc.) interact with external APIs hundreds or thousands of times dur...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067