Malicious npm Packages Used in Targeted Credential Theft Campaign
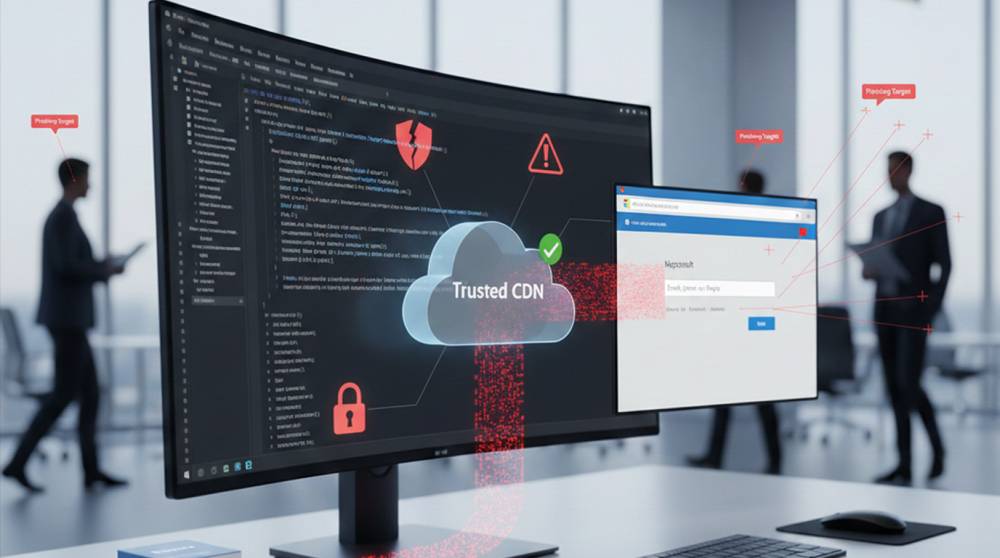
Cybersecurity experts have identified an ongoing, organized phishing campaign that used the npm platform to gain access to thousands of companies’ us...
Found 25 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity experts have identified an ongoing, organized phishing campaign that used the npm platform to gain access to thousands of companies’ us...
It might surprise some developers, but even widely used packages can turn rogue. These are small libraries or dependencies that, intentionally or after bei...
Cybersecurity researchers have taken a closer look at a deceptive npm package that appears to be experimenting with a new trick: nudging AI-powered securit...
North Korea’s malware operation targeting developers hasn’t slowed down. In fact, it’s grown noticeably louder. Security researchers have...
Cybersecurity researchers are raising alarms over a supply chain attack targeting the popular npm package @solana/web3.js, widely used by Solana developers...
A recent malware campaign targeting the npm (Node Package Manager) repository has raised alarms within the open-source ecosystem. Malicious packages are ac...
Cybersecurity researchers have recently uncovered several suspicious packages in the npm registry designed to steal Ethereum private keys and gain remote a...
Roblox developers are facing a persistent cyber threat aimed at compromising systems through fake npm packages. Cybersecurity firm Checkmarx has reported t...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067