Cross-Site Scripting (XSS) Attacks: How They Work and How to Defend Against Them
Cross-Site Scripting (XSS) attacks are among the most common and dangerous types of security vulnerabilities found in web applications. XSS attacks occur w...
Found 88 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cross-Site Scripting (XSS) attacks are among the most common and dangerous types of security vulnerabilities found in web applications. XSS attacks occur w...
In the vast realm of cybersecurity, hackers play diverse roles, each with distinct motivations, methods, and impacts. Understanding the different types of...
The advent of 5G technology represents a groundbreaking leap in connectivity, promising to revolutionize how we communicate, interact, and conduct business...
A state-sponsored cyber espionage campaign, codenamed Crimson Palace, has been observed expanding its operations across Southeast Asia, compromising govern...
As industrial robots become increasingly integral to modern manufacturing and production processes, ensuring their cybersecurity has become a critical conc...
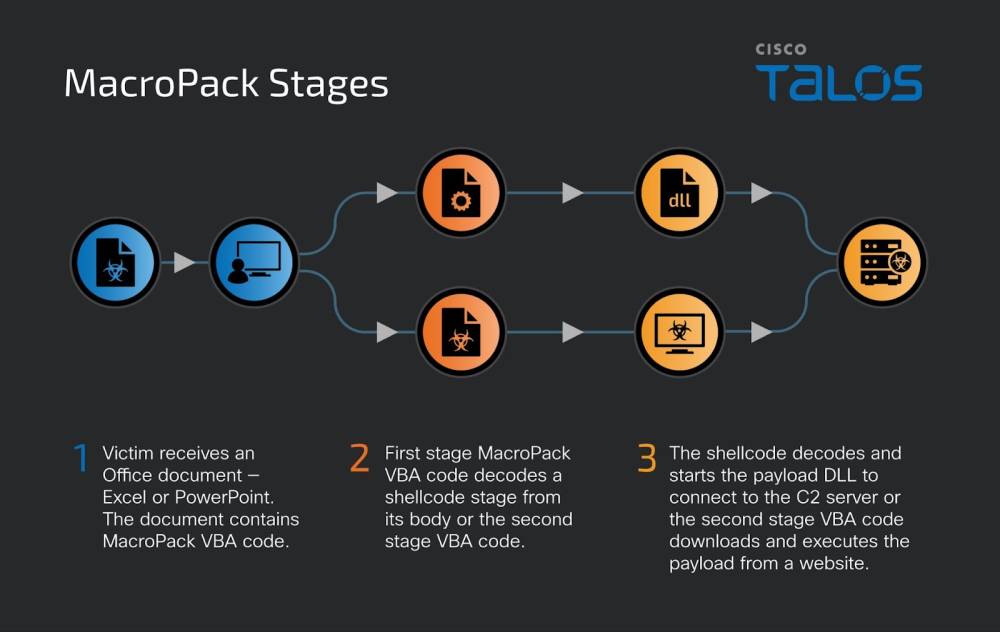
Threat actors are utilizing a red-teaming tool called MacroPack to serve malware payloads, according to recent findings from Cisco Talos. Originally design...
Cybersecurity is often viewed through the lens of technology—firewalls, encryption, and antivirus software. However, the human element plays a crucia...
In this comprehensive video tutorial, we explore the realms of cybersecurity and ethical hacking, centering our focus on Whonix an influential anonymity-ce...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067