RAG Poisoning: AI's Biggest Security Blind Spot
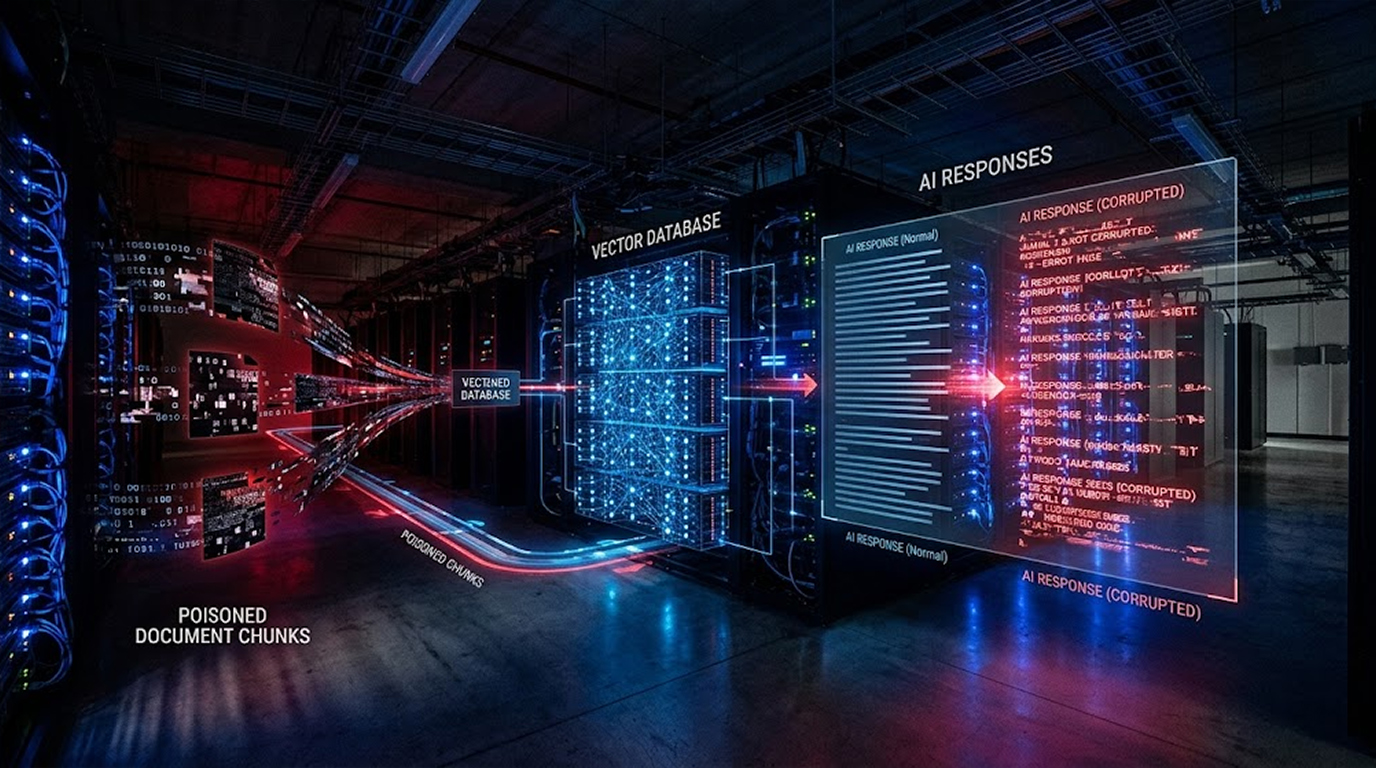
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
Found 28 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
When you think about web security, CSS is probably the last thing on your mind. It is just styling, right? Colors, fonts, layouts. What could possibly be d...
This is one way an attacker can use to exploit websites. The dangling-byte technique is a new and innovative approach to HTTP desync that enables an attack...
PortSwigger's James Kettle has built an AI-assisted research system called HTTP Terminator that generated and proved new HTTP desynchronization techniques...
You have a web app that you want to test. Maybe it is a customer portal, an API, or a full-blown SaaS platform. You know you need a security tool, but the...
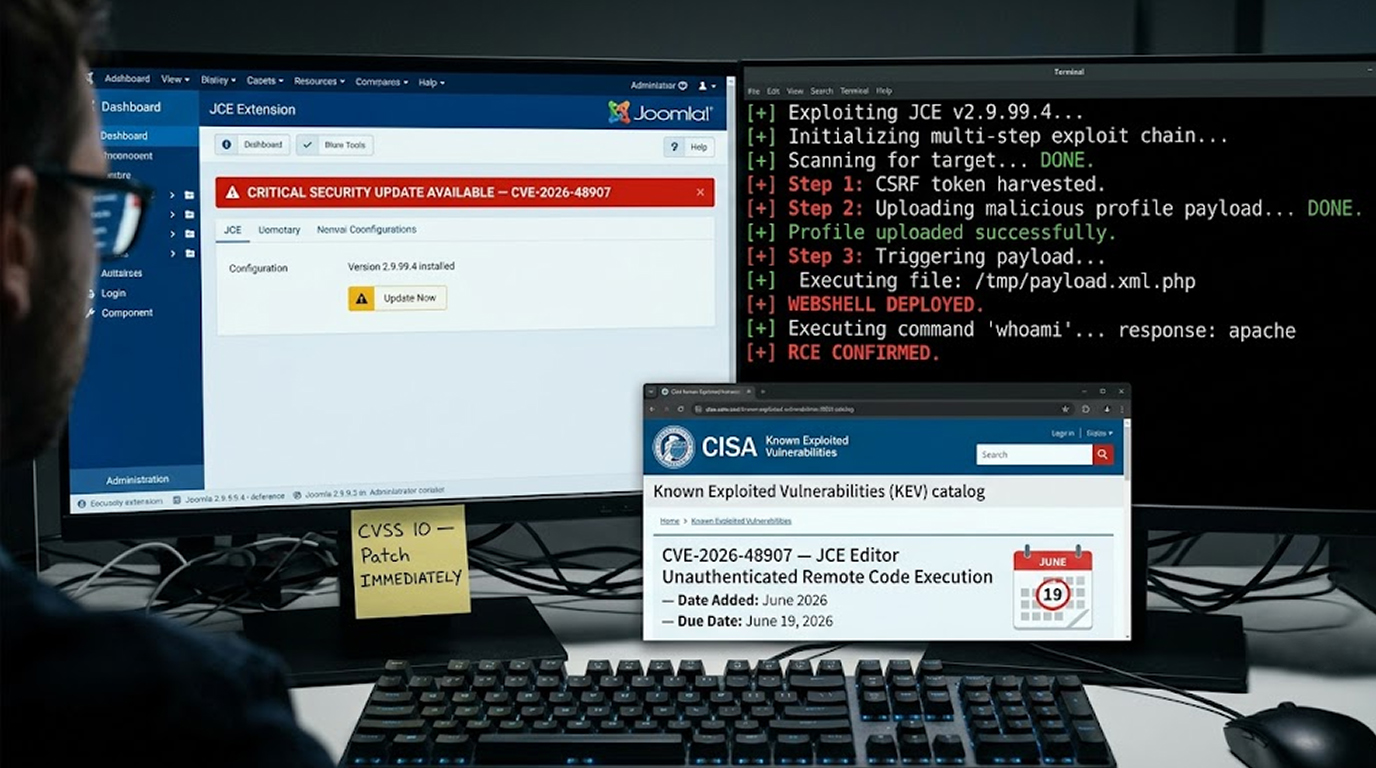
The U.S. Cybersecurity and Infrastructure Security Agency just added a maximum-severity flaw to its Known Exploited Vulnerabilities catalog. Federal agenci...
As the cybersecurity industry continues to advance at an accelerated pace, new vulnerabilities pose increased potential for both rewards and risk by being...
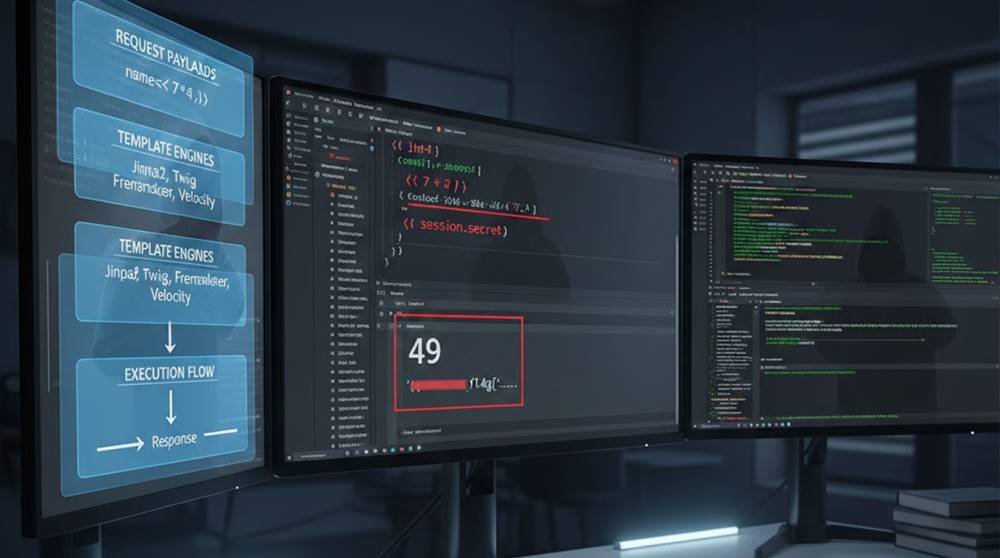
Template engines power:1. Login pages2. Email templates3. Error messages4. Admin dashboardsWhen user input is rendered inside templates without proper hand...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067