GitLab CVE-2026-110264: Unauthenticated RCE Patch
Your self-managed GitLab server might be accepting remote code execution from anyone who sends the right request, because GitLab just released emergency fi...
Found 15 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your self-managed GitLab server might be accepting remote code execution from anyone who sends the right request, because GitLab just released emergency fi...
Here's a fun one. ILIAS has two endpoints that don't require authentication. One of them writes to your session. The other one reads your session back and...
If you're running Forminator Forms on your WordPress site, you need to update right now. A researcher found a way for anyone to upload malicious files with...
A maximum severity level vulnerability was detected in SAP Commerce Cloud, for which patches have been released by SAP. The vulnerability would allow arbit...
A security researcher has published an exploit for a critical OS command injection flaw in CorgetGpsDget. The vulnerability is in the GPS application and e...
A critical unauthenticated remote code execution vulnerability in the JCE extension for Joomla has been exploited. A public proof-of-concept is now availab...
A critical severity vulnerability in the Progress Kemp LoadMaster load balancer has been added to CISA’s Known Exploited Vulnerabilities list. The ad...
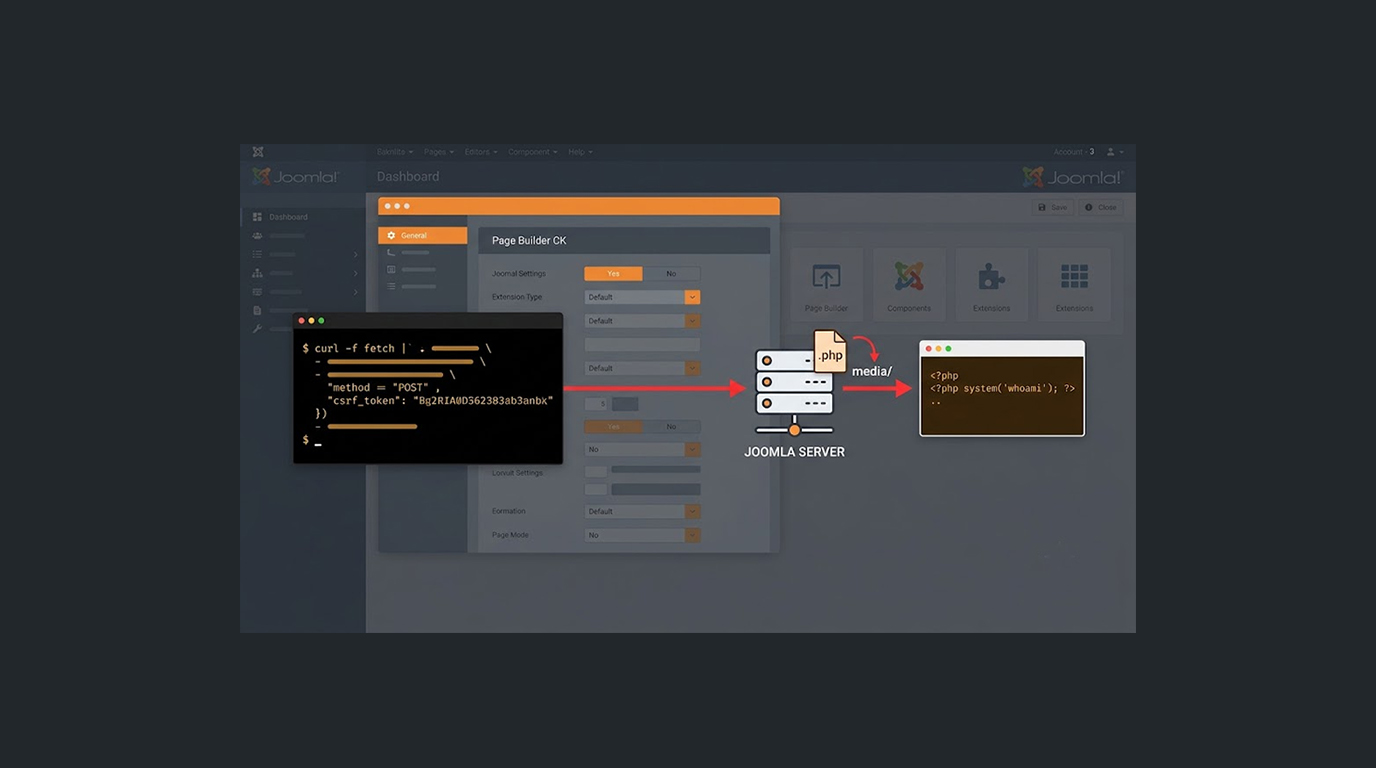
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067