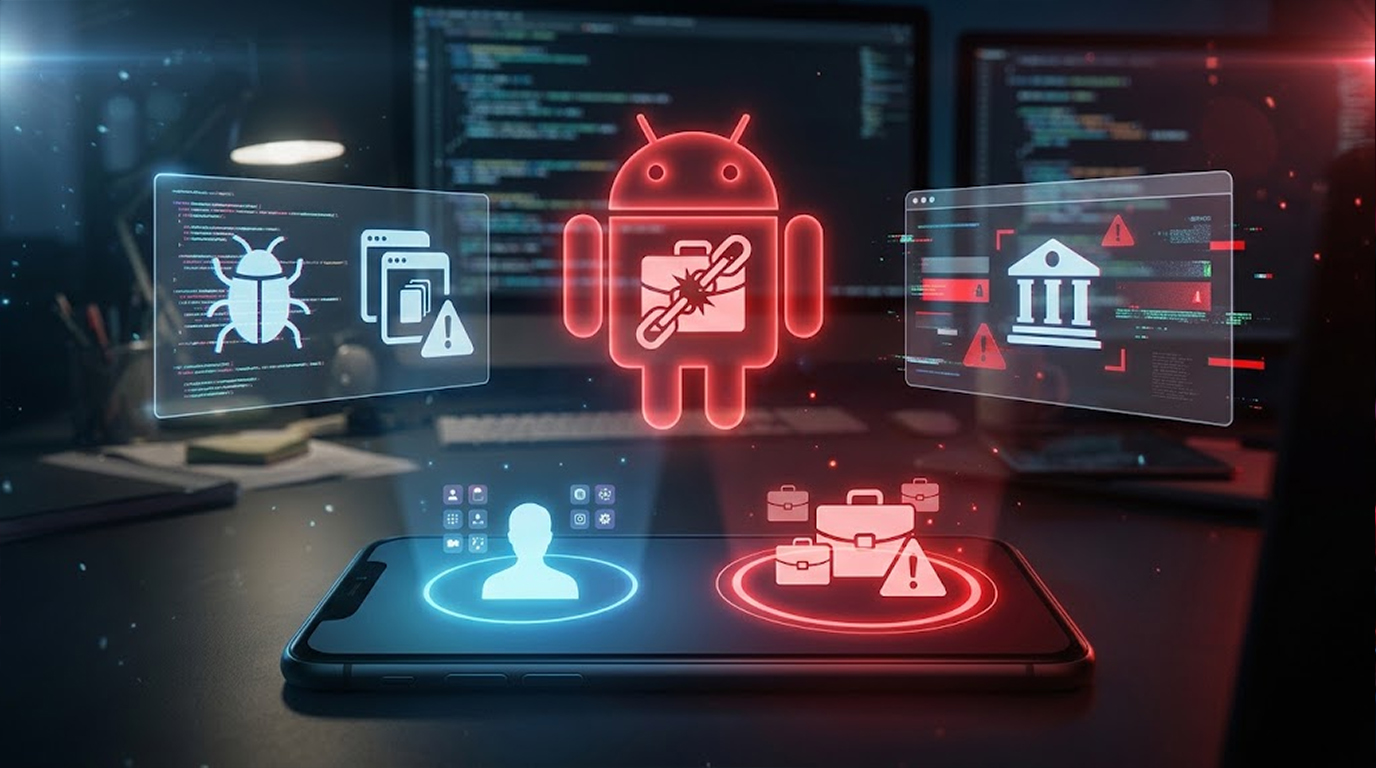
A banking trojan called Gigabud has found a sneaky new way to avoid detection. It installs a second Android app that creates a work profile on your phone and drops a fake banking app inside it. The whole point is to hide from the real banking app's security checks.
Group-IB published a report on September 9 detailing the technique. The Hacker News covered the findings. The short version: the bad guys have figured out how to use a legitimate Android feature as a hiding place.
Let me break down how this works.
Quick Summary
|
What |
Details |
|
Trojan |
Gigabud (remote access trojan) |
|
New Tactic |
Work profile evasion |
|
Second App |
Vwork (based on Shelter) |
|
Confirmed In |
Indonesia |
|
Losses |
~$960,000 estimated |
|
Attribution |
GoldFactory |
What Is a Work Profile?
Android has a feature called a work profile.It creates a space on your phone which you use only for applications of your employers. Everything within a work profile remains separated from everything else on your phone.
Think of it like a locked box inside your phone. Your personal stuff is outside. Work stuff is inside. They don't mix.
That separation is supposed to be a good thing. But Gigabud is using it against you.
How Gigabud Hides
Here's the trick. Banking apps often carry security code that scans your phone for known malware. But that scan only looks in your personal space. It can't see inside a work profile.
So Gigabud does this:
- It infects your phone (more on how later).
- It installs a second app called Vwork.
- Vwork creates a work profile.
- Vwork drops a tampered banking app inside that profile.
Now the real banking app's malware scan can't see the fake one. The fake app sits in its own little bubble, hidden from security checks.
"The work profile hides the trojan from the banking app's own malware checks," Group-IB said. "A fraudulent payment can look unrelated to the alert already raised on the phone."
That's the core of the trick. It's clever, and it's concerning.
What Is Gigabud?
Gigabud is a remote access trojan (RAT). That means it gives the attacker live control over your phone. It's been active since 2022. Group-IB links it to a group called GoldFactory.
How It Gets In:
GoldFactory spreads the Gigabud through apps that pretend to be legitimate services. They impersonate:
- National airlines
- Tax offices
- Government portals
You install them from outside the official app store. Once installed, the app asks for three permissions:
- Accessibility access
- Permission to draw over other apps
- Permission to keep running in the background
The Accessibility permission is the key. Once you grant it, the operator has real control.
What It Does Once Installed:
- Sends a list of every app on your phone to the operator
- Identifies which banking apps you use
- Shows a fake login screen over your real banking app
- Captures your keystrokes
- Takes your lock screen code with an invisible overlay
- Runs transactions on your phone while a black screen covers the activity
It's a full takeover.
What Is Vwork?
Vwork is the second app. It's the one that creates the work profile and manages the fake banking app.
Group-IB found that Vwork's architecture and class names match Shelter, an open-source tool that lets phone owners isolate or duplicate apps using work profiles. Shelter is meant to be used by hand, by the person holding the phone. Vwork opens the same functions to other apps.
The Difference:
- Shelter: You control it. You set up the profile. You choose which apps to clone.
- Vwork: Any app on the device can control it. Set up a profile, clone an app, list what's inside, open an app. No user involvement.
Group-IB said the security checks that stopped other apps from calling those functions have been removed. So any app can drive Vwork.
Before it clones anything, Vwork asks an external server for permission. Gigabud carries commands written specifically for it.
Shelter walks you through several screens before creating a profile. Vwork cuts it down to a single prompt, written in Chinese.
The Indonesian Chain
Group-IB confirmed the full attack chain on infected devices in Indonesia. The installs arrived in order:
- Gigabud first
- Vwork within minutes
- The tampered banking app
In the one case described in detail, the app that went into the work profile wasn't a duplicate of the victim's real banking app. It was a fake version of a real Indonesian bank's app.
The Numbers:
- Between February and July 2026, Group-IB counted:
- About 1,469 compromised devices in Indonesia
- 1,281 possibly compromised logins
- Estimated losses of about $960,000
Those are just the cases Group-IB observed. The real number could be higher. Group-IB didn't say how many of those devices had Vwork installed.
Gigabud samples built to work with Vwork have been found targeting Brazil, Colombia, Egypt, Indonesia, Laos, Mexico, Morocco, the Philippines, Thailand, Türkiye, and one Gulf Cooperation Council country. But those are samples, not confirmed infections. Only the Indonesian chain is confirmed.
How to Check Your Phone for a Work Profile
If you're worried, you can check if your phone has a work profile. Here's how:
- Open Settings.
- Tap Passwords and accounts.
- Look for a Work tab. If it's there, your phone has a work profile.
- Apps inside a work profile show a small briefcase badge on their icons.
To delete it:
- Open the Work tab.
- Choose Remove Work Profile.
- Tap Delete.
Google says this removes everything stored inside the profile.
- One more thing: Check that the app that set up the profile is gone. Group-IB said Vwork keeps its icon out of the app launcher, but it still shows up in a file manager.
- Important: These steps assume the phone belongs to you. You can't remove a profile an employer owns. Group-IB's report doesn't say whether deleting the profile ends the risk while Gigabud is still installed in your personal space.
What Banks Should Watch For
Group-IB listed signs that banks can look for. These are behaviors, not known malware files:
- A work profile appearing on an ordinary consumer phone that nobody set up
- The same banking app showing install markers in both profiles
- A profile holding none of the apps a person would normally have
- Accessibility switched on for an app with no reason to need it
Those are red flags.
The Bigger Picture
Using a container to hide a banking app isn't new. Promon described FjordPhantom in 2023. It ran a real banking app inside a virtual container so it could change how the app behaved from the inside. That worked by breaking the wall Android puts between apps.
Vwork does the opposite. It uses a wall Android already provides the work profile to put the trojan beyond the checks that would normally catch it.
It's a clever twist on an old idea.
What Should You Do
1. Download Apps from Official Stores Only
Sideloaded apps are a primary infection vector. Stick to Google Play.
2. Refuse Accessibility Access
If an app asks for Accessibility access and it's not an accessibility tool, deny it. That's the permission Gigabud needs most.
3. Use a Second Factor That Isn't SMS
SMS codes can be intercepted. Use an authenticator app or a hardware key for banking.
4. Check for Work Profiles
If you didn't set one up, and your phone isn't managed by an employer, a work profile is suspicious.
5. Report Suspicious Activity
If you think you've been infected, contact your bank and report it.
The Bottom Line
Gigabud has a new trick. It uses Android's work profile feature to hide a fake banking app from security checks. Group-IB confirmed the chain in Indonesia. The technique is still under development, but it's a sign of things to come.
What You Need to Know:
|
Key Point |
Detail |
|
Trojan |
Gigabud |
|
New Tactic |
Work profile evasion |
|
Second App |
Vwork |
|
Confirmed In |
Indonesia |
|
Losses |
~$960,000 |
|
Attribution |
GoldFactory |
What You Need to Do:
- Install apps only from official stores
- Refuse Accessibility access to non-accessibility apps
- Use a second factor that isn't SMS
- Check for unexpected work profiles
- Report suspicious activity
FAQ Section
What is Gigabud?
Gigabud is a RAT for Android mobiles that provides attackers with direct control over the device. Detection of Gigabud took place in 2022 and is connected to the GoldFactory group.
How does the work profile trick work?
Gigabud installs a second app called Vwork. Vwork creates a work profile and drops a fake banking app inside it. Since the real bank app’s malware scan cannot access the work profile, the faket application remains undetected.
What is Vwork?
Vwork is a modified version of Shelter, an open-source tool for isolating apps using work profiles. Unlike Shelter, Vwork can be controlled by any app on the device, not just the user.
How can I verify whether my phone has a work profile?
Open Settings, then Passwords and accounts. If there's a Work tab, your phone has a work profile. Apps inside it show a briefcase badge.
What should I do if I find a suspicious work profile?
Remove it. And then see whether the app that created this is installed. You may even think about doing a security scan and getting in touch with your bank.